の検索結果 :
×の検索結果 :
×Blazor SAML シングルサインオン (SSO)アプリケーションを使用すると、Blazor アプリケーションで SAML シングルサインオンを有効にできます。シングルサインオンを使用すると、1 つのパスワードだけで Blazor アプリケーションとサービスにアクセスできます。このアプリケーションは、すべての SAML 準拠の ID プロバイダーと互換性があります。ここでは、PingFederate を ID プロバイダーとして、Blazor と PingFederate 間でシングルサインオン (SSO) を構成する手順を順を追って説明します。Blazor SSO で提供される機能の詳細については、こちらをクリックしてください。
      using miniorange.saml
      public class Startup
      {
        public void ConfigureServices(IServiceCollection services)
        {

         services.AddAuthentication(CookieAuthenticationDefaults.AuthenticationScheme).AddCookie();
         services.AddControllersWithViews();
        }
        public void Configure(IApplicationBuilder app, IHostingEnvironment env, ILoggerFactory loggerFactory)
        {
          app.UseHttpsRedirection();
          app.UseRouting();
          app.UseAuthorization();
          app.MapRazorPages();

          app.UseCookiePolicy();
          app.UseAuthentication();
          app.UseStaticFiles();
          app.UseminiOrangeSAMLSSOMiddleware();
          app.Run();
        }
      }
      using Microsoft.AspNetCore.Authentication.Cookies;
      using miniOrange.saml;

      var builder = WebApplication.CreateBuilder(args);

      builder.Services.AddRazorPages();
      // Add authentication services
      builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());

      var app = builder.Build();

      if (!app.Environment.IsDevelopment())
       {
          app.UseExceptionHandler("/Error");

          app.UseHsts();
       }

      app.UseHttpsRedirection();
      app.UseRouting();
      app.UseAuthorization();
      app.MapRazorPages();

      app.UseCookiePolicy();
      app.UseAuthentication();
      app.UseStaticFiles();
      app.UseminiOrangeSAMLSSOMiddleware();
      app.Run();
      app.useantiforgery();
https://<blazor-application-base-url>/?ssoaction=config

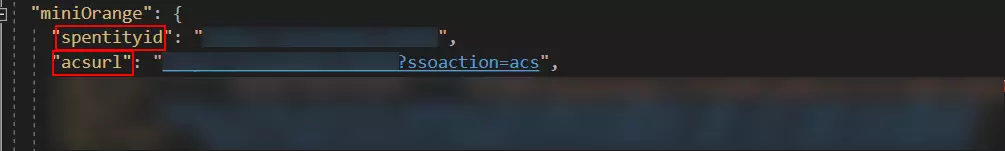
SAML SP メタデータを取得して ID プロバイダー側で構成するには、以下に 2 つの方法を詳しく説明します。
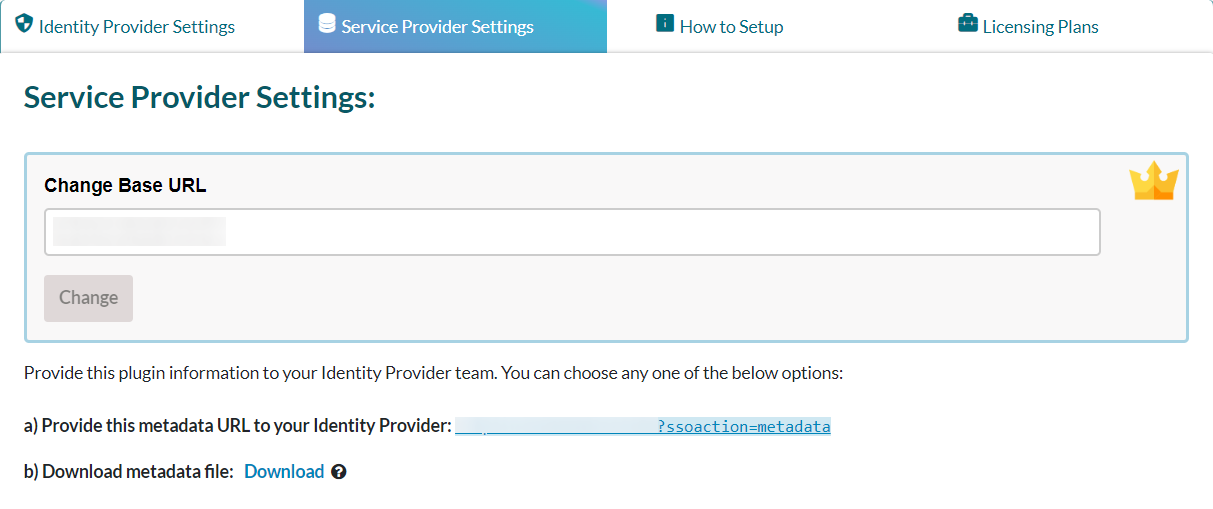
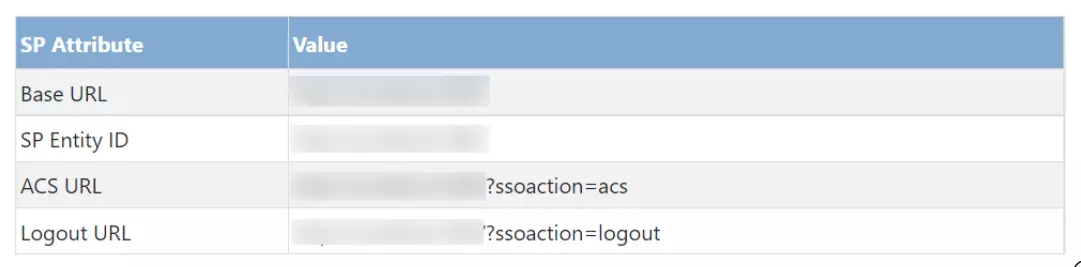


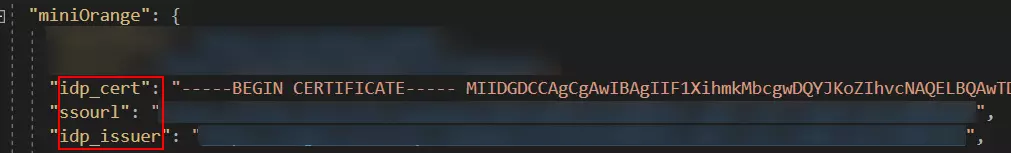
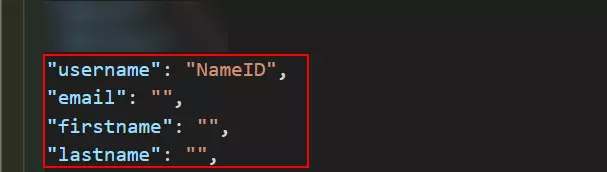
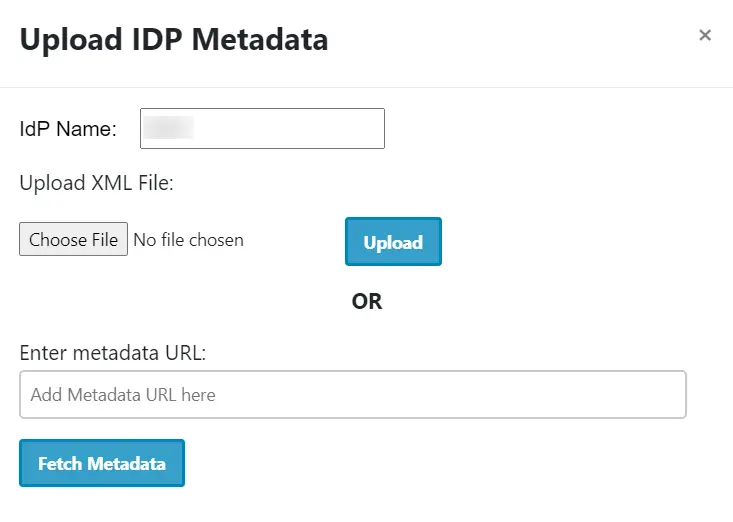
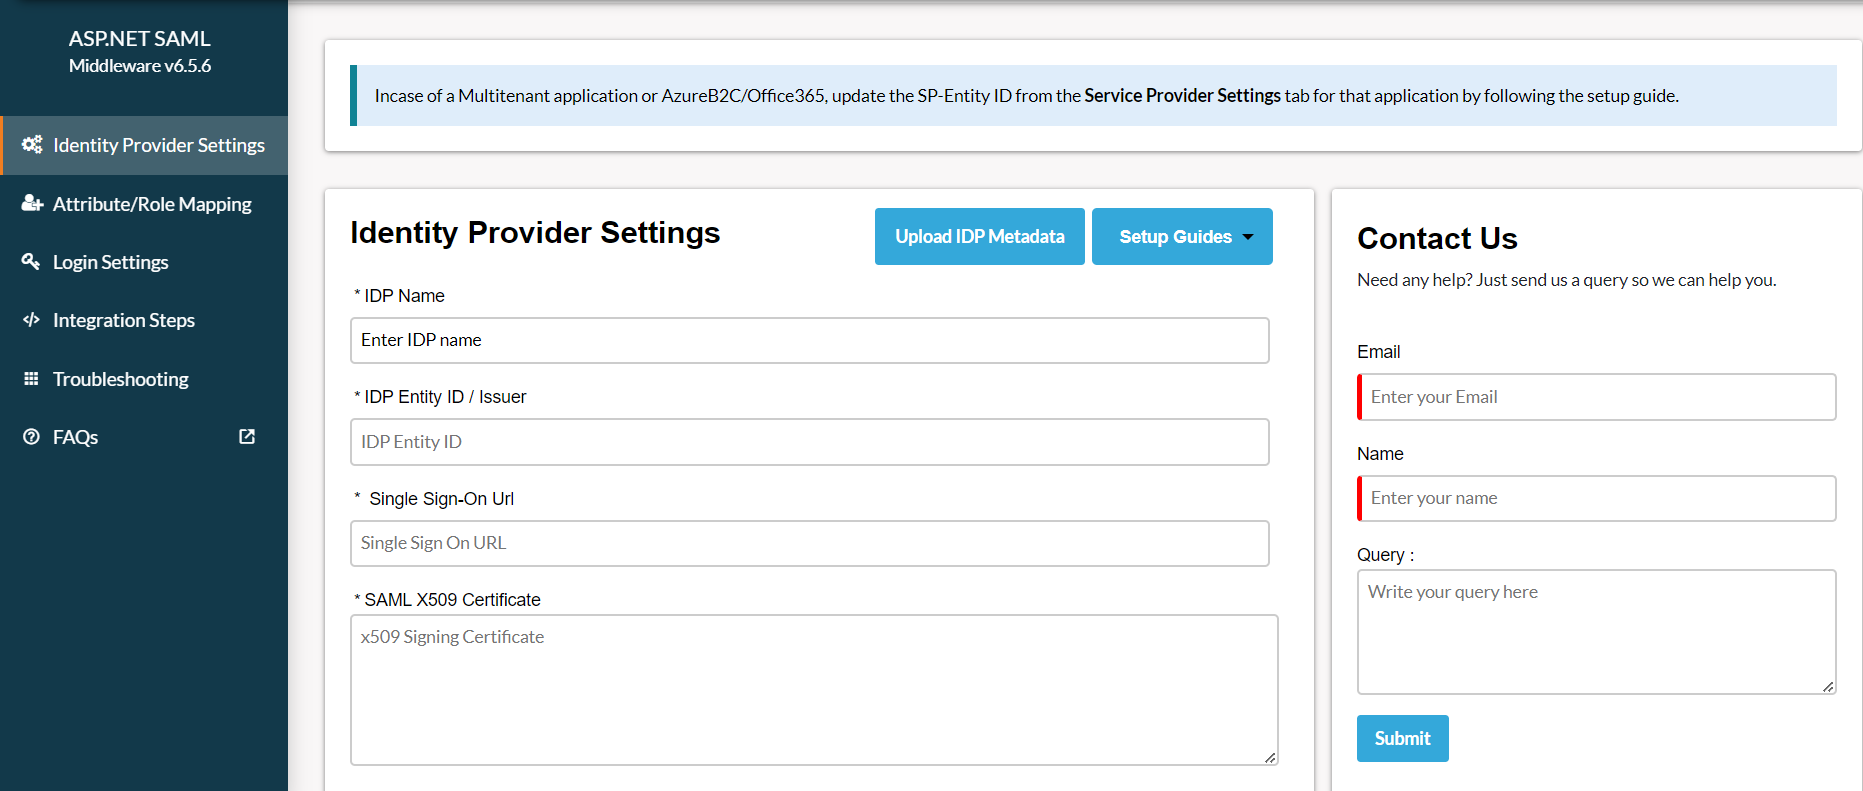
アプリケーションで SAML ID プロバイダーのメタデータを構成するには、以下に説明する 2 つの方法があります。
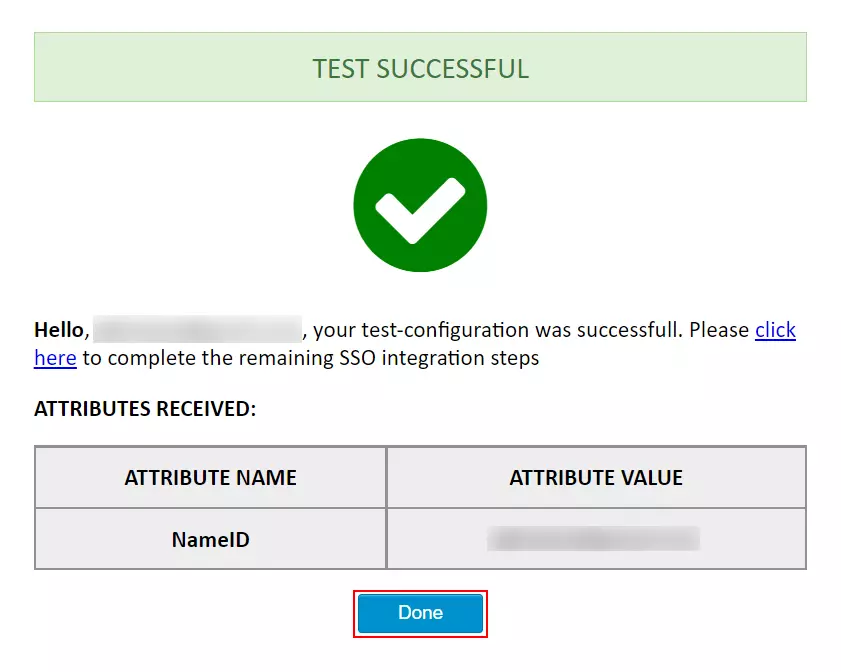
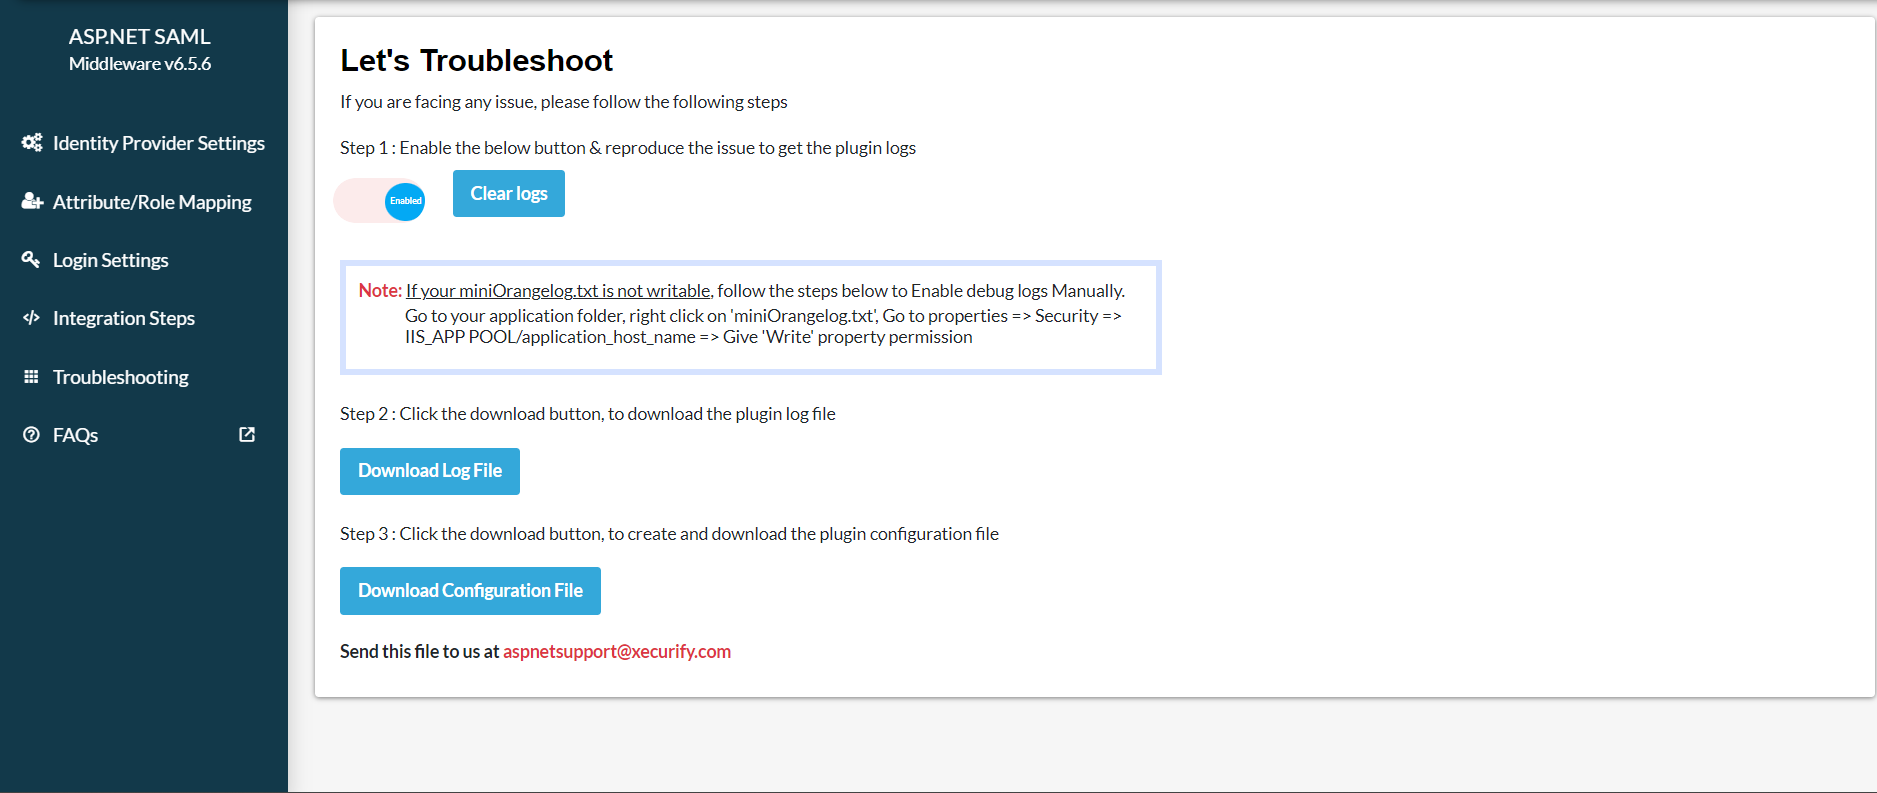

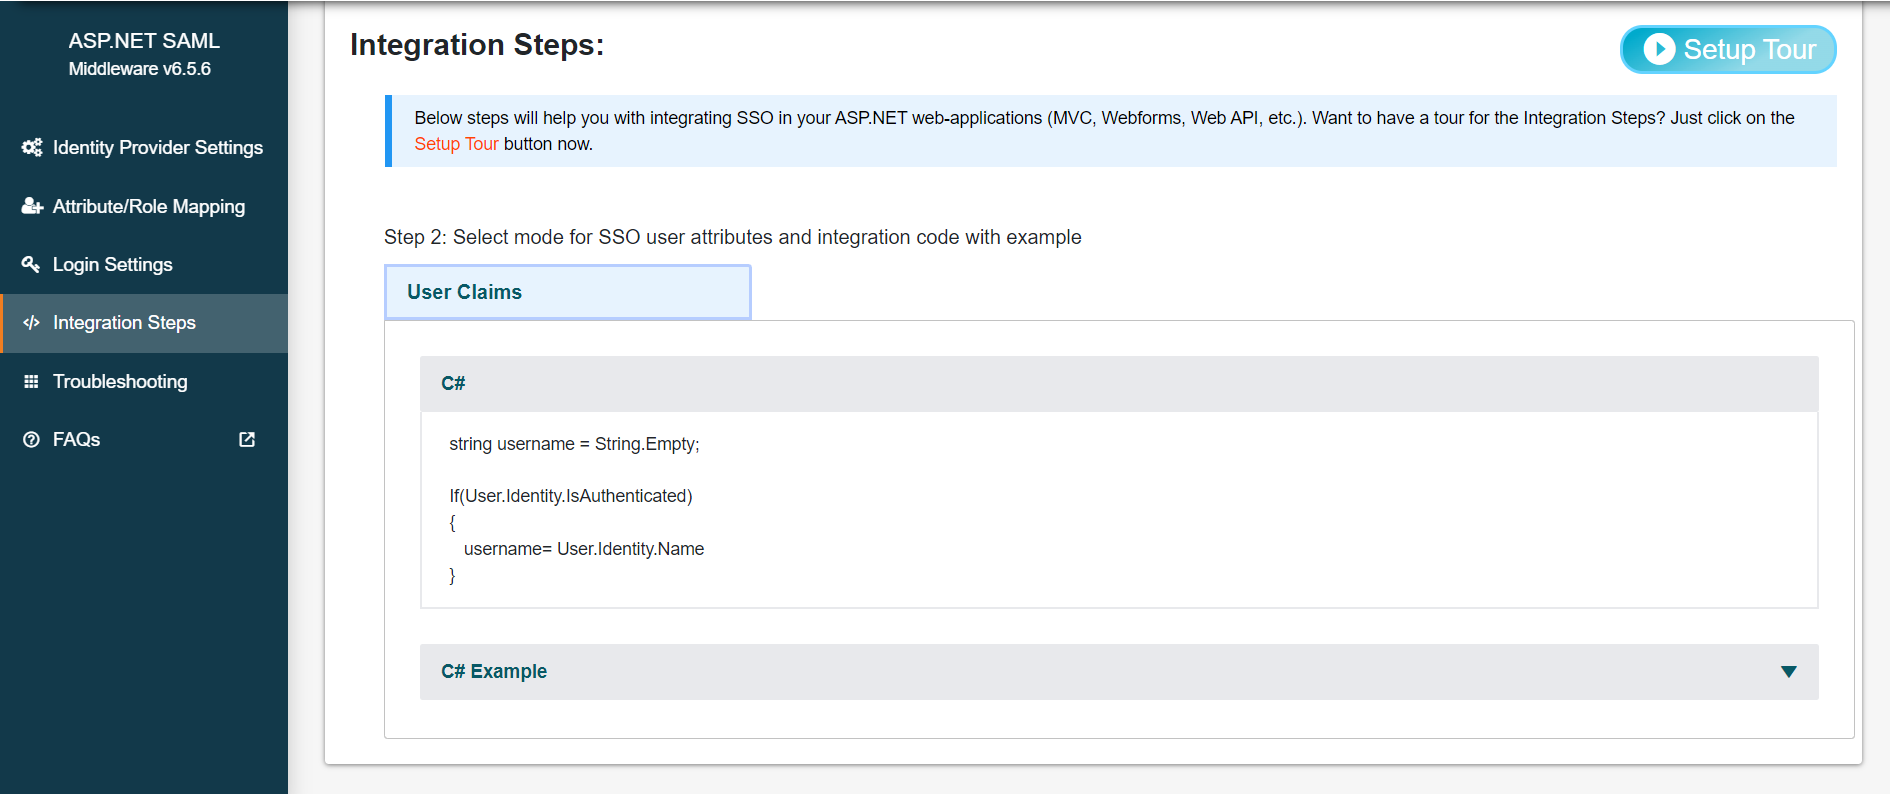
    string name="";
    string claimtype="";
    string claimvalue="";

     if(User.Identity.IsAuthenticated)
     {
       foreach( var claim  in User.Claims)
       {
         claimtype = claim.Type;
         claimvalue = claim.Value;
       }
       retrive custom attributes(for eg. Retrieve Mapped 'mobileNumber' attribute of your IDP)
       var identity = (ClaimsIdentity)User.Identity;
       IEnumerable claims = identity.Claims;
       string mobileNumber = identity.FindFirst("mobileNumber")?.Value;
     }

https://blazor-application-base-url/?ssoaction=login
<a href=”https://blazor-application-base-url/?ssoaction=login”>Log
            in</a>
https://blazor-application-base-url/?ssoaction=logout
<a href=”https://blazor-application-base-url/?ssoaction=logout”>Log
            out</a>
Blazor SAML 2.0 シングルサインオン (SSO) アプリケーションは、ADFS、Microsoft Entra ID (旧 Azure AD)、Bitium、Centrify、G Suite、JBoss Keycloak、Okta、OneLogin、Salesforce、AWS Cognito、OpenAM、Oracle、PingFederate、PingOne、RSA SecureID、Shibboleth-2、Shibboleth-3、SimpleSAML、WSO2 などの任意の ID プロバイダー、または独自のカスタム ID プロバイダーで構成できます。ID プロバイダーの一覧はこちらをご覧ください。
IDプロバイダーが見つからない場合は、aspnetsupport@xecurify.comまでメールでお問い合わせください。IDPとのSSO設定をサポートし、お客様の要件に関する迅速なガイダンス(メールまたは会議)を提供いたします。また、お客様の要件に最適なソリューション/プランの選択を弊社のチームがお手伝いいたします。
助けが必要? 私たちはここにいます!