
サードパーティプロバイダーを使用したWordPressのREST API認証
概要
REST API Authentication for WordPress using Third Party Provider method involves the use of tokens
(access-token/id-token/jwt token) received from third-party providers like Google, Facebook, Firebase, Apple, Azure
AD, Keycloak, Okta, AWS Cognito, Github, Slack, Gitlab, etc. for accessing wordpress rest api securely.
WordPress endpoints are not secure by default and data can be stolen via REST APIs in JSON
format. REST API Authentication for WordPress plugin allows you to call REST APIs with multiple security methods
like Basic
Auth, API KEY, JWT token, OAuth token . In this guide we will use OAuth token issued by OAuth/OpenID
Connect/Firebase providers to validate the REST API requests which will keep your WordPress website protected
and
secure.
Each time a request to access the REST API will be made, the authentication will be done against that token
issued
by third-party providers like Google, Facebook, Firebase, Apple, okta, etc, and on the basis of the validation
of
the API token, the resources for that REST API request will be allowed to access. So, the single token you
obtained
on your app after SSO login can be used further for accessing REST API endpoints for WordPress.



WordPress の REST API 認証
REST API Authentication plugin for WordPress provides security from unauthorized access to your REST APIs for WordPress. Our plugin provides multiple authentication methods like Basic Authentication, API Key Authentication, OAuth 2.0 Authentication, and JWT Authentication.
もっと知る前提条件: ダウンロードとインストール
- WordPress インスタンスに管理者としてログインします。
- WordPress に移動します ダッシュボード -> プラグイン をクリックします。入力したコードが正しければ、MFAの設定は正常に完了します 新規追加.
- を検索 RESTAPI認証 WordPressのプラグインをクリックして 今すぐインストール.
- インストールしたら、をクリックします アクティブにしましょう.
Usecase: Authenticate/protect REST API Endpoints for WordPress using the JWT token obtained from Social Login/OAuth 2.0/OpenID Connect Identity providers(Server).
- Suppose you have an android/ iOS mobile application and you have provided your user to login with multiple social login providers like Google, Facebook, Apple, Linkedin, Instagram or other OAuth/OpenID Connect providers like AWS Cognito, Auth0, Microsoft Azure, Okta, Keycloak, Firebase etc. and you want your users to access the REST API endpoints for WordPress from the mobile applications, so you can perform authentication of the REST API endpoints access based on the access/id token (JWT token) obtained from the OAuth/OpenID Connect Identity providers(server) while single Sign On(SSO) for login into your application. So the access/id token/JWT is passed in the Authorization header of the API request with the token type as Bearer and validation of that token is done directly through the corresponding OAuth/OpenId Connect/Firebase Identity providers. So the validation request is made internally to the corresponding OAuth/OpenID Connect Server. If the validation of that token is successful, the REST API request will result in resource/data access, and on the validation failure, the error response will be returned. In this way, the resources/ data can be protected with the top level of security with authentication directly from OAuth/ OpenID Connect Identity providers.
- この認証のユースケースをプラグインでどのように実現できるか:

1. The REST API Endpoint request is made with the access/id token obtained from the OAuth/OpenID Connect Identity providers passed in the Authorization header with the token type as Bearer.
2. The REST API request for WordPress is monitored by our plugin and the JWT token validation/authentication request is sent to the OAuth/OpenID Connect Identity provider(Server).
3. JWT トークンを検証するために以前に行われたリクエストに対するレスポンスが OAuth/OpenID Connect ID プロバイダー (サーバー) から返されます。
4. JWT トークンの検証/認証が成功した場合、要求されたリソースへのアクセスが許可されます。これは、リクエスタがリソース/データへのアクセスを許可されたことを意味します。トークンの検証が失敗した場合は、エラー応答が返されます。 。したがって、リソース データは保護されており、承認に基づいてアクセスできるため、セキュリティは問題になりません。
関連するユースケース:
- How to prevent REST API endpoints for WordPress using the JWT token provided by Social Login or OAuth2.0/OpenID Connect Identity Providers?
- How to perform authentication and ensure security or perform authorization to grant access to the REST API endpoints of WordPress on the basis of the access/id token provided by Social Login/OAuth providers during OAuth/OpenID SSO login flow?
- How to authenticate and access WordPress/WooCommerce REST API endpoints using Firebase JWT tokens for mobile applications?
Read Use Cases for the following Rest API Authentication Methods:


WordPress 用の API 認証プラグインの設定
- あなたの選択します。 認証方法 → サードパーティプロバイダー と追加 イントロスペクションエンドポイント OAuth/OpenID Connect プロバイダーによって提供されるをクリックします。 構成の保存.
- Once you configure the plugin with the Introspection Endpoint provided by your provider, try to access your REST APIs for WordPress using the access token/id_token provided by your OAuth Provider as shown below.

Request: GET https://<domain-name>/wp-json/wp/v2/posts
Header:
access_token : < access_token >
OR
id_token  : < id_token  >
-H 'app-name:TheAppName'
プログラミング言語のコードサンプル
var client = new RestClient("http://<wp_base_url>/wp-json/wp/v2/posts ");
client.Timeout = -1;
var request = new RestRequest(Method.GET);
request.AddHeader("Authorization", "< access_token > OR id_token <id_token>");
request.AddHeader = ("app-name", "TheAppName");
IRestResponse response = client.Execute(request);
Console.WriteLine(response.Content);
OkHttpClient client  = new OkHttpClient().newBuilder().build();
MediaType mediaType  = MediaType.parse("text/plain");
RequestBody body = RequestBody.create(mediaType, "");
Request request  = new Request.Builder()
.url("http://<wp_base_url>/wp-json/wp/v2/posts ")
.method("GET", null)
 .addHeader = ("Authorization", "< access_token > OR id_token <id_token>")
.addHeader = ("app-name", "TheAppName");
 .build();
Response responseclient.newCall(request).execute();
var settings  = {
"url": "http://<wp_base_url>/wp-json/wp/v2/posts ",
"method": "GET",
"timeout": 0,
"headers": {
"Authorization": "< access_token > OR id_token <id_token>"
"app-name": "TheAppName"
},
};

$.ajax(settings).done(function (response)  {
console.log(response);
});
<?php
 $curl = curl_init();
curl_setopt_array($curl, array
(
CURLOPT_URL => 'http://%3Cwp_base_url%3E/wp-json/wp/v2/posts%20',
CURLOPT_RETURNTRANSFER => true,
CURLOPT_ENCODING => '',
CURLOPT_MAXREDIRS => 10,
CURLOPT_TIMEOUT => 0,
CURLOPT_FOLLOWLOCATION => true,
CURLOPT_HTTP_VERSION => CURL_HTTP_VERSION_1_1,
CURLOPT_CUSTOMREQUEST => 'GET',
CURLOPT_HTTPHEADER => array(
'Authorization: < access_token > OR id_token <id_token>'
'app-name: TheAppName'
),

));

$response = curl_exec($curl);
curl_close($curl);
echo $response;
import http.client

conn   = http.client.HTTPSConnection("<wp_base_url>")
payload= "
headers = {
'Authorization': '< access_token > OR id_token <id_token>'
'app-name': 'TheAppName',
}
conn.request("GET", "/wp-json/wp/v2/posts ", payload, headers)
res= conn.getresponse()
data = res.read()
print (data.decode("utf-8"))
郵便配達員のサンプル:
- Postman リクエスト形式のサンプルは、以下からダウンロードできます。 こちら.
- ダウンロードした zip ファイルを抽出し、抽出した json ファイルを Postman アプリケーションにインポートします。
- 置き換える <アクセストークン> or < id_token > with the respective token provided by your OAuth 2.0 provider.
- 置き換える <アプリ名> それぞれの AppName に置き換えます。
- 例:
Postman を使用して REST API リクエストを作成するには、次の手順に従います。


機能説明
1. ロールベースの REST API の制限:
This feature allows restricting the REST API access based on the user roles. You can whitelist the roles for which you want to allow access to the requested resource for the REST APIs. So whenever a REST API request is made by a user, his role will be fetched and only allowed to access the resource if his role is whitelisted.
それを構成する方法は?
- まず、プラグインの「詳細設定」タブに移動します。
- Then, in the Role based Restriction section, all the roles by default will be allowed to access the APIs. You can enable the checkbox of the roles for which you want to restrict access.
- In the above screenshot, the subscriber role checkbox is enabled. So whenever an API request is made by the user with his role as subscriber then that user won’t be allowed to access the requested resource.
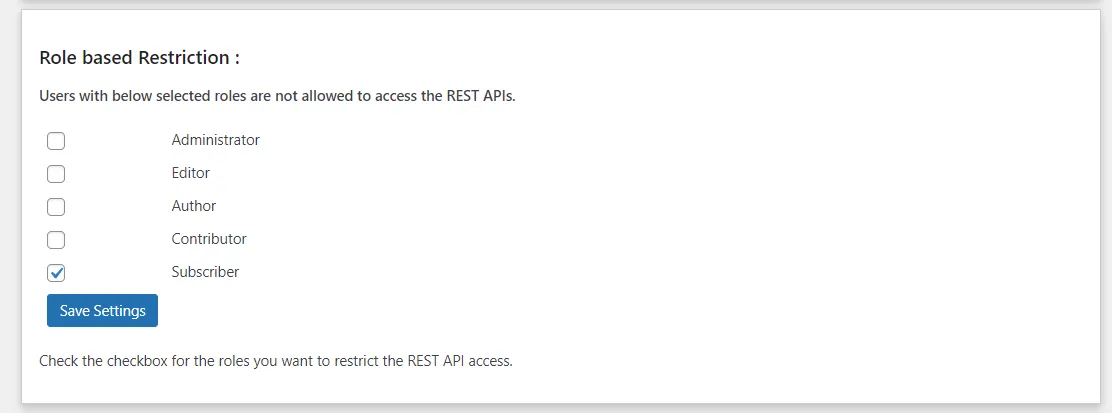
注意: The Role based restriction feature is valid for Basic authentication(Username: password), JWT method, and OAuth 2.0 (Password grant).
2. カスタムヘッダー
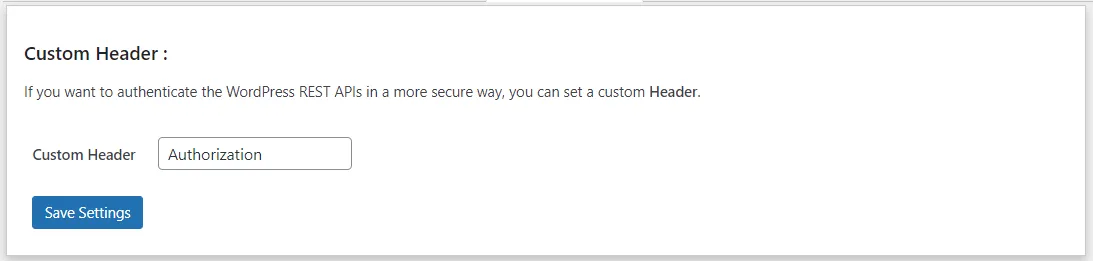
この機能では、デフォルトの「Authorization」ヘッダーではなくカスタム ヘッダーを選択するオプションが提供されます。
It will increase the security as you have the header named with your ‘custom name’, so if someone makes the REST API request with a header as ‘Authorization’ then he won’t be able to access the APIs.
それを構成する方法は?
- まず、プラグインの「詳細設定」タブに移動します。
- 次に、「カスタムヘッダー」セクションで、テキストボックスを編集して、必要なカスタム名を入力できます。
3. REST APIを除外する
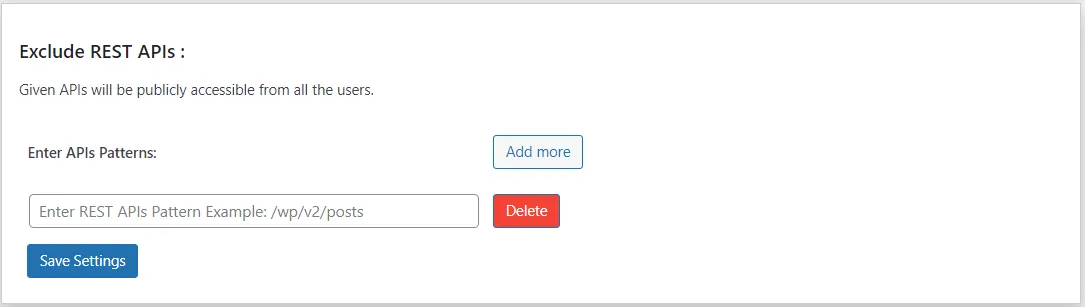
This feature allows you to whitelist your REST APIs so these can be accessed directly without any authentication. Hence all these whitelisted REST APIs are publicly available.
それを構成する方法は?
- まず、プラグインの「詳細設定」タブに移動します。
- Then in the ‘Exclude REST APIs’, you can enter your APIs in the prescribed format which needs to be whitelisted for public access.
- 例: REST API を除外したいとします。
「/wp-json/wp/v2/posts」の場合は、テキストボックスに「/wp/v2/posts」と入力する必要があります。
4. カスタムトークンの有効期限
This feature is applicable for JWT and OAuth 2.0 methods which uses time based tokens to authenticate the REST API endpoints for WordPress. This feature allows you to set the custom expiry for the tokens such that the token will no longer be valid once the token expires.
それを構成する方法は?
- まず、プラグインの「詳細設定」タブに移動します。
- Then in the ‘Token Expiry Configuration’ section, the access token validity and refresh token(used for OAuth 2.0 method) can be altered. By default the access token expiry time is set to 60 minutes and the refresh token expiry time is set to 14 days. Hence with this feature, the expiry can be adjusted accordingly as per the requirements.
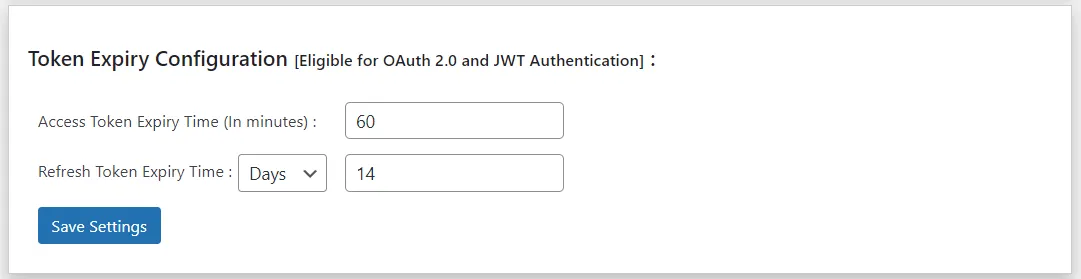
したがって、このカスタム トークンの有効期限機能を使用すると、セキュリティがさらに強化されます。
5. HMAC を使用してトークンの高度な暗号化を有効にする
This feature is available with the Basic Authentication method in which by default the token is encrypted using Base64 encoding technique but with the advanced feature, the token can be encrypted with highly secure HMAC encryption which is very secure.

6. JWT ベースのトークンの署名の検証
This feature allows a secure signing of the JWT signature for the JWT token such that your JWT token is much more secure and the signature can only be decoded using the client secret/certificate. It means your signature is private and can not be seen by others.
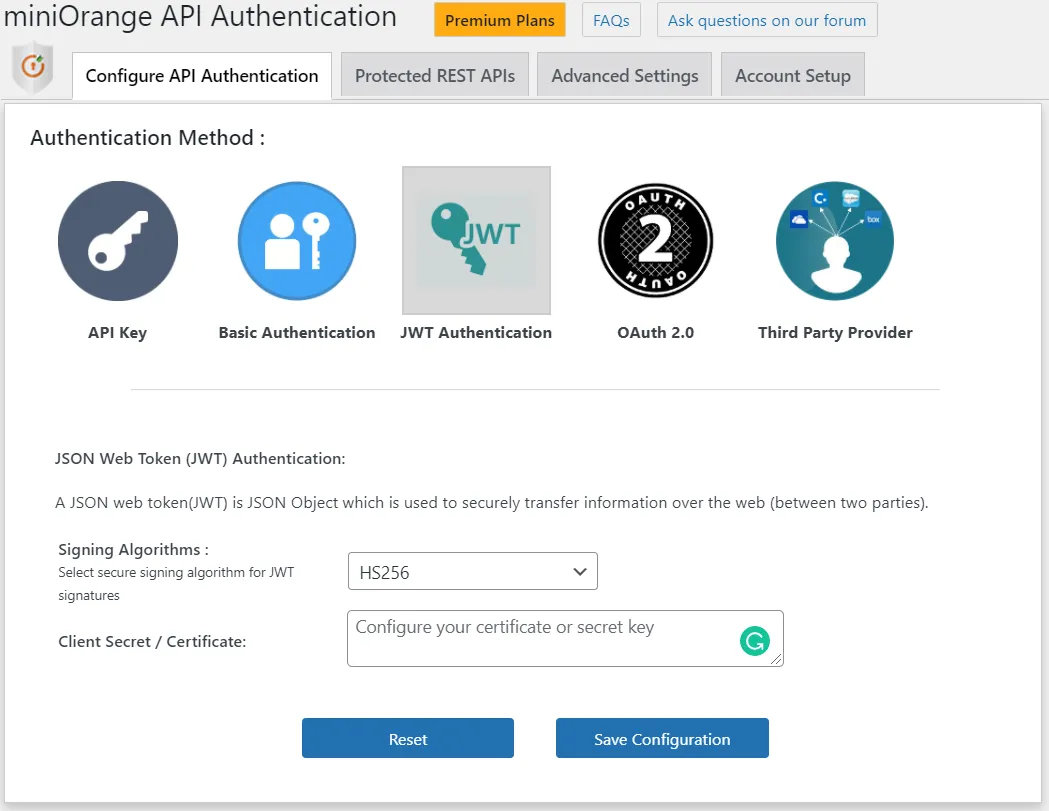
We provide the support for 2 Signing algorithms: HS256 and RS256.So, any of the signing algorithms can be chosen from the dropdown as shown in the above image.
また、JWT の署名に使用されるクライアント シークレットまたは証明書を追加する必要があります。
7. ユーザー固有の API キー/トークンを作成する
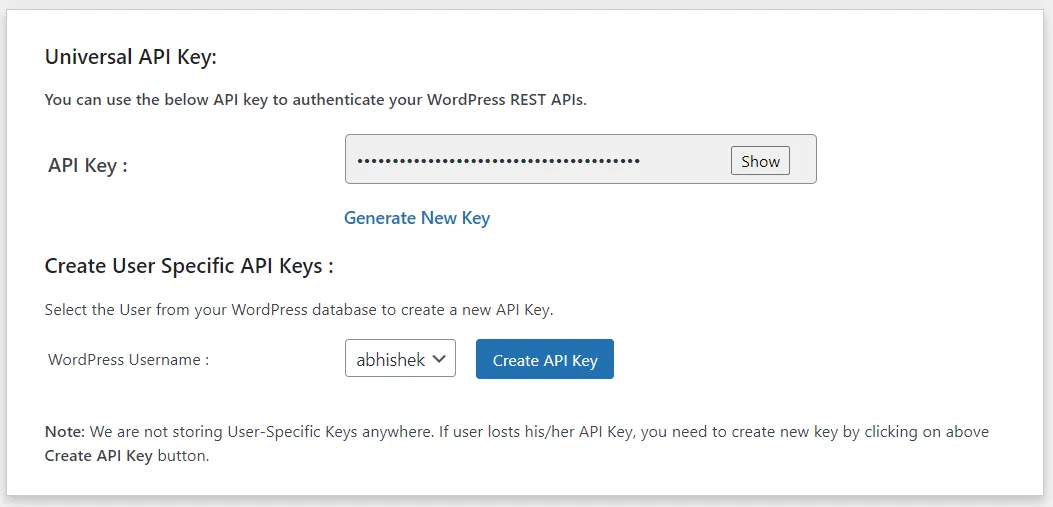
- This feature is available within the API key method in which the tokens can be generated in accordance with the user information rather than a randomly generated token which is a universal key.
- With the Universal API key/token, users do not have permission to access certain REST APIs for WordPress with POST, PUT, or DELETE request methods, such as creating users, posts, or pages etc, in which a particular user permissions/role is required to perform operations via use of the REST API request as the universal key is randomly generated and does not contain the user based description.
- So this User based API key/token feature allows the user to access the REST APIs with request method as POST,PUT,DELETE in WordPress which requires user credentials or certain roles to perform the operation such that the when the REST API request for WordPress is made with the user-based key then the role of the user is obtained and he will be allowed to access the API only if he has permission to do so.
- 例: Only users with administrator and editor roles have permissions to create/edit/delete a post.
- So, if a request is made to this API to create/delete/edit the post, the API response will result in “You are not allowed to perform this operation”.
- Now, if a request is made with the user-based token generated for the user that has administrator or editor role then only they have access to this API and are able to perform the operation(create/update/delete) via the API call.
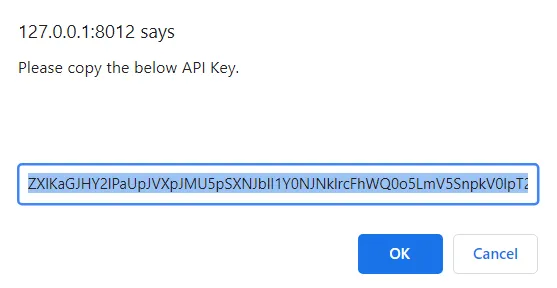
- ドロップダウンからユーザーを選択し、「API キーの作成」ボタンをクリックします。
- 画面にポップアップが表示されます。OK ボタンをクリックしてトークンをコピーするだけです。
- Now this token can be used with the API request just like the universal key is used to make the API request.
この機能の使用方法:
 プラグインのデモをリクエストする
フル機能のトライアル版を入手
ご返信ありがとうございます。近日中にご連絡させていただきます。
何か問題が発生しました。 もう一度質問を送信してください
お困りですか?
ご要望について迅速なガイダンス(メールまたはミーティング)をご希望の場合は、 apisupport@xecurify.comまでメールでお問い合わせください。弊社のチームがお客様のご要望に最適なソリューション/プランの選択をお手伝いいたします。


