There are two ways detailed below with which you can configure your SAML Identity Provider metadata in the middleware.
A] Upload metadata using the Upload IDP Metadata button:
- If your identity provider has provided you with the metadata URL or metadata file (.xml format only), then you can simply configure the identity provider metadata in the middleware using the Upload IDP Metadata option.
- Copy metadata URL or download the metadata file to configure the same on your identity provider end.
- You may refer to the screenshot below:
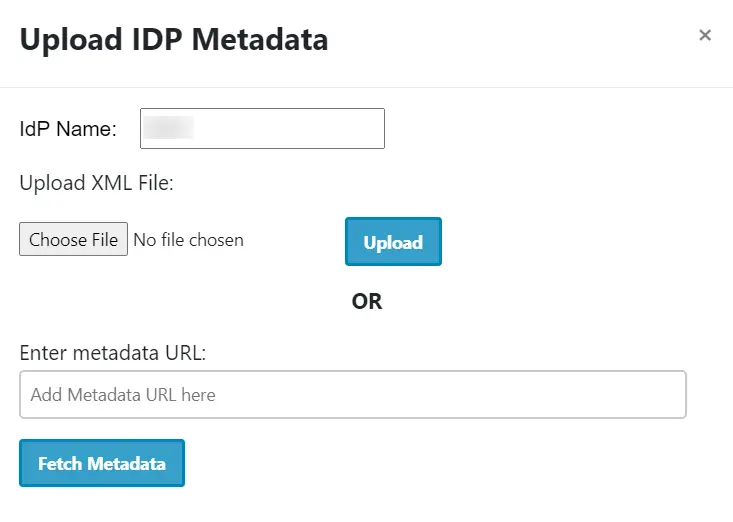
- You can choose any one of the options according to the metadata format you have available.
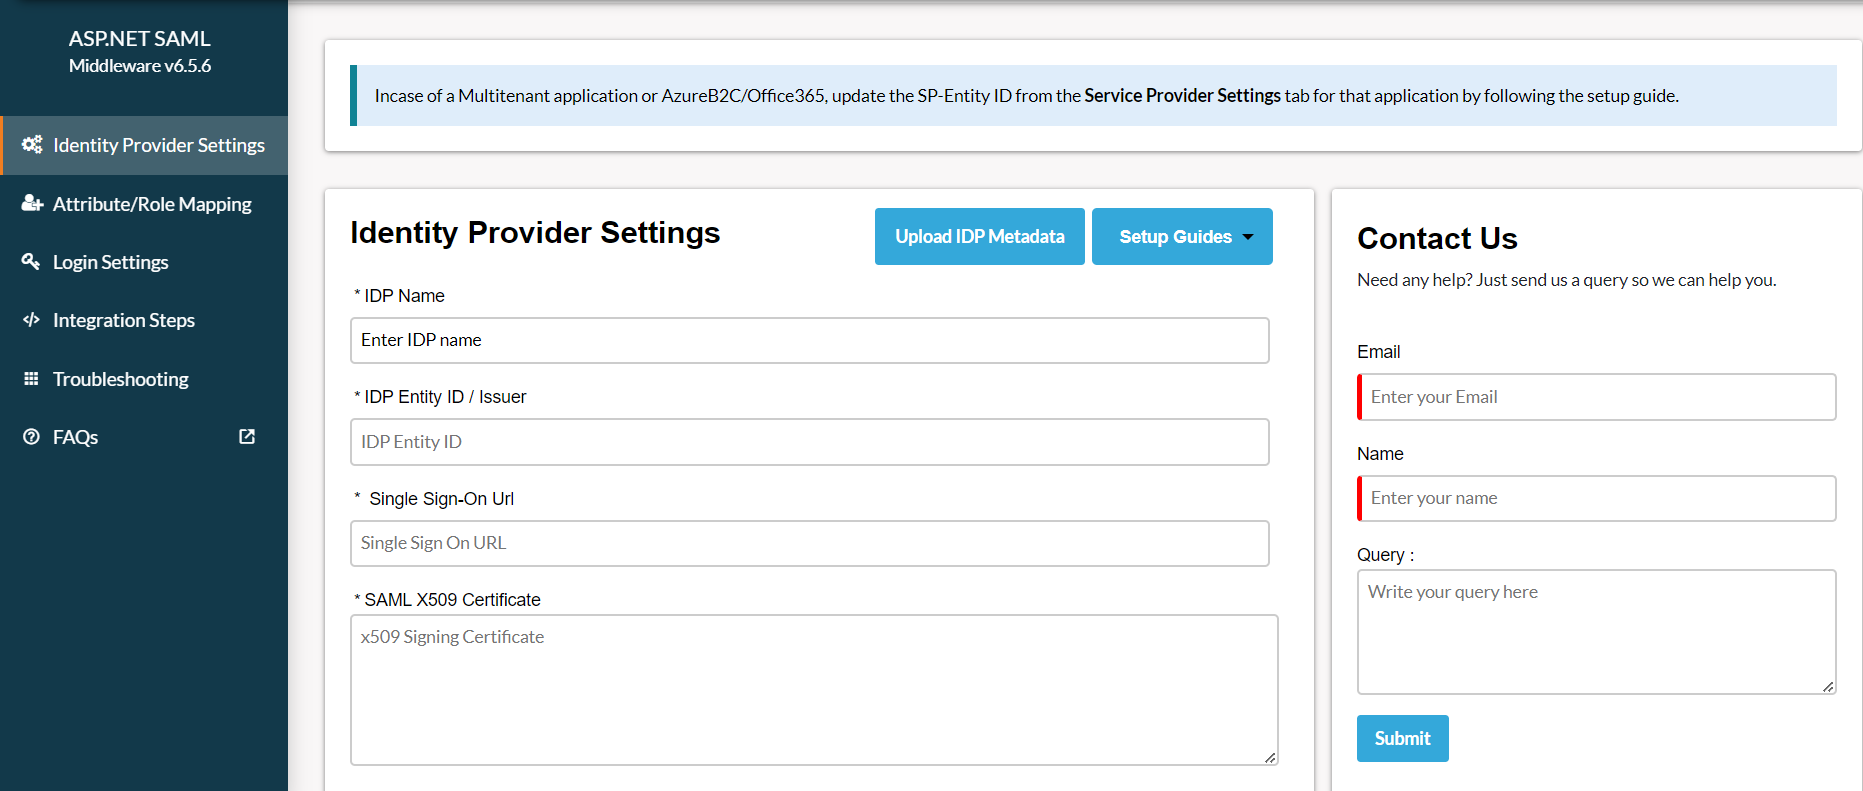
B] Configure the identity provider metadata manually:
- After configuring your Identity Provider, it will provide you with IDP Entity ID, IDP Single Sign On URL and SAML X509 Certificate fields respectively.
- Click Save to save your IDP details.
4. Testing SAML SSO
- After uploading the metadata details, navigate to the Identity Provider Settings section. Hover over the Select Actions dropdown and click on Test Configuration.

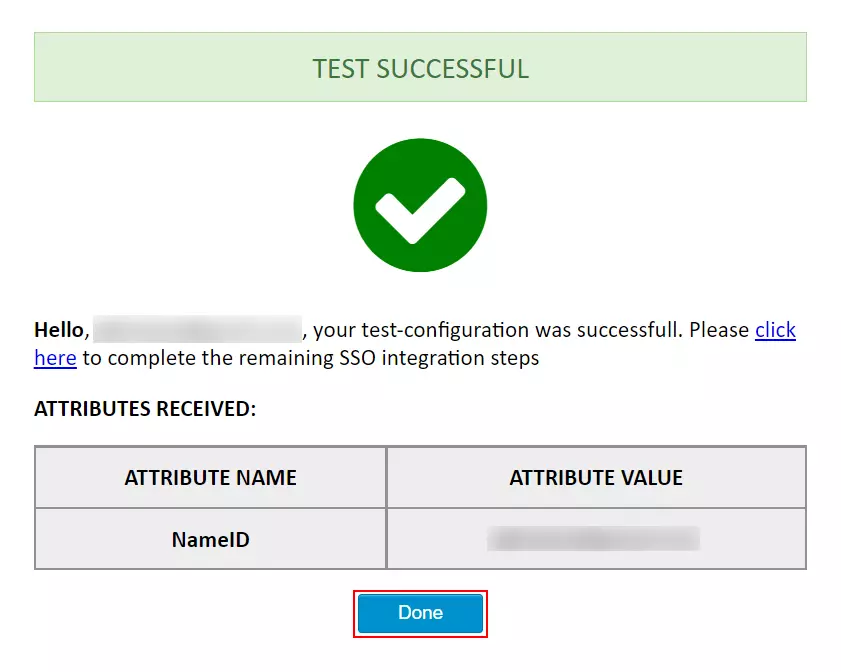
- The screenshot below shows a successful result. Click on SSO Integration to further continue with the SSO Integration.
- If you are experiencing any error on the middleware end you’ll be shown with the window similar to below.
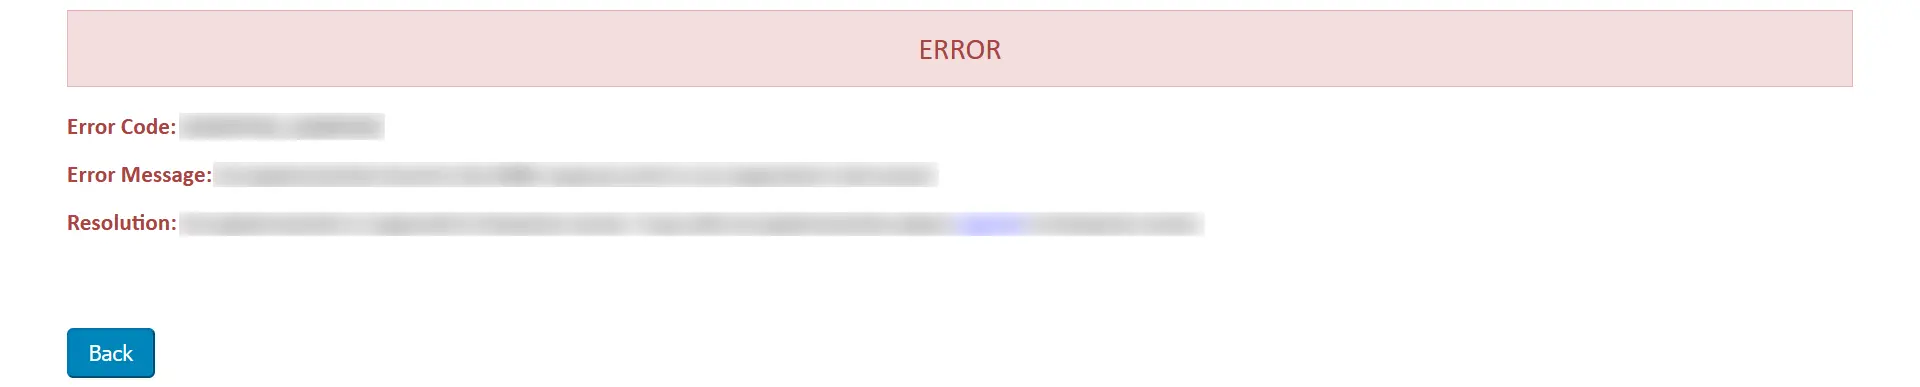
- To troubleshoot the error you can follow the below steps:
- Under Troubleshoot tab, enable the toggle to receive the plugin logs.
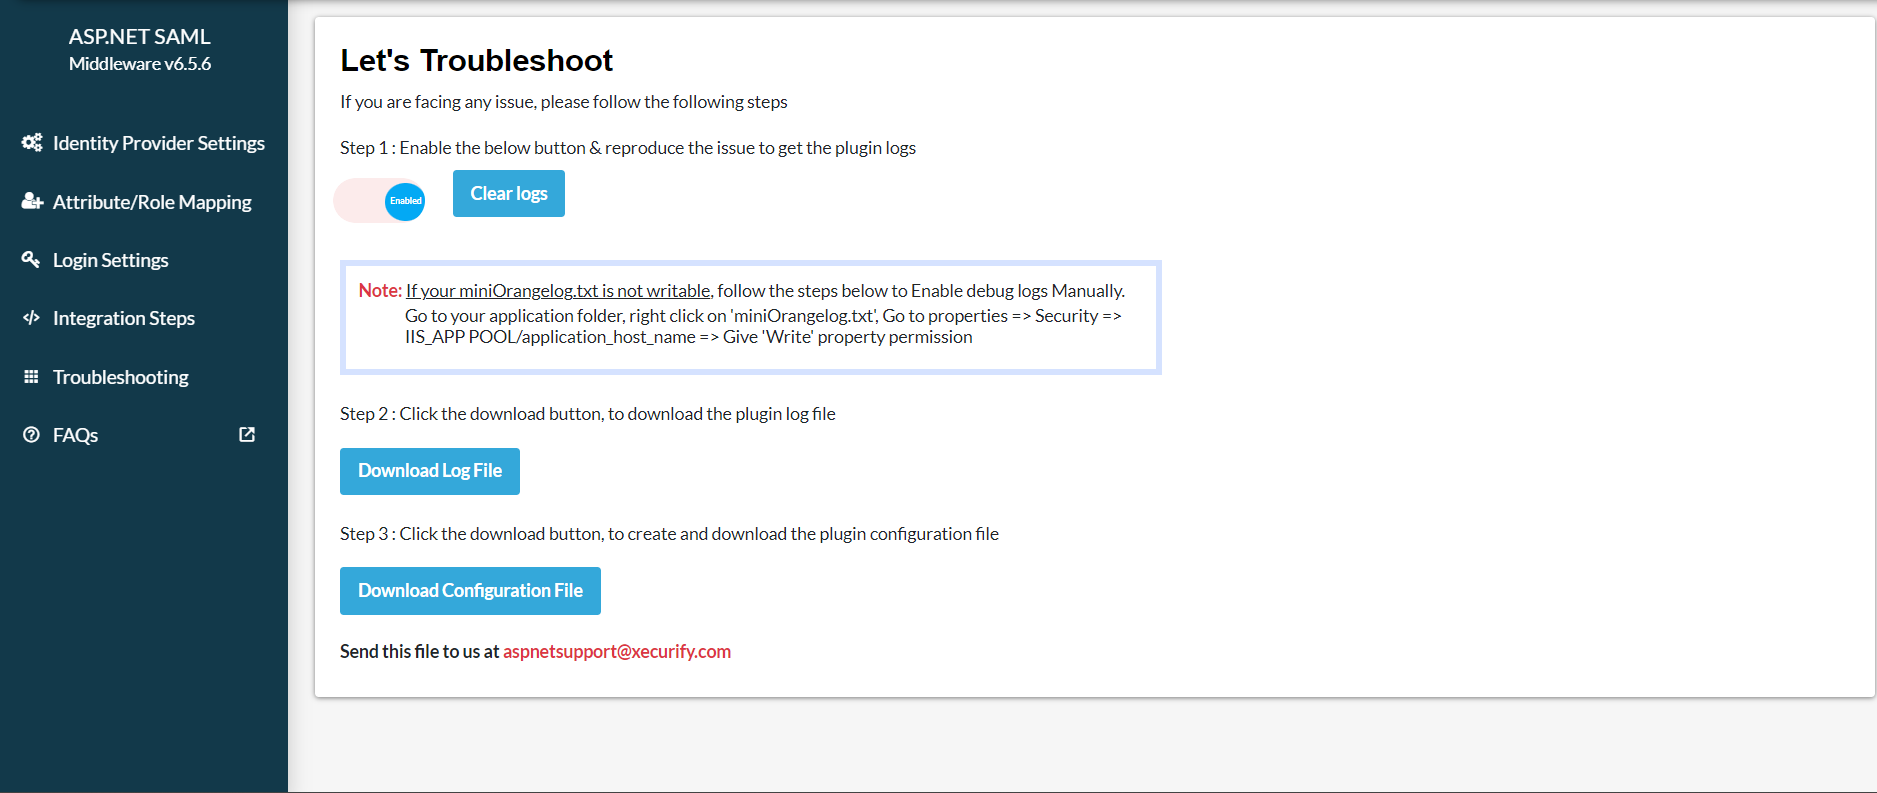
- Once enabled, you will be able to retrieve plugin logs by navigating to Plugin Settings tab and clicking on Test Configuration.
- Download the log file from the Troubleshoot tab to see what went wrong.
- You can share the log file with us at aspnetsupport@xecurify.com and our team will reach out to you to resolve your issue.
5. Attribute Mapping
- After testing the configuration, Map your application attributes with the Identity Provider (IdP) attributes.
- From the left-hand menu of the miniOrange ASP.NET SAML SSO Middleware, click on Attribute/Role Mapping tab as shown in the image.

- If you want to pass additional attributes from your IdP, enter the Attribute Name and corresponding Attribute Value under Custom Attribute Mapping.
- Note: All the mapped attributes will be stored in the session so that you can access them in your application.
- Once the attributes are mapped, click Save Attribute Mapping to apply changes.

6. Integration Code
- This steps allow you to retrieve the SSO user information in your application in the form of user claims.
- You can also look the setup tour to understand how the SSO integration would work in your asp.net middleware application.
- Just copy-paste that code snippet wherever you want to access the user attributes.
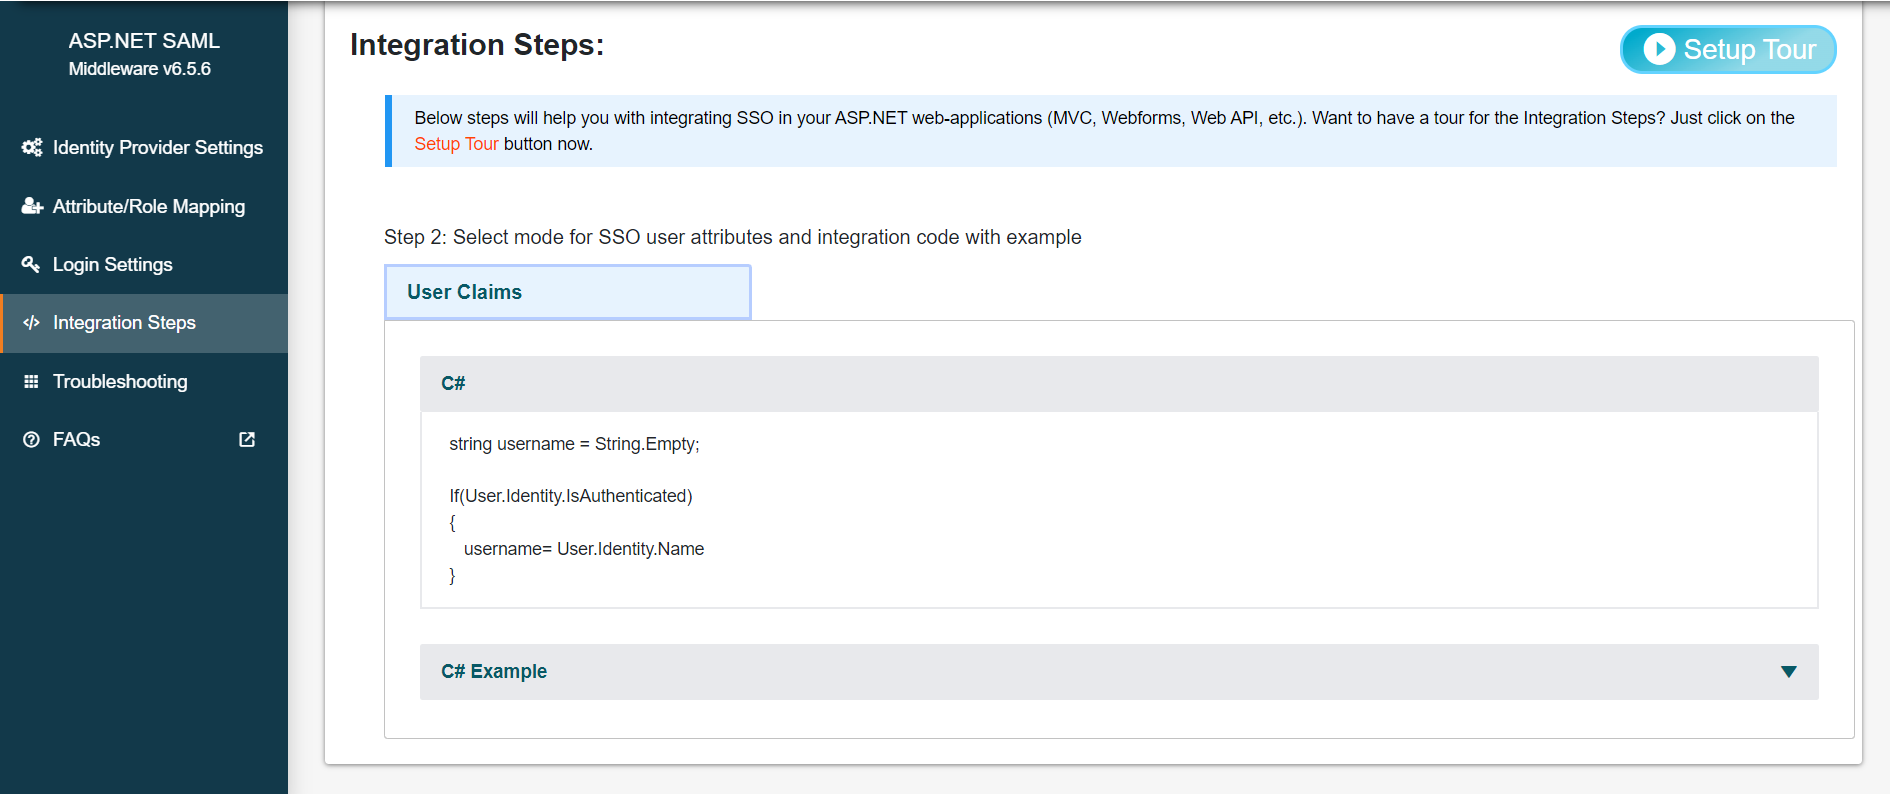
- Note: With the trial middleware the authenticated user details are stored in user claims using the default .NET Cookie Authentication. Support of setting user claims using Header-based, Session-based, JWT-based authentication is available in our premium plugin.
- You can also copy the integration code from below:
          string name="";

          string claimtype="";

          string claimvalue="";


          if(User.Identity.IsAuthenticated)


          {


            foreach(var claim in User.claims)


           {


             claimtype = claim.Type;


             claimvalue = claim.Value;


           }


           //retrive custom attributes(for eg. Retrieve Mapped 'mobileNumber' attribute of your IDP)


           var identity = (ClaimsIdentity)User.Identity;


           IEnumerable claims = identity.claims;


           string mobileNumber = identity.FindFirst("mobileNumber")?.Value;


         }
7. Login Settings
- Hover on Select Actions and click on Copy SSO Link.

- Use the following URL as a link in the application from where you want to perform SSO:
https://<asp.net-middleware-base-url>/?ssoaction=login
- For example, you can use it as:
                      <a href="https://<asp.net-middleware-base-url>/?ssoaction=login">Log
                    in</a>
8. Logout Settings
- Use the following URL as a link to your application from where you want to perform SLO:
https://<asp.net-middleware-base-url>/?ssoaction=logout
- For example, you can use it as:
                      <a href="https://<asp.net-middleware-base-url>/?ssoaction=logout">Log
                    out</a>


