LastPass SSO for WordPress | LastPass Single Sign-On (SSO) Login for WordPress
Overview
LastPass SSO (SAML Single Sign-On) login [SAML SSO] for WordPress can be achieved by using our SAML SP Single Sign-On (SSO) plugin for WordPress. Our SSO solution will make WordPress as SAML 2.0 compliant Service Provider establishing trust between the WordPress site and LastPass to securely authenticate and login users to the WordPress site. Our LastPass Single Sign-On (SSO) solution helps to secure WordPress sites behind the SSO login so that users are authenticated using their LastPass login credentials. Here we will go through a guide to configure LastPass SSO (SAML Single Sign-On) login between WordPress site and LastPass by considering LastPass as IdP (Identity Provider) and WordPress as SP (Service Provider). Our SAML SSO plugin provides Unlimited user authentications from LastPass.
You can visit our SSO plugin for WordPress to know more about the other features we provide.
Pre-requisites : Download And Installation
To configure LastPass as SAML IdP with WordPress, you will need to install the miniOrange SAML SP SSO plugin for WordPress.
Configuration Steps
1. Setup LastPass as IdP (Identity Provider)
Follow the following steps to Configure LastPass as IdP:
Configure LastPass as IdP
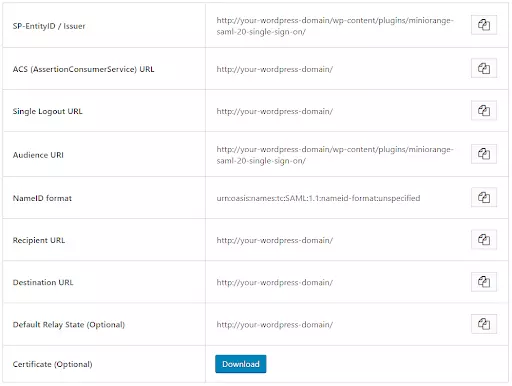
- In the miniOrange SAML SP SSO plugin, navigate to Service Provider Metadata tab. Here, you can find the SP metadata such as SP Entity ID and ACS (AssertionConsumerService) URL which are required to configure the Identity Provider.
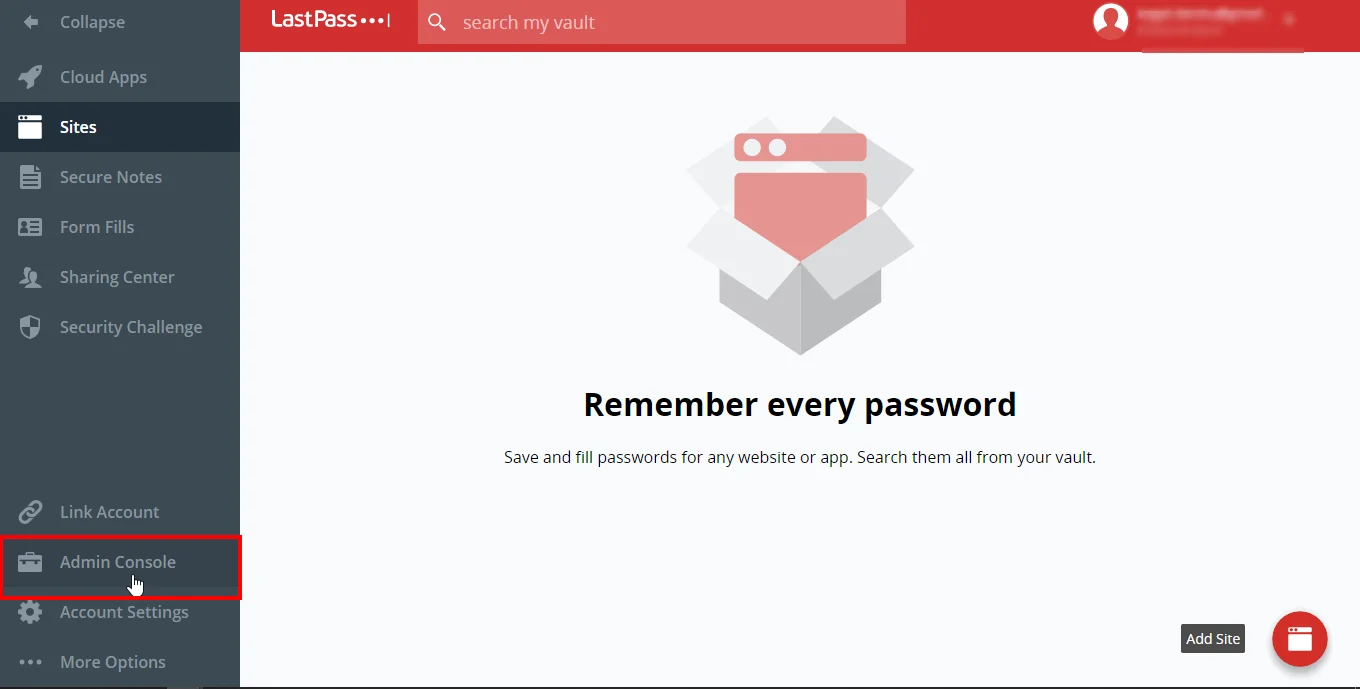
- Now click on SSO & MFA option.
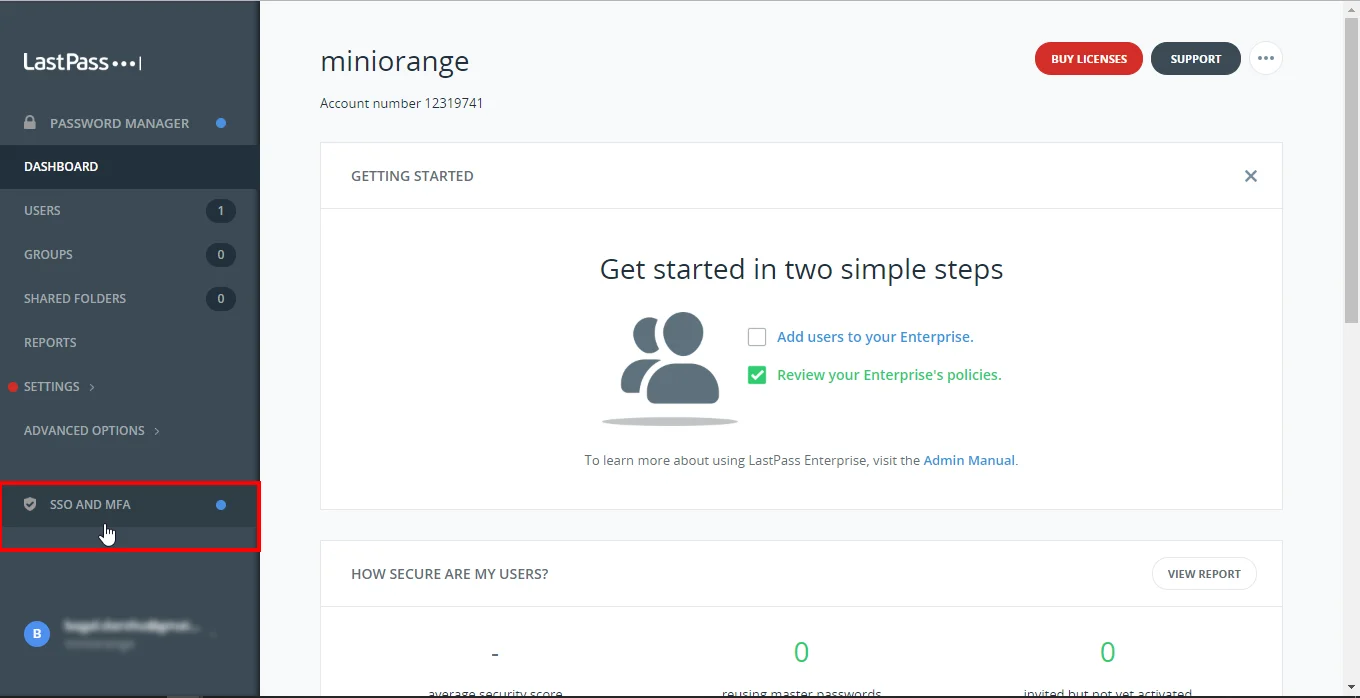
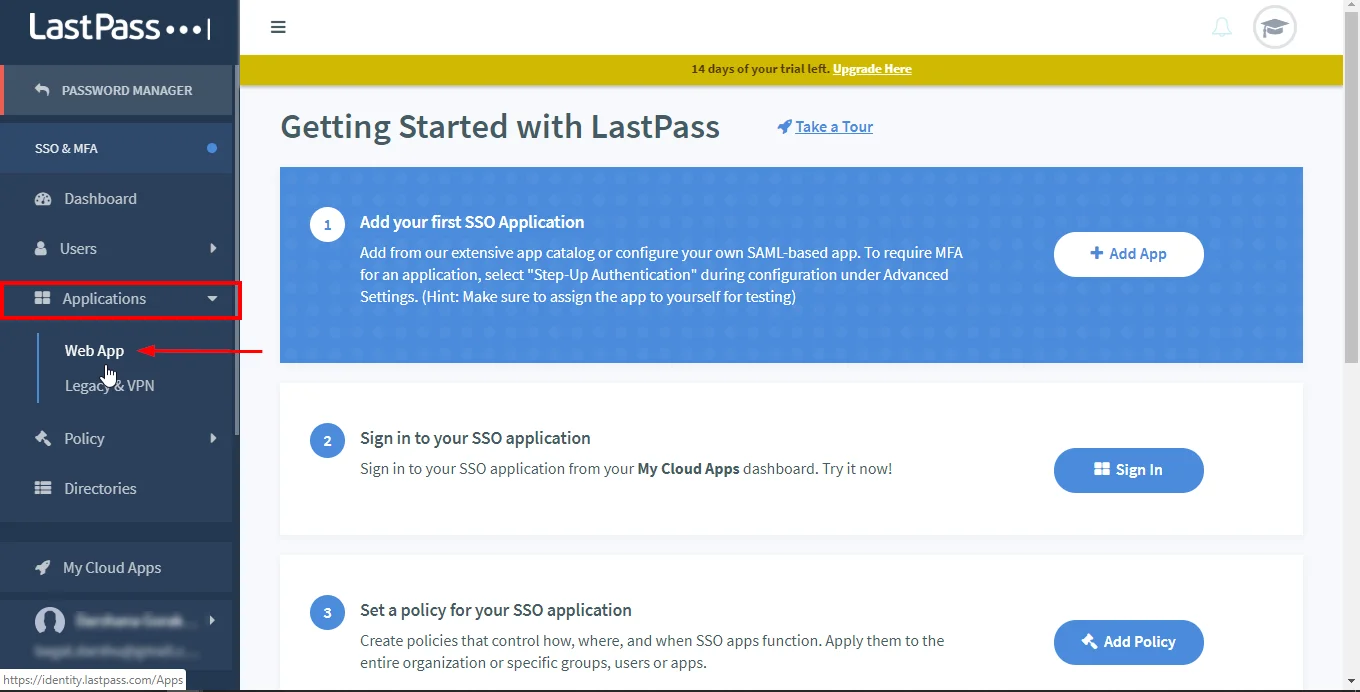
- Under the Application tab, click on Web App.
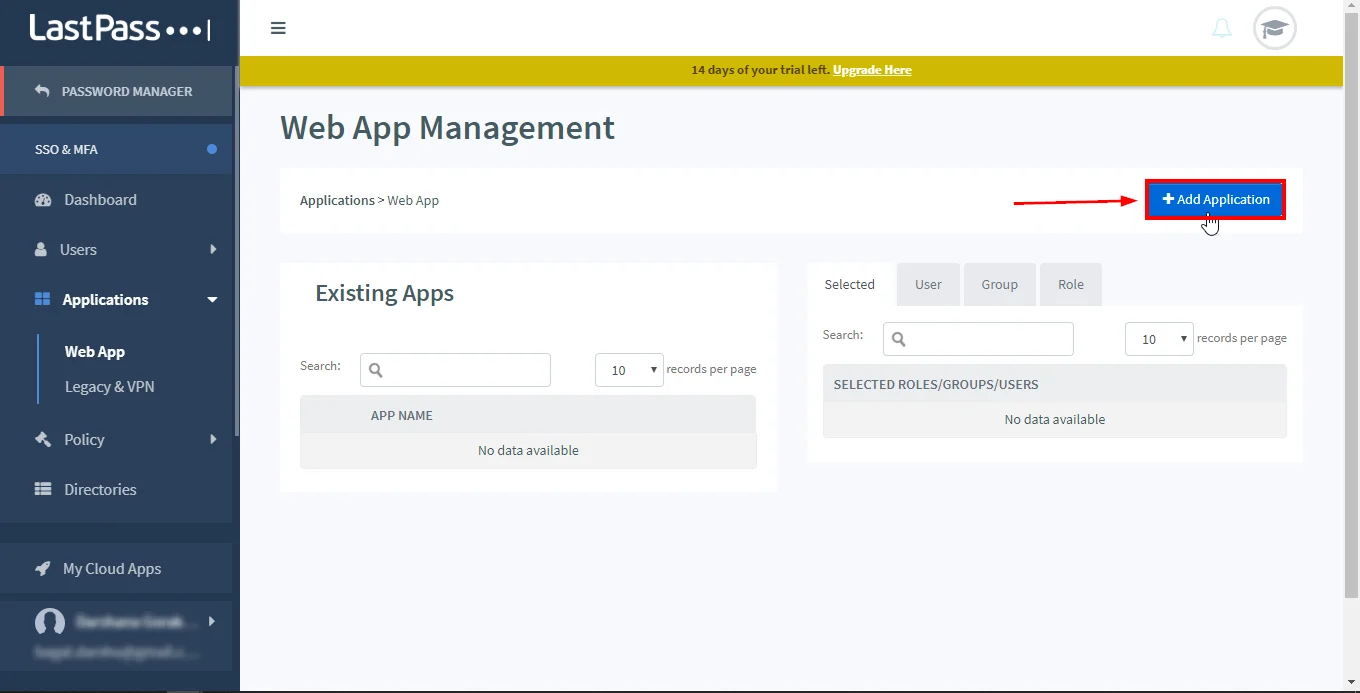
- On the top right corner, click on the Add Application button to create new app.
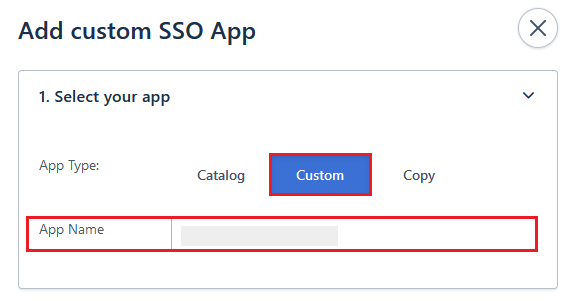
- In the Add catalog SSO App section, navigate to the Select your App option.
- Select App Type as Custom and enter your App Name.
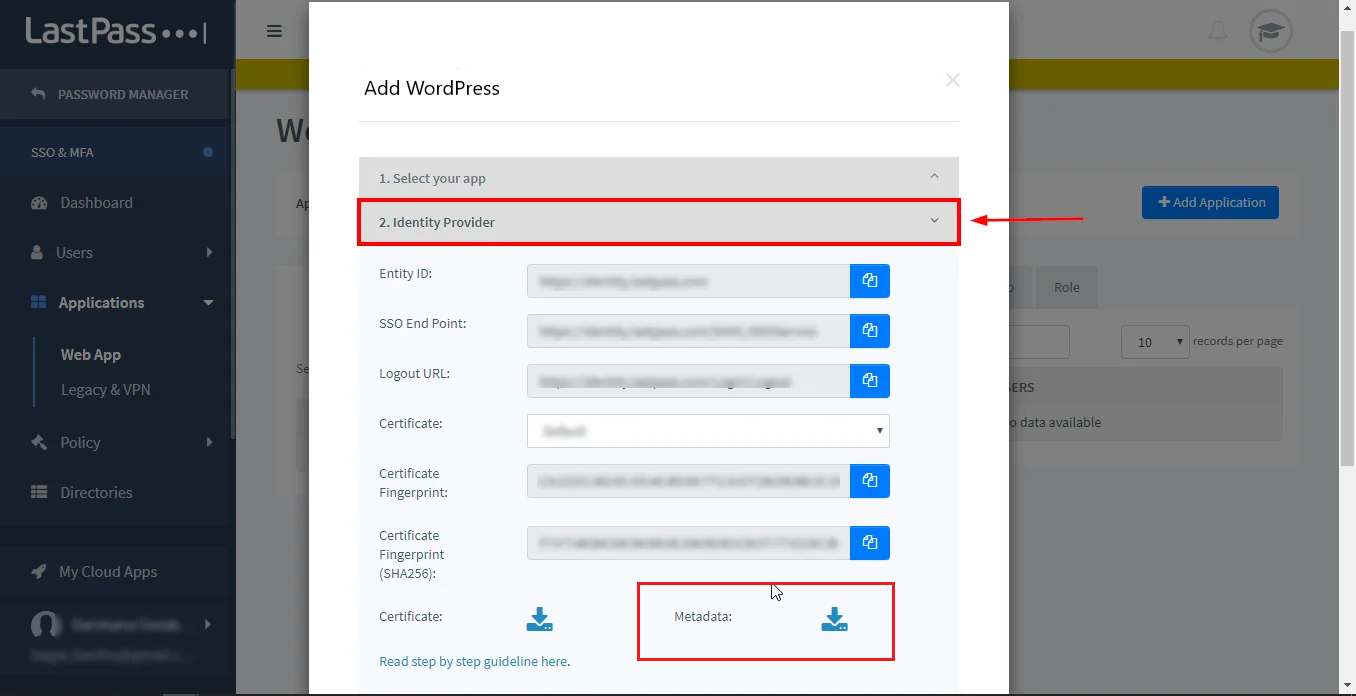
- From Identity Provider section copy the required information or download the metadata to configure the Service Provider.
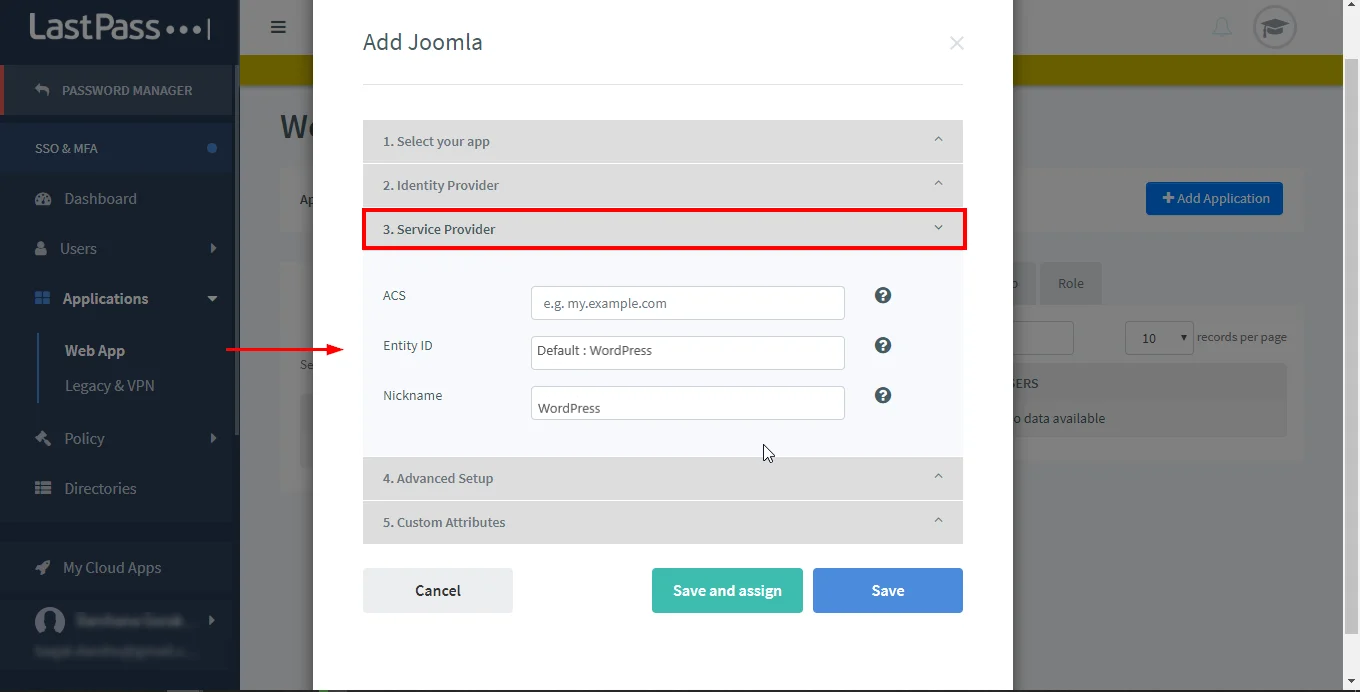
- In the Service Provider section, enter the required details:
| ACS |
ACS (AssertionConsumerService) URL from the Service Provider Metadata tab of the Plugin |
| Entity ID |
SP Entity ID / Issuer from the Service Provider Metadata tab of the Plugin |
| Nickname |
WordPress |
- Configure Advanced Setup and Custom Attributes as per the requirement (Optional).
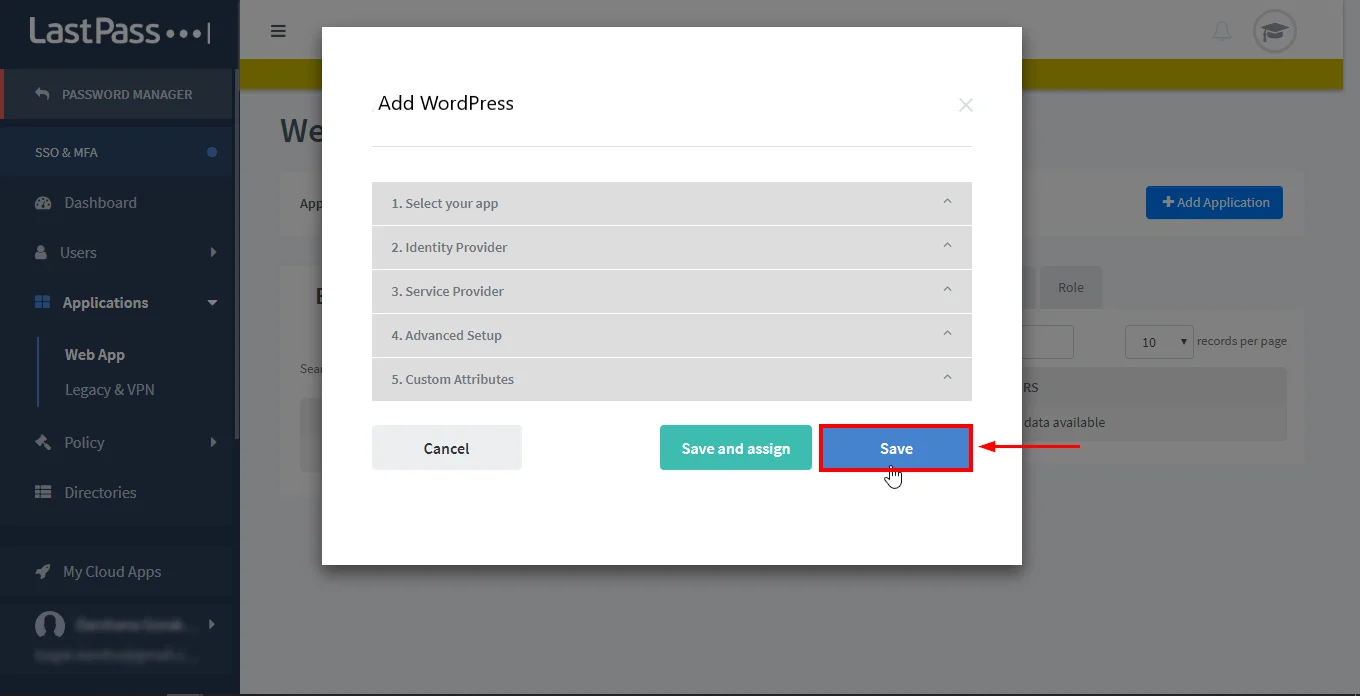
- Once all the configuration is completed then click on Save.
Assigning Groups/People
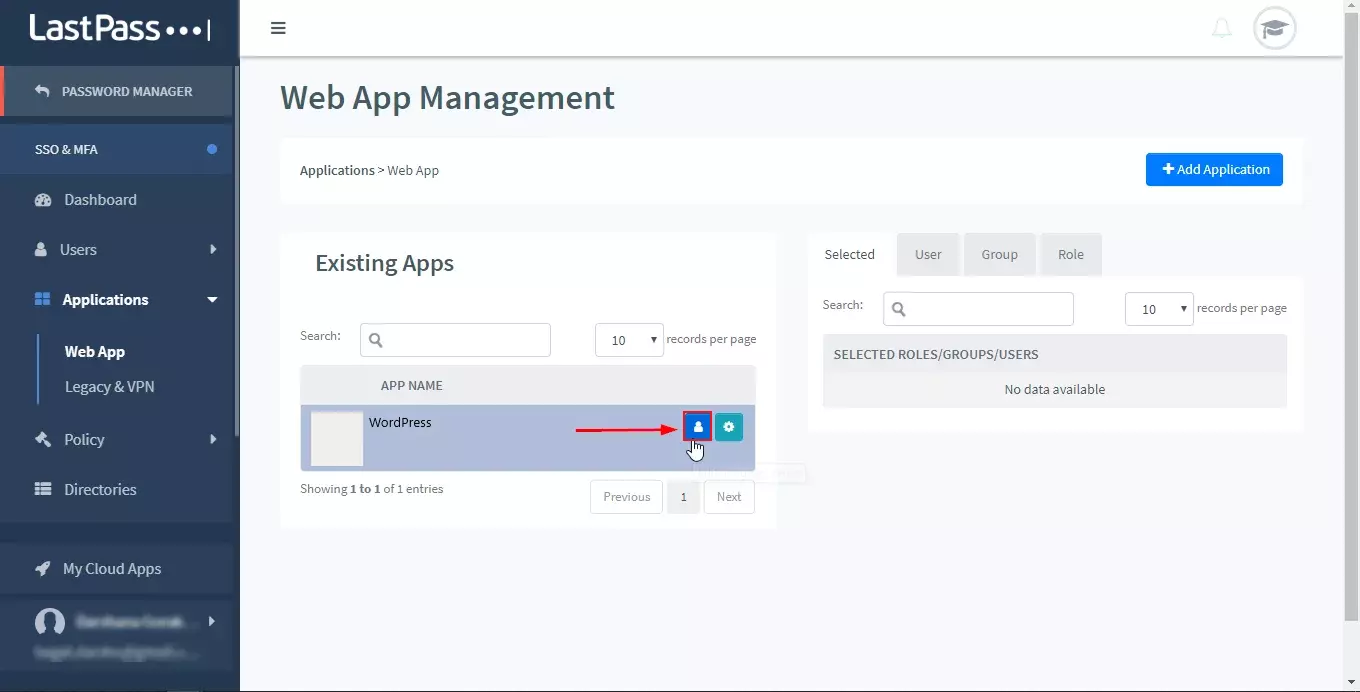
- Navigate to the application you created and click on the contact icon in LastPass.
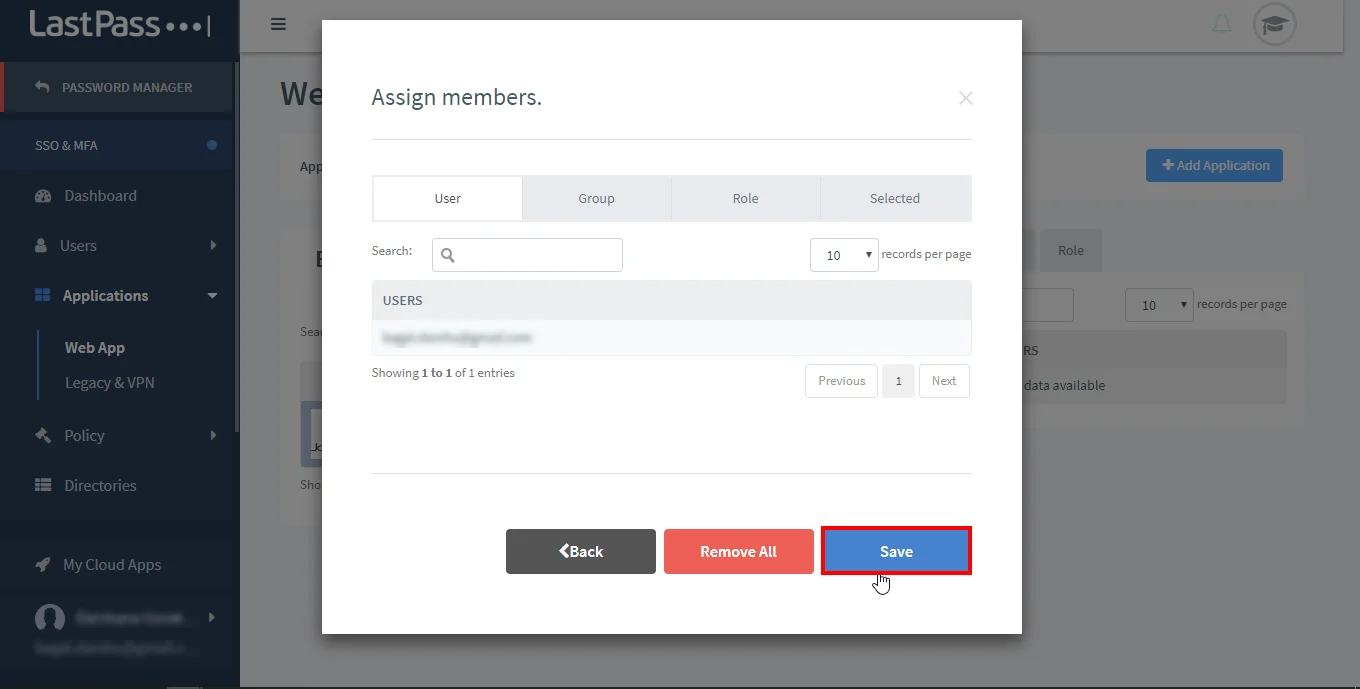
- Assign the users according to the User/Groups and click on Save.
- Download LastPass MFA App and login by doing barcode scan/mail in the mobile (Optional).
You have successfully configured LastPass as SAML IdP (Identity Provider) for achieving LastPass Single Sign-On (SSO) Login, ensuring secure LastPass Login into WordPress (WP) Site.
Step 2: Configure
WordPress as SP (Service Provider)
In the SAML SSO plugin for WordPress, go to the IDP Configuration tab of the plugin. There are two
ways to configure the SSO Plugin for WordPress:
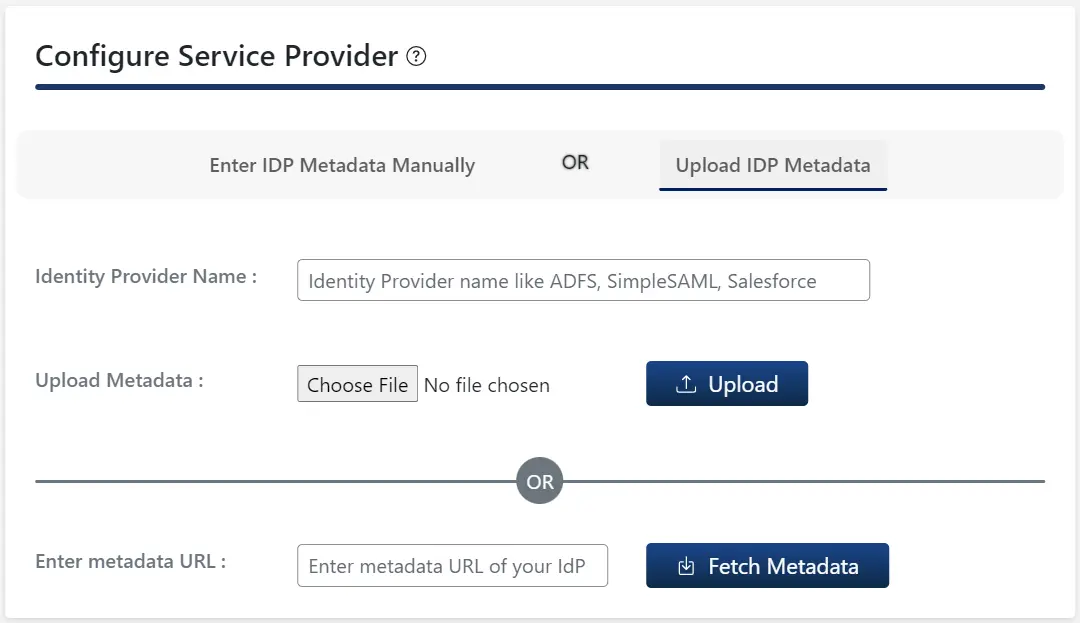
A. By uploading IDP metadata:
- Click on Upload IDP metadata button.
- Enter the Identity Provider Name
- You can either upload a metadata file and click on Upload button or use a
metadata URL and click on Fetch Metadata.
B.Manual Configuration:
- Provide the required settings (i.e. Identity Provider Name, IDP Entity ID or Issuer, SAML Login
URL, X.509 Certificate) as provided by your Identity Provider and click on the Save
button.
- Click on Test configuration to check the attributes and values sent by IDP.

Step 3: Attribute Mapping

Note: To configure attribute mapping for multiple identity providers, follow the setup guide
here. This feature is available in the Enterprise plan.
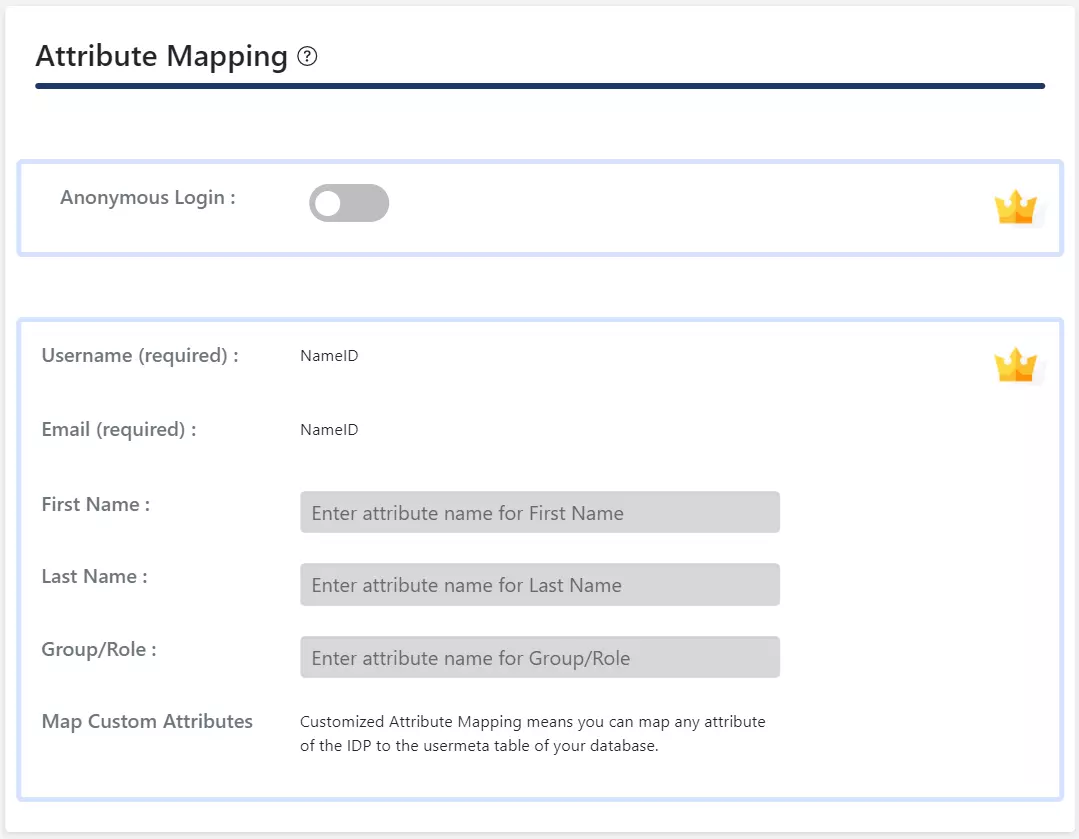
- In the free plugin, only NameID is supported for Email and Username attributes of the
WordPress user.
- When a user performs SSO, the NameID value sent by the IDP will get mapped to the email and
username of the WordPress user.
In the SAML SSO plugin for WordPress, go to the Service Provider Setup tab of the plugin. There are two
ways to configure the SSO Plugin for WordPress:
A. By uploading IDP metadata:
- Click on Upload IDP metadata button.
- Enter the Identity Provider Name
- You can either upload a metadata file and click on Upload button or use a
metadata URL and click on Fetch Metadata.
B.Manual Configuration:
- Provide the required settings (i.e. Identity Provider Name, IDP Entity ID or Issuer, SAML Login
URL, X.509 Certificate) as provided by your Identity Provider and click on the Save
button.
- Click on Test configuration to check the attributes and values sent by IDP.

Step 3: Attribute Mapping
Note: To configure attribute mapping for multiple identity providers, follow the setup guide
here. This feature is available in the Enterprise plan.
- Attribute Mapping feature allows you to map the user attributes sent by the IDP
during SSO to the user attributes at WordPress.
- In SAML Plugin for WordPress, go to Attribute/Role Mapping tab and fill up the following
fields in Attribute Mapping section.
NOTE: If you click on Test Configuration button in Service Provider Setup tab and
authenticate with your IDP, you can see a list of attributes sent by the IDP in the
Attribute/Role mapping tab. This information can be used to
provide the above mapping.
In the SAML SSO plugin for WordPress, go to the Service Provider Setup tab of the plugin. There are two
ways to configure the SSO Plugin for WordPress:
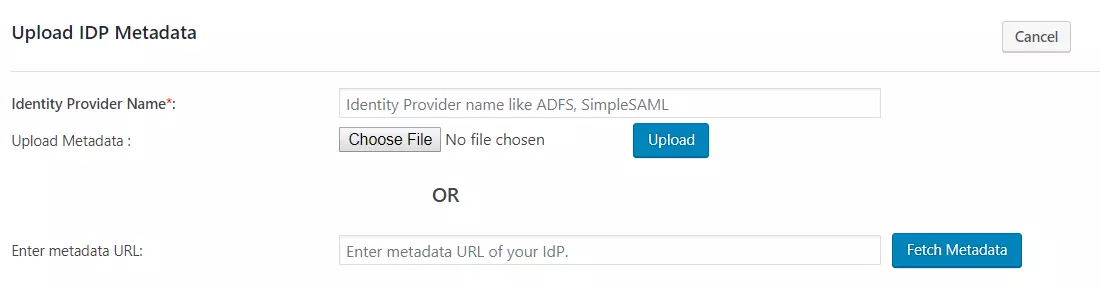
A. By uploading IDP metadata:
- Click on Upload IDP metadata button.
- Enter the Identity Provider Name
- You can either upload a metadata file and click on Upload button or use a
metadata URL and click on Fetch Metadata.
- In the Premium plugin, you can enable auto-sync for the metadata URL which
will auto-update the plugin configuration as per the IDP metadata after a set interval of time
B.Manual Configuration:
- Provide the required settings (i.e. Identity Provider Name, IDP Entity ID or Issuer, SAML Login
URL, X.509 Certificate) as provided by your Identity Provider and click on the
Save button.
- Click on Test configuration to check the attributes and values sent by IDP.

-
In the Premium Plugin, you can provide the SAML Logout URL to achieve Single Logout on your
WordPress site.
Step 3: Attribute Mapping
Note: To configure attribute mapping for multiple identity providers, follow the setup guide
here. This feature is available in the Enterprise plan.
-
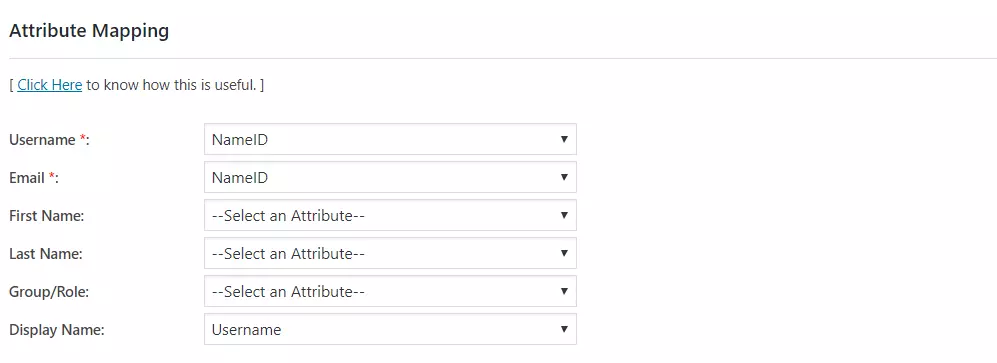
Attribute Mapping feature allows you to map the user attributes sent by the IDP
during SSO to the user attributes at WordPress.
-
In SAML Plugin for WordPress, go to Attribute/Role Mapping tab and fill up the following
fields in Attribute Mapping section.
-
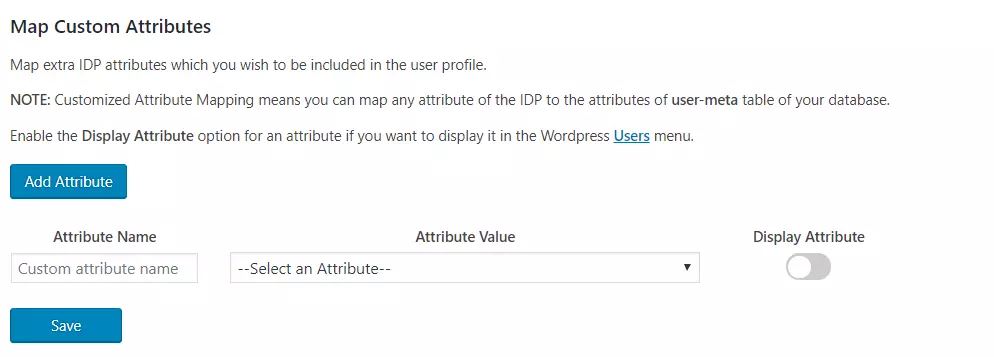
Custom Attribute Mapping: This feature allows you to map any attribute sent by the
IDP to the usermeta table of WordPress.
Step 4: Role Mapping
Note: To configure role mapping for multiple identity providers, follow the setup guide here. This feature is available in the Enterprise plan.
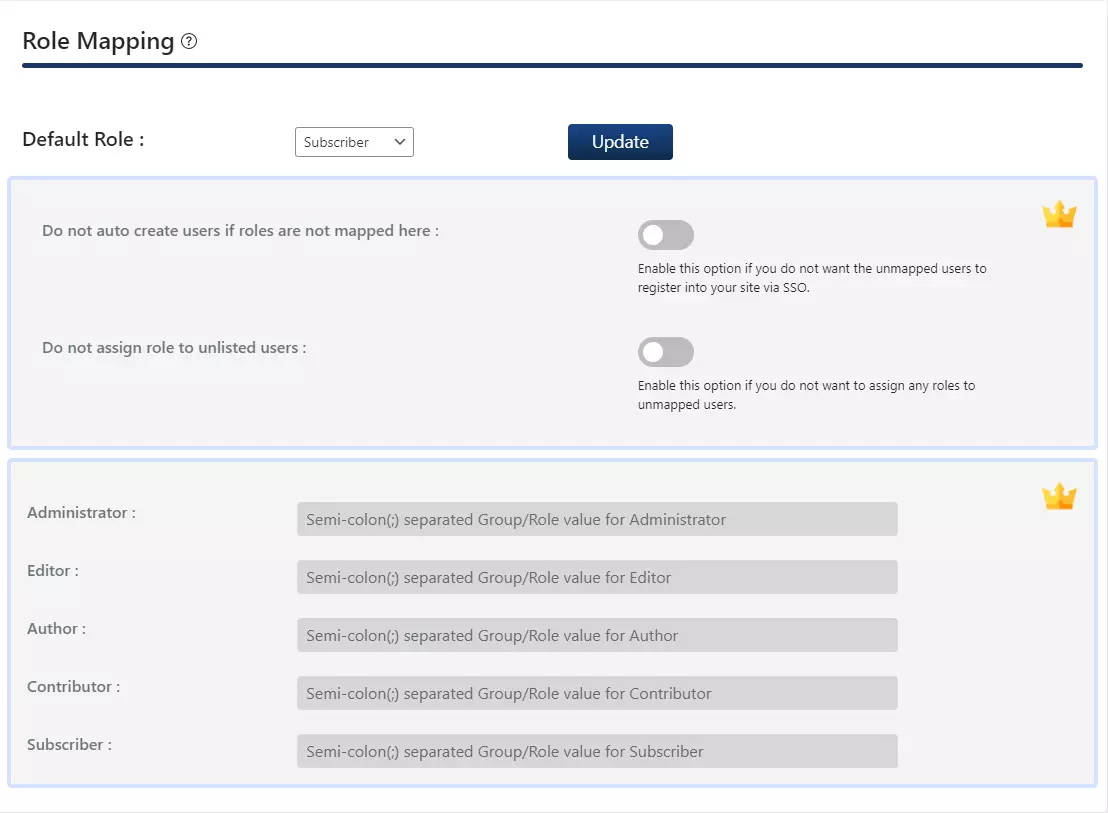
- In the free plugin, you can choose a Default Role which will be assigned to all the
non-admin users when they perform SSO.
- Go to Attribute/Role mapping tab and navigate to Role Mapping section.
- Select the Default Role and click on the Update button.
Step 4: Role Mapping
Note: To configure role mapping for multiple identity providers, follow the setup guide here. This feature is available in the Enterprise plan.
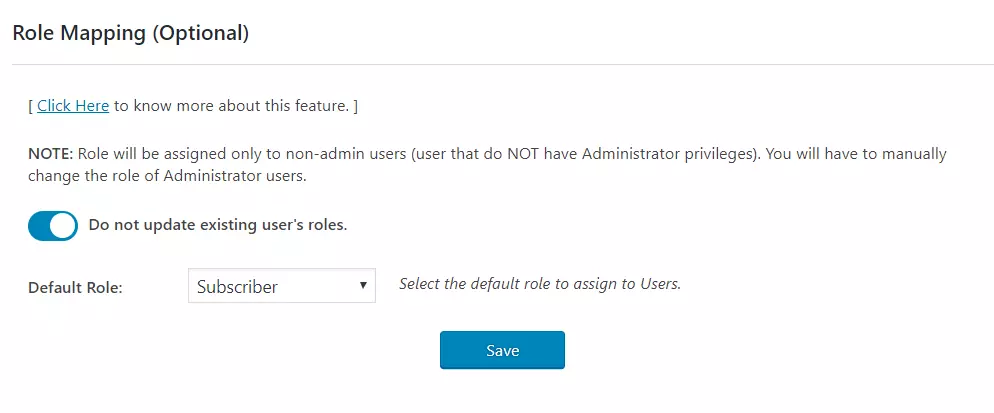
In the standard plugin, you can choose a default role which will be assigned to all the non-admin
users when they perform SSO.
- Go to Attribute/Role mapping tab and navigate to Role Mapping section.
- Select the Default Role and click on the Save button.
Step
4: Role Mapping
This feature allows you to assign and manage roles of the users when they perform SSO. Along with
the default WordPress roles, this is compatible with any custom roles as well.
Note: To configure role mapping for multiple identity providers, follow the setup guide here. This feature is available in the Enterprise plan.
- From the Attribute Mapping section of the plugin, provide a mapping for the field named
Group/Role. This attribute will contain the role related information sent by the IDP and
will be used for Role Mapping.
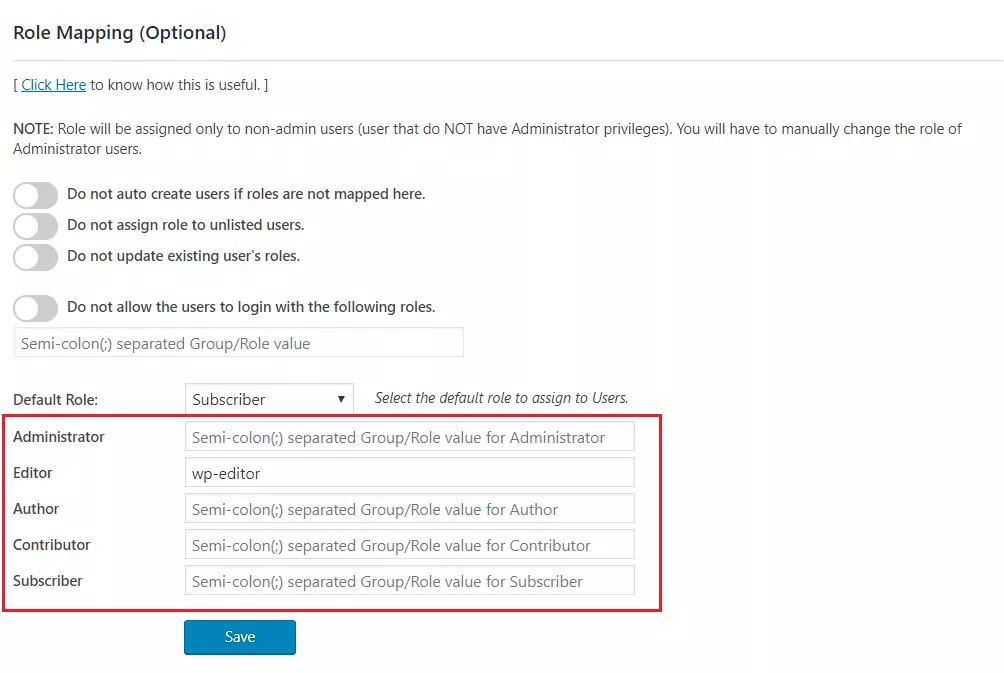
- Navigate to role mapping section and provide the mappings for the highlighted roles.
-
For example, If you want a user whose Group/Role attribute value is wp-editor to be
assigned as an Editor in WordPress, just provide the mapping as wp-editor in the Editor
field of Role Mapping section.
Step 5: SSO settings
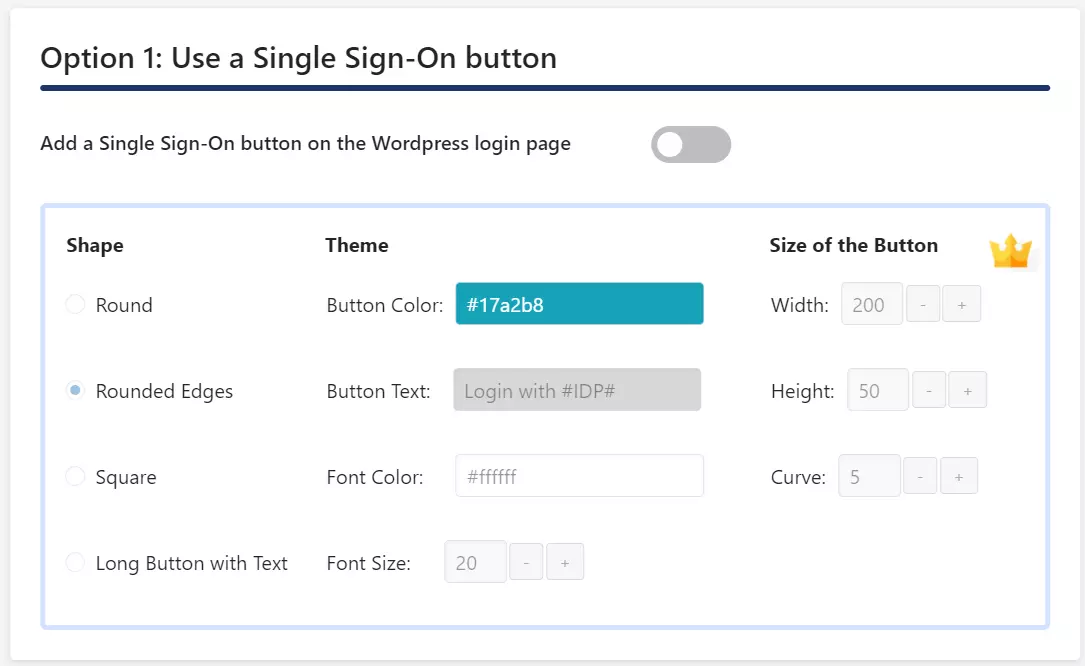
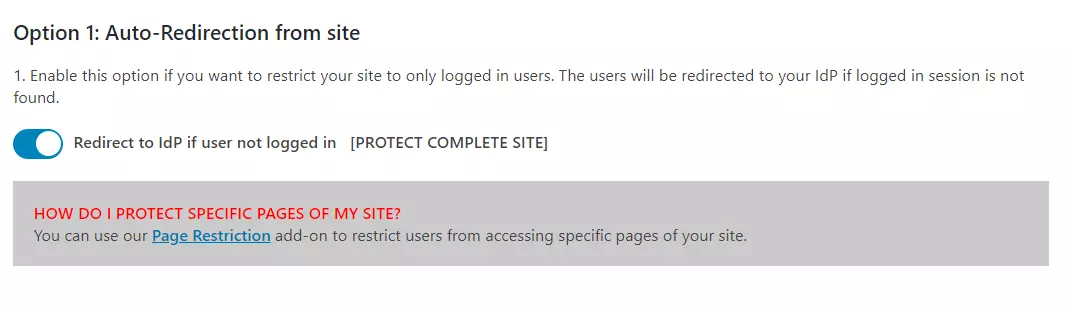
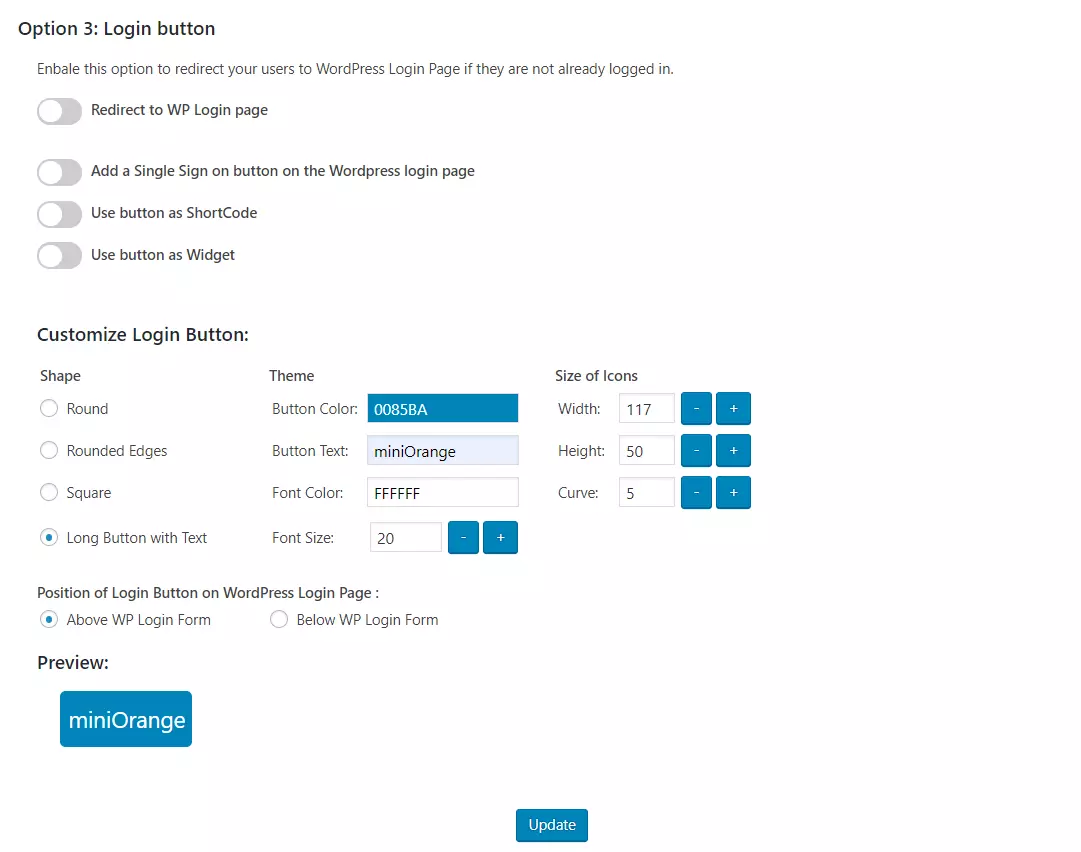
- In the free plugin you can add a Single Sign-On button by enabling Add a Single Sign-On
button on the WordPress Login Page toggle in Option 1.
- If your WordPress theme supports login widget, you can add a login widget to enable SP-Initiated
SSO on your site.
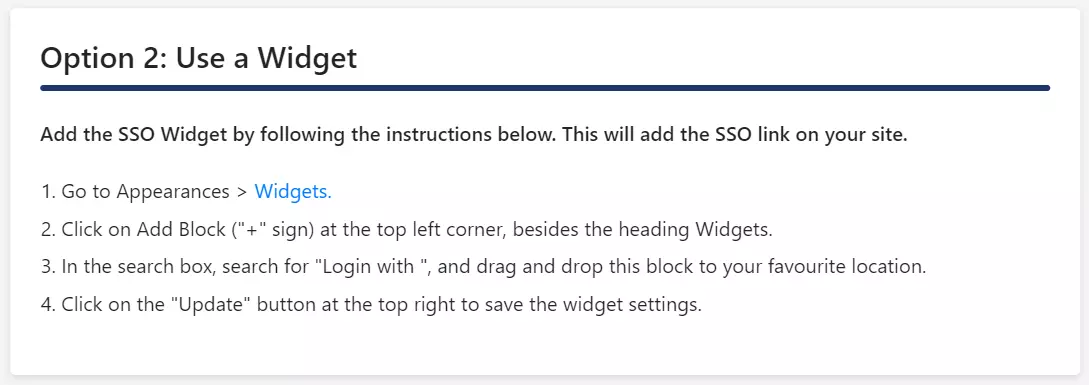
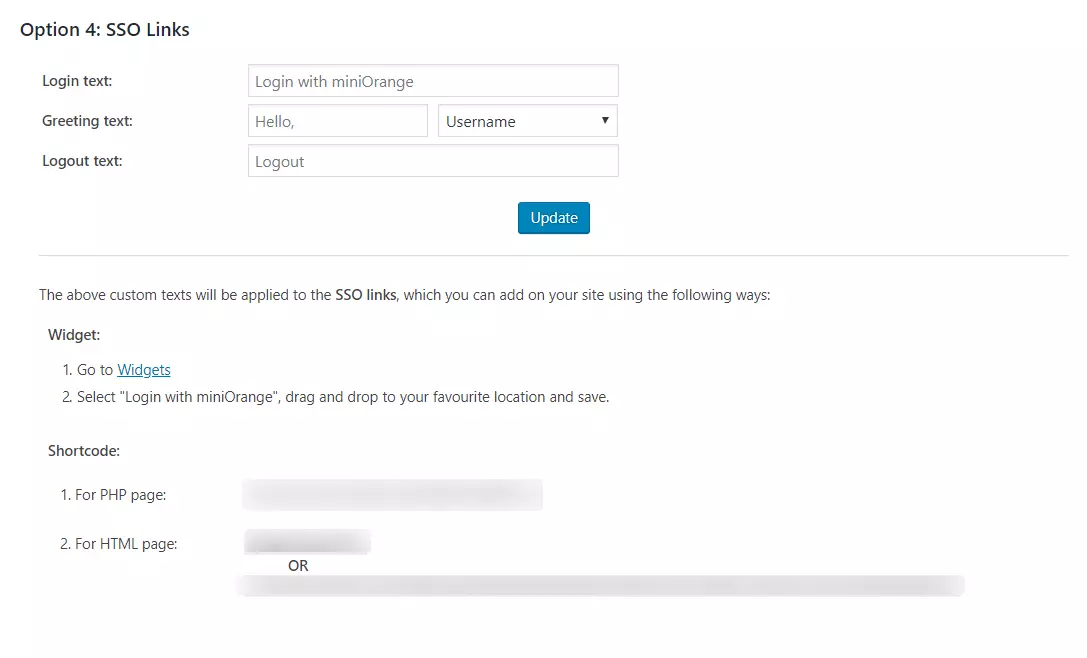
- Navigate to Redirection and SSO links tab and follow the given steps given under Option 2:
Use a Widget to add a login widget on your site.
Step 5: SSO settings
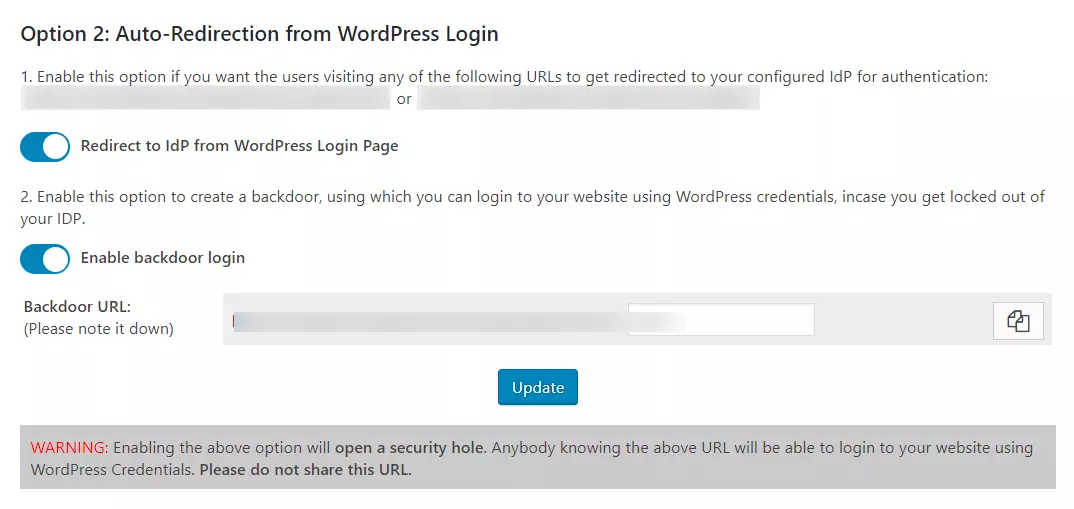
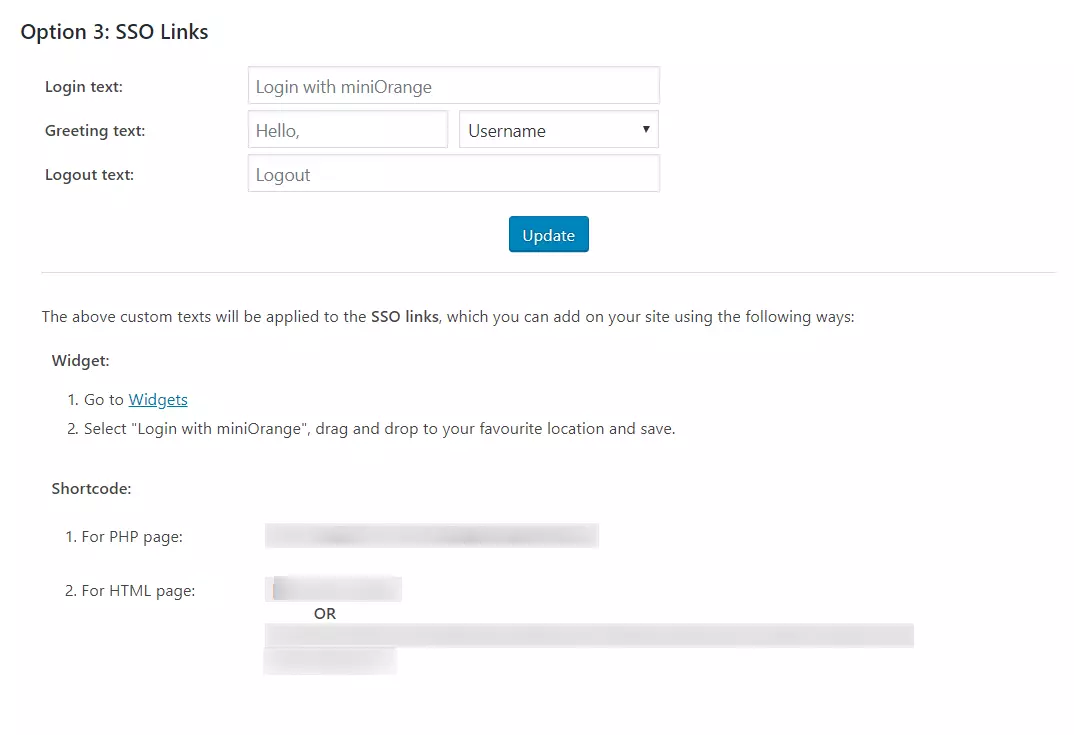
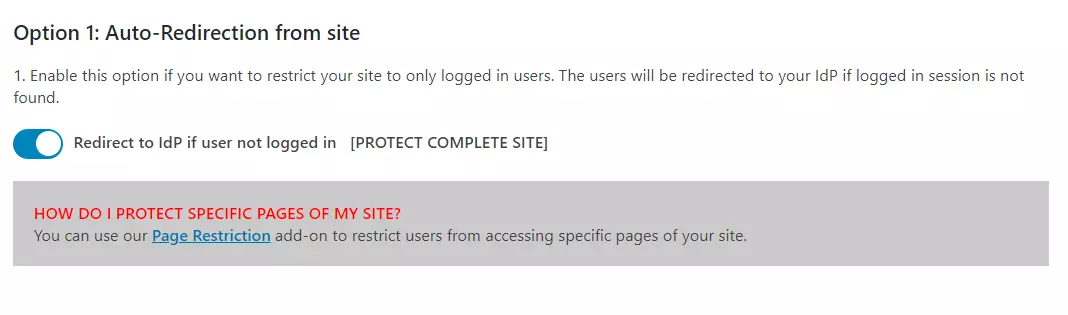
In the Standard plugin you can enable SP-initiated SSO using the following options.
You have successfully configured WordPress as SAML SP for achieving LastPass SSO login into your WordPress Site.
In this Guide, you have successfully configured SAML Single Sign-On (LastPass SSO Login for WordPress) using LastPass as IdP and WordPress as SP using miniOrange plugin-SAML Single Sign-On – SSO Login.This solution ensures that you are ready to roll out secure access to your WordPress site using LastPass login credentials within minutes. You can login in WordPress with LastPass Idp credentials through SAML SSO.
Related Articles


 Sign Up