Guide to Configure ASP.NET Core SAML SSO using Salesforce as IDP
Overview
ASP.NET Core SAML Single Sign-On (SSO) middleware gives the ability to enable SAML Single Sign-On for your ASP.NET core applications. Using Single Sign-On you can use only one password to access your ASP.NET core application and services. Our middleware is compatible with all the SAML compliant Identity providers. Here we will go through a step-by-step guide to configure Single Sign-On (SSO) between ASP.NET Core and Salesforce considering Salesforce as IdP.
Salesforce SSO for Contacts, Accounts and Custom Objects
Allow your partners, contacts, accounts or any other custom object records to login and access applications like WordPress, Shopify, JIRA, Confluence, etc. using Salesforce record as their identity for SSO authentication.
Salesforce SSO using Custom Objects as Identity SourcePlatform Support: The ASP.NET Core SAML middleware supports ASP.NET Core 2.0 and above. It supports all the ASP.NET Core platforms, including Windows, Linux and macOS.
- Trial
- Enterprise
Pre-requisites : Download And Installation
- Version .NET 5 & Above
- Version .NET Core 2.1 & .NET Core 3.1
- .NET Framework
PM> NuGet\Install-Package miniOrange.SAML.SSO
> dotnet add package miniOrange.SAML.SSO
Note: To integrate the miniOrange ASP.NET SAML SSO middleware in your application, you will be required to add the below namespaces, services and middleware in your project, below is a sample implementation for reference.
Include only the highlighted section below in the Program.cs file of your application.
                      using miniOrange.saml;


                      using System.Reflection


                      var builder=WebApplication.CreateBuilder(args);


                      // Add services to the container.


                      builder.Services.AddRazorPages();


                      builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


                      var app = builder.Build();


                            if(!app.Environment.IsDevelopment())


                      {


                        app.UseExceptionHandler("/Error");


                        app.UseHsts();


                      }


                      app.UseHttpsRedirection();


                     app.UseRouting();


                    app.UseAuthorization();


                    app.MapRazorPages();


                    app.UseCookiePolicy();


                    app.UseAuthentication();


                      #if NET9_0_OR_GREATER

  app.MapStaticAssets();

  #else

  app.UseStaticFiles();

  #endif


                    app.UseminiOrangeSAMLSSOMiddleware();


                    app.Run();
PM> NuGet\Install-Package miniOrange.SAML.SSO
> dotnet add package miniOrange.SAML.SSO
Note: To integrate the miniOrange ASP.NET SAML SSO middleware in your application, you will be required to add the below namespaces, services and middleware in your project, below here is a sample.
Include only the highlighted section below in the Program.cs file of your application.
           using miniOrange.saml;

                      using System.Reflection;


                      public class Startup

                      {


                        public Startup(IConfiguration configuration)

                        {

                          Configuration = configuration;

                        }

                        public IConfiguration Configuration { get; }


                        // This method gets called by the runtime. Use this method to add services to the container.

                        public void ConfigureServices(IServiceCollection services)

                        {

                          services.AddRazorPages();

                          services.AddminiOrangeServices(Assembly.GetExecutingAssembly());

                        }


                        // This method gets called by the runtime. Use this method to configure the HTTP request pipeline.

                        public void Configure(IApplicationBuilder app, IWebHostEnvironment env)

                        {

                          if (env.IsDevelopment())

                          {

                            app.UseDeveloperExceptionPage();

                          }

                          else

                          {

                            app.UseExceptionHandler("/Error");

                            // The default HSTS value is 30 days. You may want to change this for production scenarios, see         https://aka.ms/aspnetcore-hsts.

                            app.UseHsts();

                          }


                          app.UseHttpsRedirection();


                          app.UseCookiePolicy();

                          app.UseAuthentication();


                          #if NET9_0_OR_GREATER

                          app.MapStaticAssets();

                          #else

                          app.UseStaticFiles();

                          #endif


                          app.UseminiOrangeSAMLSSOMiddleware();


                          app.UseRouting();

                          app.UseAuthorization();

                          app.UseEndpoints(endpoints =>

                          {

                            endpoints.MapRazorPages();

                          });

                        }

                      }
Pre-requisites : Download And Installation
- Version .NET 5 & Above
- Version .NET Core 2.1 & .NET Core 3.1
- .NET Framework
- Login to http://portal.miniorange.com/ and navigate to the Downloads tab. From there, locate your purchased plugin and click on Download Plugin to download the plugin zip file.

- Extract the Downloaded zip file in your machine and place the nuget package file (.nupkg file) in a some folder like "C:\miniOrangePackages"
- Run the following command in your VS terminal to add it as a package source:
dotnet nuget add source C:\miniOrangePackages--name miniOrangePackage
- Open your Project in the terminal:
cd C:\Path\To\YourProject
- Install the Package in your project using the below command:
dotnet add package miniOrange.SAML.SSO --source miniOrangePackage
OR
- After placing the NuGet package (.nupkg file) in a local folder, instead of using the terminal, you can also install it using Visual Studio by following the steps below:
- Open your .NET application in Visual Studio, click on Tools in the top navigation bar, and navigate to NuGet Package Manager → Manage NuGet Packages for Solution.

- A new window will open; click on the gear icon next to the Package source dropdown.

- A pop-up window will open; select Package Sources from the left navigation panel, click on the plus (+) icon, enter a name for the package source, provide the path of the folder where you placed the NuGet package in the Source field, then click Update and finally click OK to save the changes, as shown in the image.

- After closing the pop-up window, select the newly added package source from the Package source dropdown.

- Now click on the Browse tab, search for miniOrange.SAML.SSO, select the package from the results, and click Install.

- Note: To integrate the miniOrange ASP.NET SAML SSO middleware in your application, you will be required to add the below namespaces, services and middleware in your project, below is a sample implementation for reference.
Include only the highlighted section below in the Program.cs file of your application.
                      using miniOrange.saml;


                      using System.Reflection


                      var builder=WebApplication.CreateBuilder(args);


                      // Add services to the container.


                      builder.Services.AddRazorPages();


                      builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


                      var app = builder.Build();


                            if(!app.Environment.IsDevelopment())


                      {


                        app.UseExceptionHandler("/Error");


                        app.UseHsts();


                      }


                      app.UseHttpsRedirection();


                     app.UseRouting();


                    app.UseAuthorization();


                    app.MapRazorPages();


                    app.UseCookiePolicy();


                    app.UseAuthentication();


                      #if NET9_0_OR_GREATER

  app.MapStaticAssets();

  #else

  app.UseStaticFiles();

  #endif


                    app.UseminiOrangeSAMLSSOMiddleware();


                    app.Run();
- Login to http://portal.miniorange.com/ and navigate to the Downloads tab. From there, locate your purchased plugin and click on Download Plugin to download the plugin zip file.
- Extract the Downloaded zip file in your machine and place the nuget package file (.nupkg file) in a some folder like "C:\miniOrangePackages"
- Run the following command in your VS terminal to add it as a package source:
dotnet nuget add source C:\miniOrangePackages--name miniOrangePackage
- Open your Project in the terminal:
cd C:\Path\To\YourProject
- Install the Package in your project using the below command:
dotnet add package miniOrange.SAML.SSO --source miniOrangePackage
OR
- After placing the NuGet package (.nupkg file) in a local folder, instead of using the terminal, you can also install it using Visual Studio by following the steps below:
- Open your .NET application in Visual Studio, click on Tools in the top navigation bar, and navigate to NuGet Package Manager → Manage NuGet Packages for Solution.
- A new window will open; click on the gear icon next to the Package source dropdown.
- A pop-up window will open; select Package Sources from the left navigation panel, click on the plus (+) icon, enter a name for the package source, provide the path of the folder where you placed the NuGet package in the Source field, then click Update and finally click OK to save the changes, as shown in the image.
- After closing the pop-up window, select the newly added package source from the Package source dropdown.
- Now click on the Browse tab, search for miniOrange.SAML.SSO, select the package from the results, and click Install.
- Note: To integrate the miniOrange ASP.NET SAML SSO middleware in your application, you will be required to add the below namespaces, services and middleware in your project, below is a sample implementation for reference.
Include only the highlighted section below in the Program.cs file of your application.
           using miniOrange.saml;

                      using System.Reflection;


                      public class Startup

                      {


                        public Startup(IConfiguration configuration)

                        {

                          Configuration = configuration;

                        }

                        public IConfiguration Configuration { get; }


                        // This method gets called by the runtime. Use this method to add services to the container.

                        public void ConfigureServices(IServiceCollection services)

                        {

                          services.AddRazorPages();

                          services.AddminiOrangeServices(Assembly.GetExecutingAssembly());

                        }


                        // This method gets called by the runtime. Use this method to configure the HTTP request pipeline.

                        public void Configure(IApplicationBuilder app, IWebHostEnvironment env)

                        {

                          if (env.IsDevelopment())

                          {

                            app.UseDeveloperExceptionPage();

                          }

                          else

                          {

                            app.UseExceptionHandler("/Error");

                            // The default HSTS value is 30 days. You may want to change this for production scenarios, see         https://aka.ms/aspnetcore-hsts.

                            app.UseHsts();

                          }


                          app.UseHttpsRedirection();


                          app.UseCookiePolicy();

                          app.UseAuthentication();


                          #if NET9_0_OR_GREATER

                          app.MapStaticAssets();

                          #else

                          app.UseStaticFiles();

                          #endif


                          app.UseminiOrangeSAMLSSOMiddleware();


                          app.UseRouting();

                          app.UseAuthorization();

                          app.UseEndpoints(endpoints =>

                          {

                            endpoints.MapRazorPages();

                          });

                        }

                      }
Configuration Steps
Step by Step guide for ASP.NET Core SAML SSO using Salesforce as Identity Provider.
1. Access the .NET SAML Plugin Dashboard
- After integration, open your browser and browse the connector dashboard with the URL below:
http(s)<your-dotnet-application-base-url>?ssoaction=config
- If the registration page or login page pops up, you have successfully added the miniOrange SAML SSO middleware in your application.

- Register or log in with your account by clicking the Register button to configure the middleware.
- After successful registration, you will receive a trial license key on your registered email address.
- To activate the middleware, you can either:
- Enter the license key received via email in the provided input field.
- Upload the license file that you downloaded by clicking on the Click Here button.
OR

- Then, check the box "I have read the above conditions and I want to activate the middleware", and click the Activate License button.

- After integration, open your browser and browse the connector dashboard with the URL below:
http(s)<your-dotnet-application-base-url>?ssoaction=config
- If the login page pops up, you have successfully added the miniOrange SAML SSO middleware in your application.

- Log in with your licensed miniOrange account to configure the middleware.
- After logging in, the Account Setup dashboard will open. Enter the license key to activate the plugin, which you will receive after logging in to portal.miniorange.com and navigating to Manage License → License Keys.

- Then, check the box "I have read the above two conditions and I want to activate the plugin", and click the Activate License button.

2. Provide .NET Application Metadata to Salesforce Identity Provider
There are two ways detailed below with which you can get the SAML SP metadata to configure onto your Identity Provider end.
A] Using SAML metadata URL or metadata file
- In the Plugin Settings menu, look for Service Provider Settings. Under that, you can find the metadata URL as well as the option to download the SAML metadata.
- Copy metadata URL or download the metadata file to configure the same on your identity provider end.
- You may refer to the screenshot below:

B] Uploading metadata manually
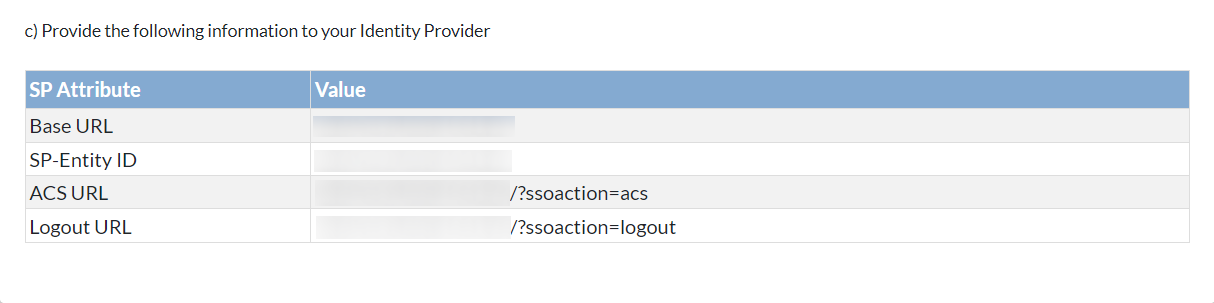
- From the Service Provider Settings section, you can manually copy the service provider metadata like SP Entity ID, ACS URL, Single Logout URL and share it with your identity provider for configuration.
- You may refer to the screenshot below:
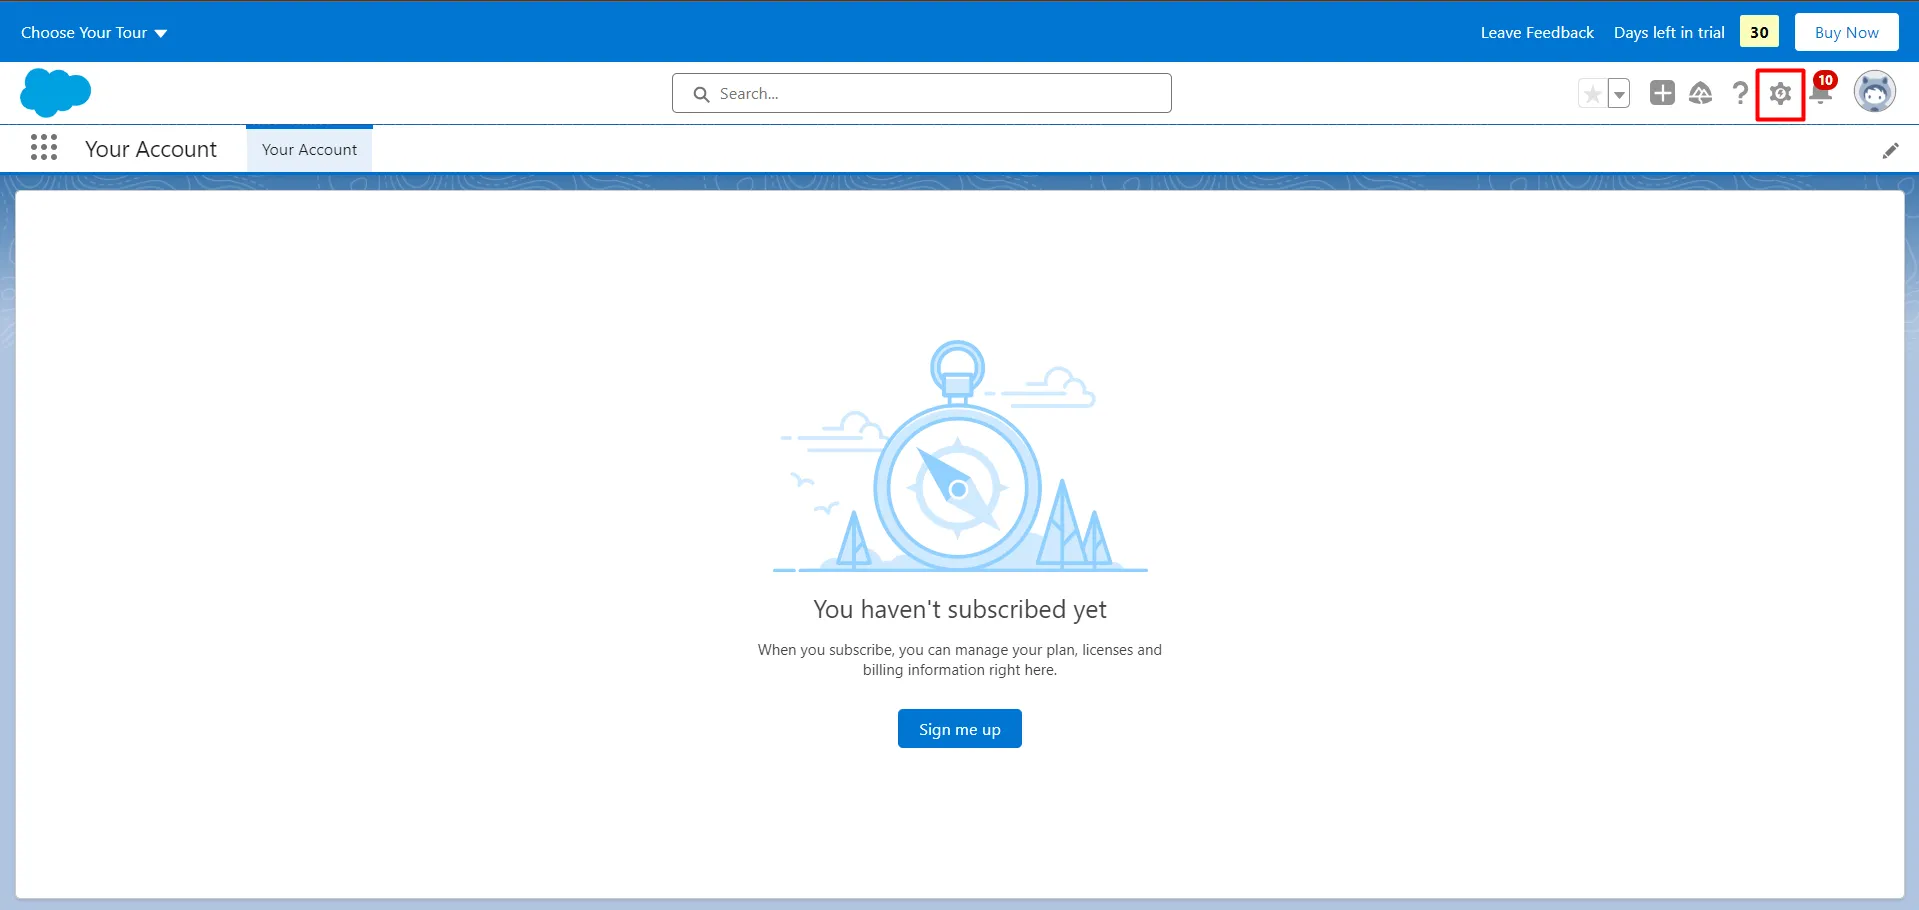
- Log into your Salesforce account as admin.
- Switch to Salesforce Lightning mode from profile menu and then go to the Setup page by clicking on setup button.
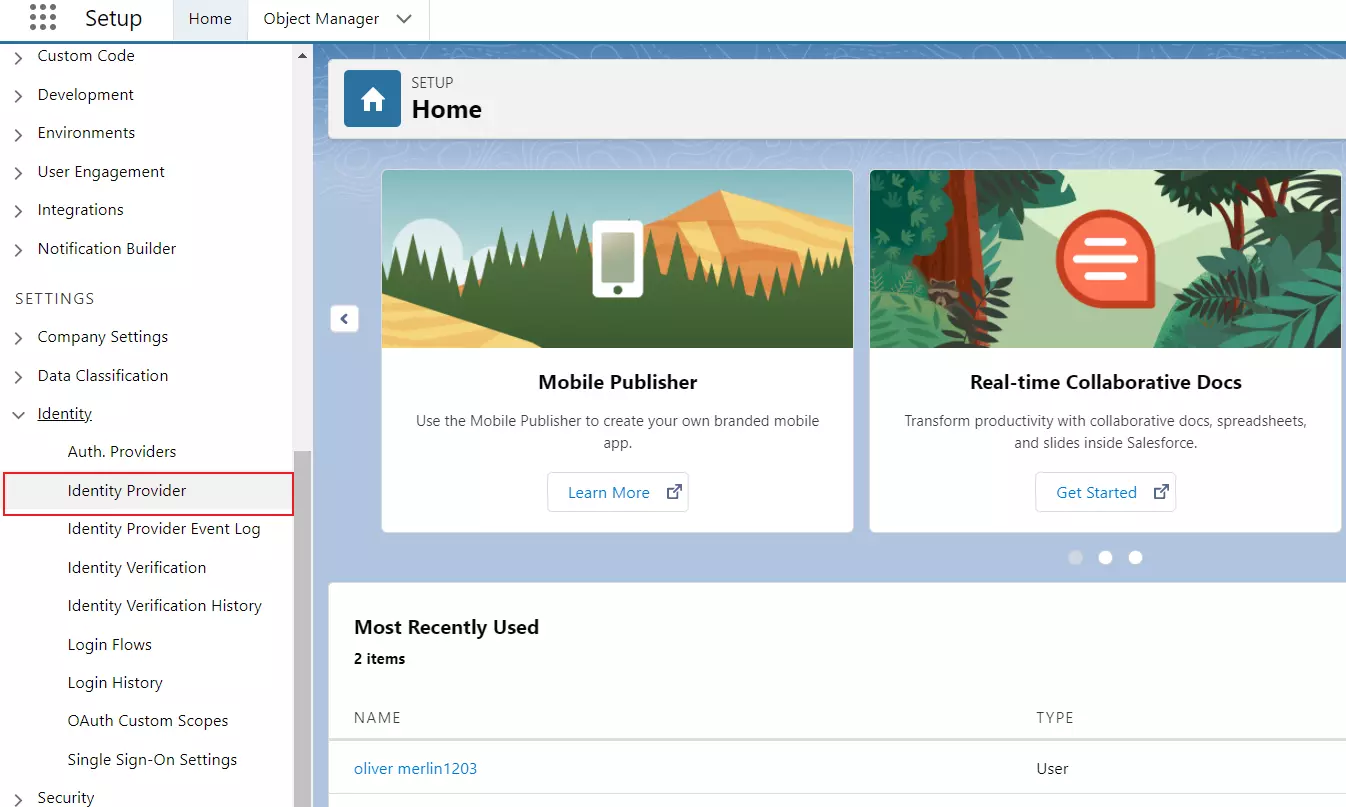
- From the left pane, select Settings Tab and click on Identity Provider.
- Click on Enable Identity Provider.
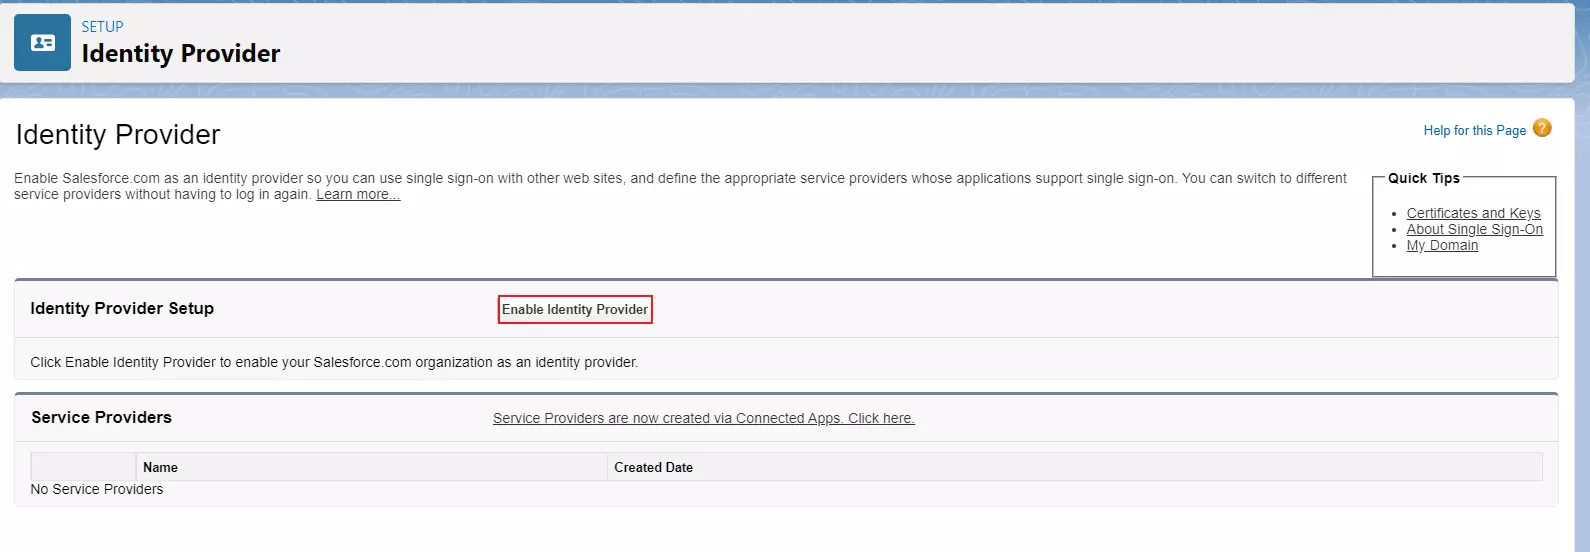
- In the Service Provider section, click on the link to create the Service Provider using Connected Apps.
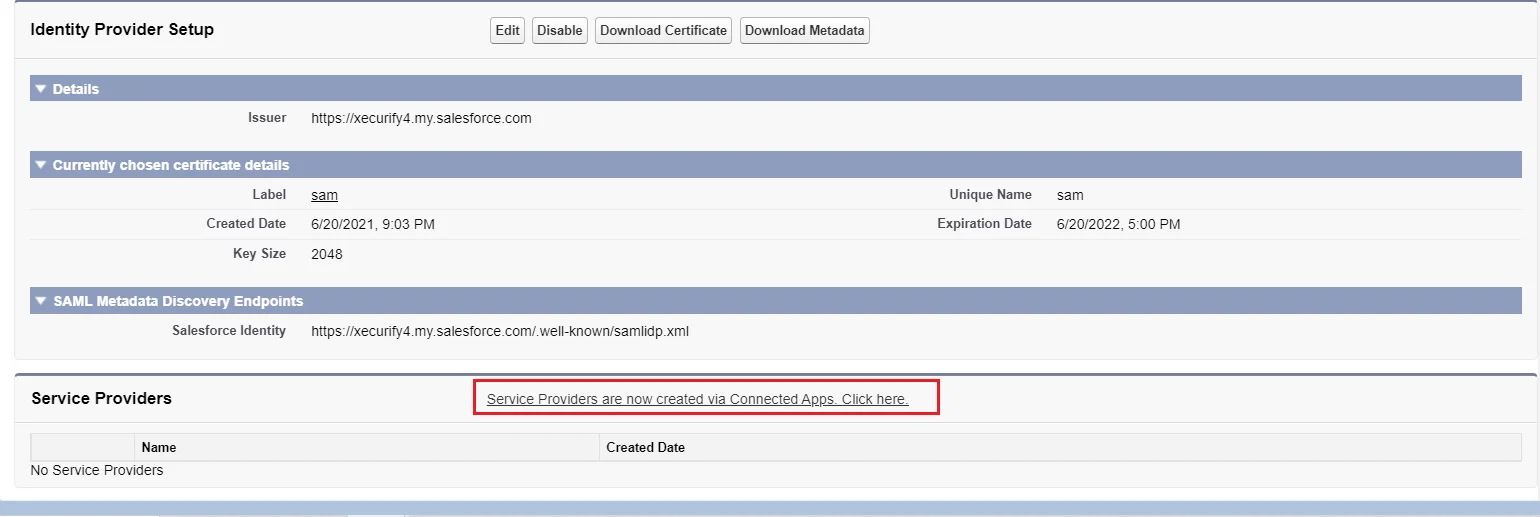
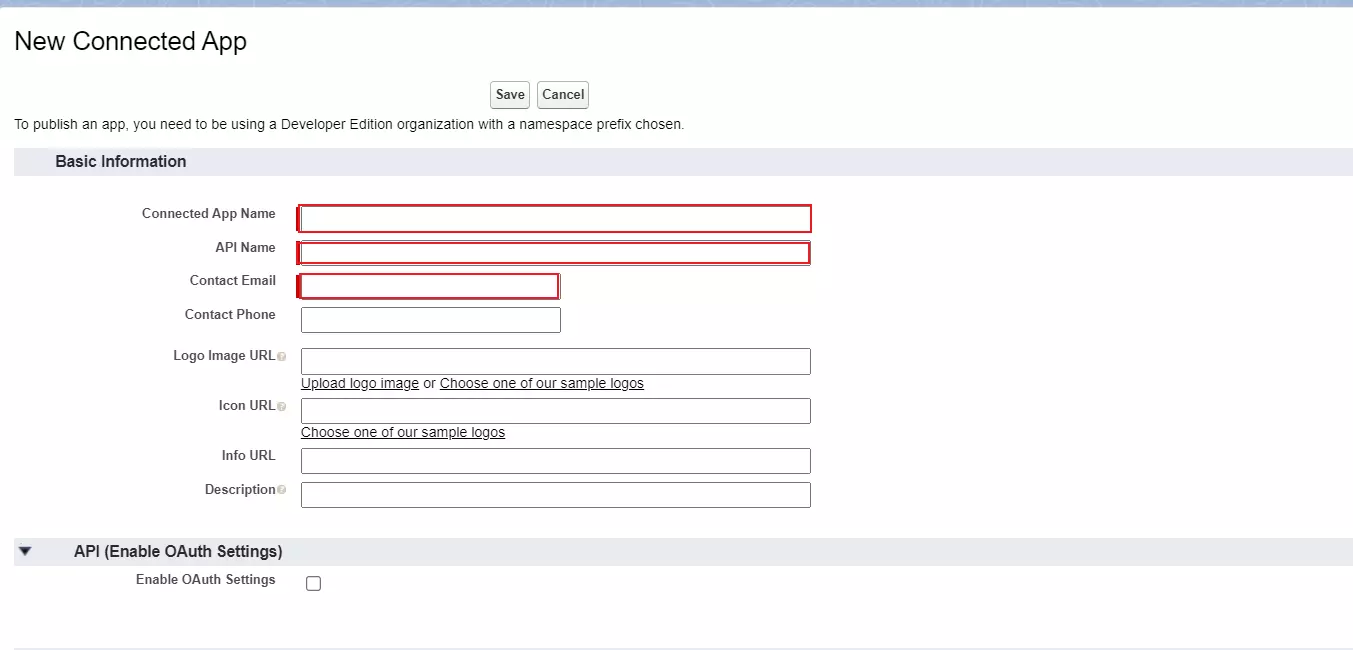
- Enter Connected App Name, API Name and Contact Email.
| Connected App Name | Provide a name for Connected App |
| API Name | Provide a API name |
| Contact Email | Provide a Contact Email |
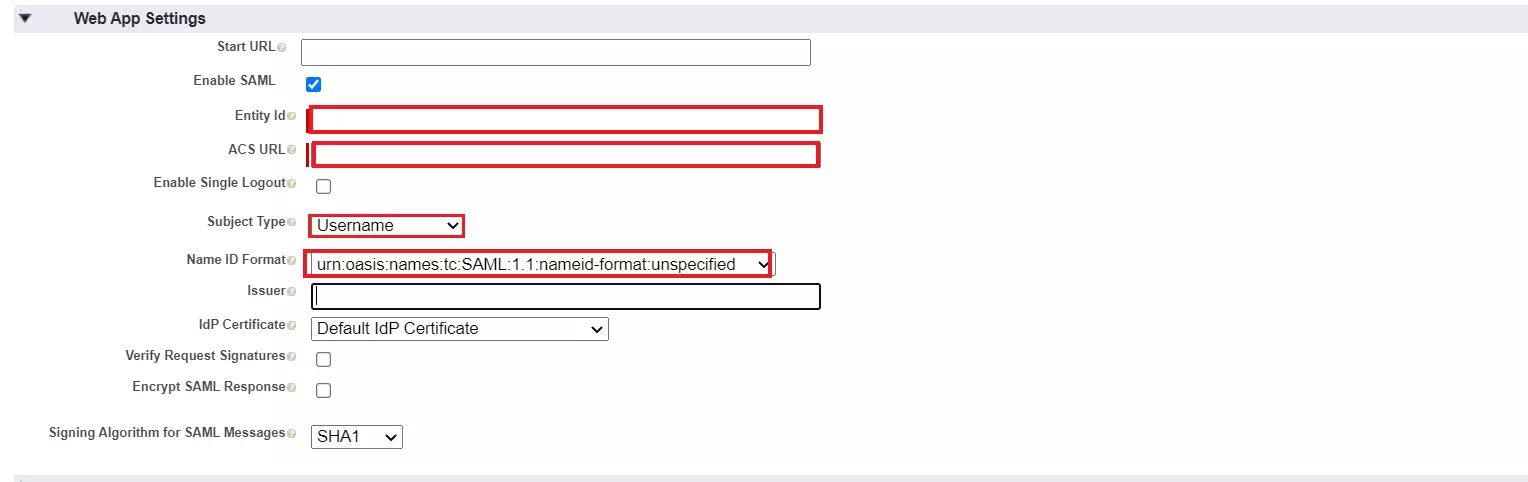
- Under the Web App Settings, check the Enable SAML checkbox and enter the following values:
| Enable SAML | Checked |
| Entity ID | SP-EntityID / Issuer from Service Provider Metadata tab of the Plugin |
| ACS URL | ACS (AssertionConsumerService) URL from Service Provider Metadata tab of the Plugin |
| Subject Type | Username |
| Name ID Format | urn:oasis:names:tc:SAML:2.0:nameid-format:unspecified |
- Click on Save to save the configuration.
- Now from the left pane, under Platform Tools section select Connected Apps.
- Then select Manage Connected Apps and click on the app you just created.
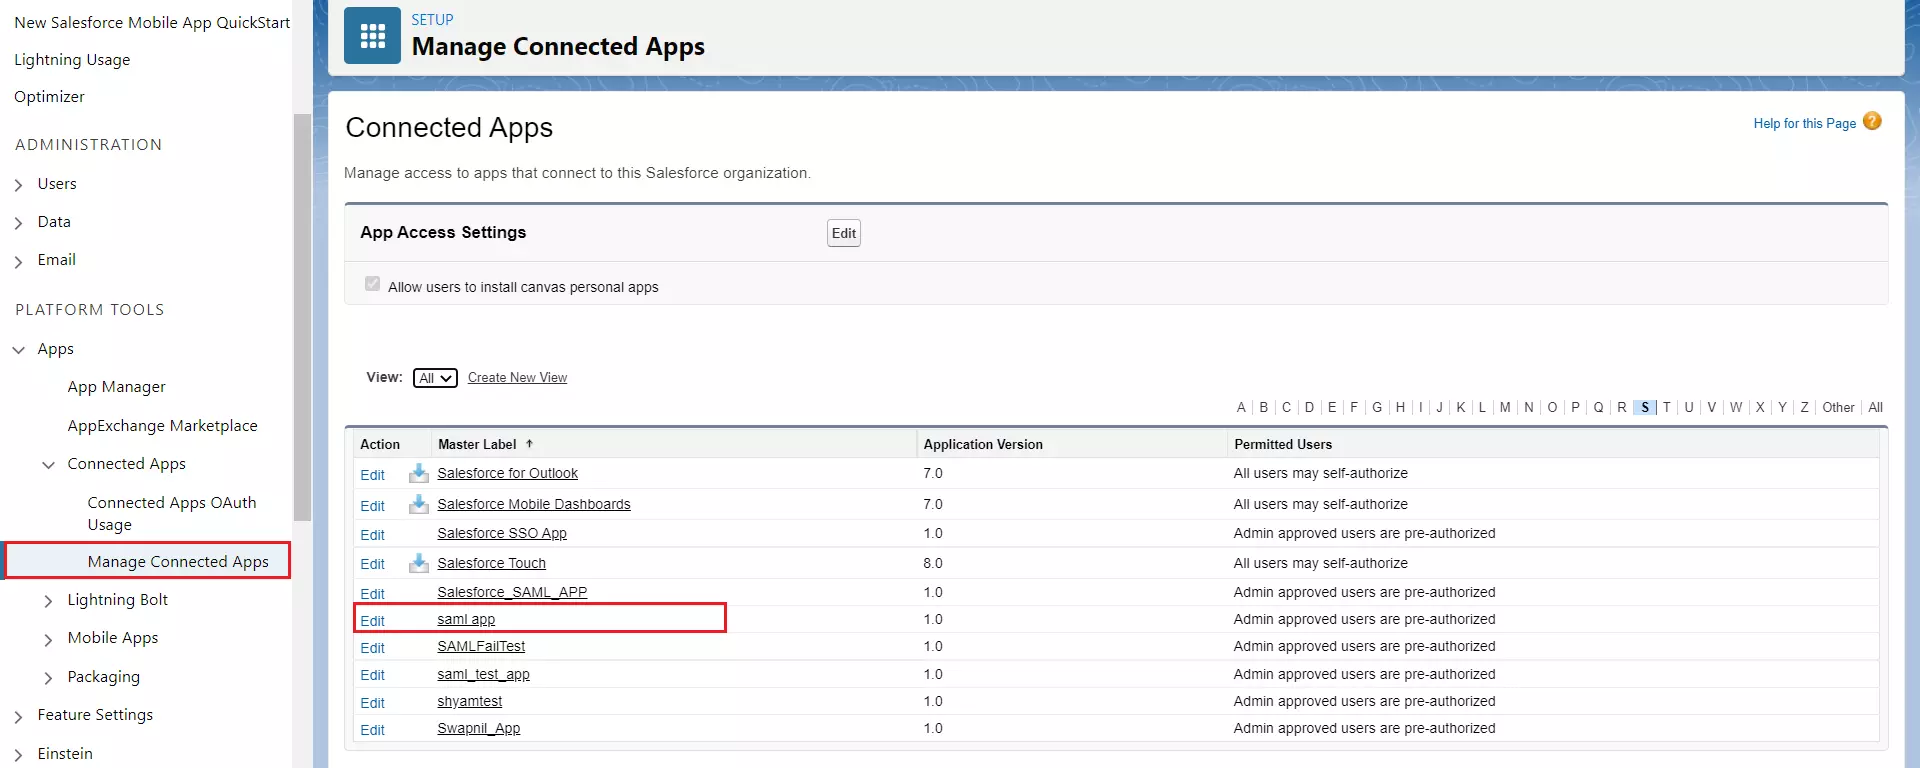
- In the Profiles section click Manage Profiles button.
- Assign the Profiles you want to give access to log in through this app.
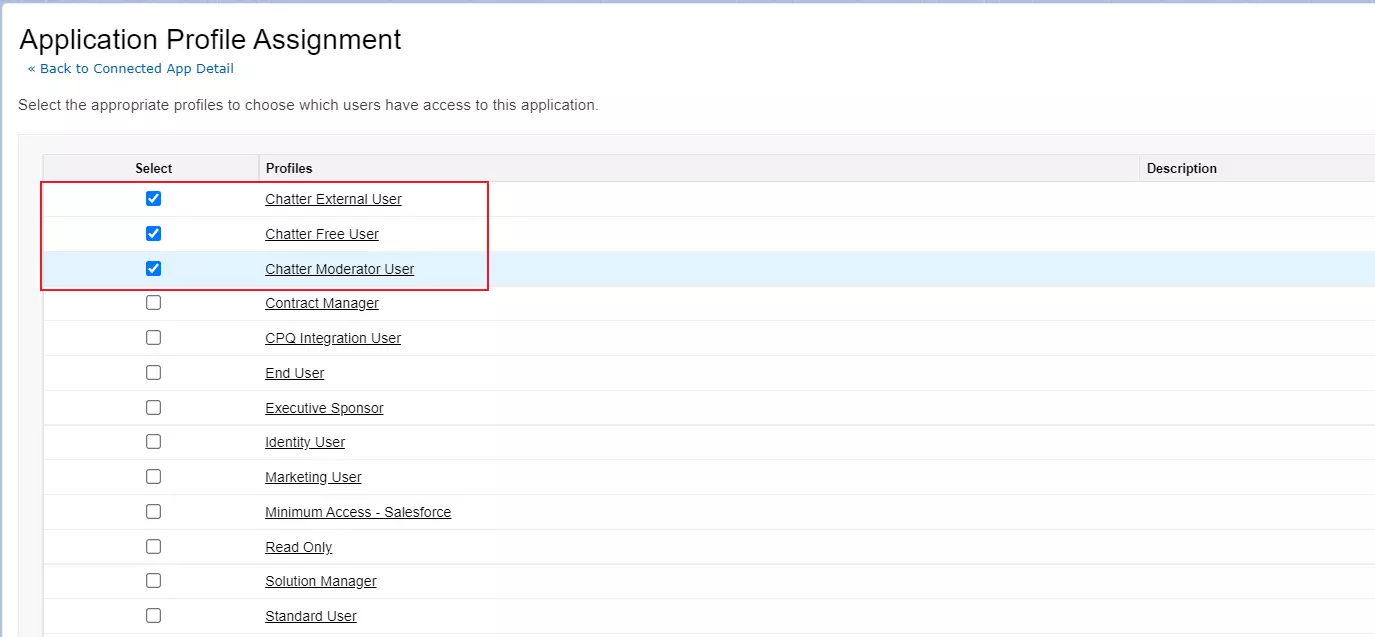
- Under SAML Login Information, click on Download Metadata.
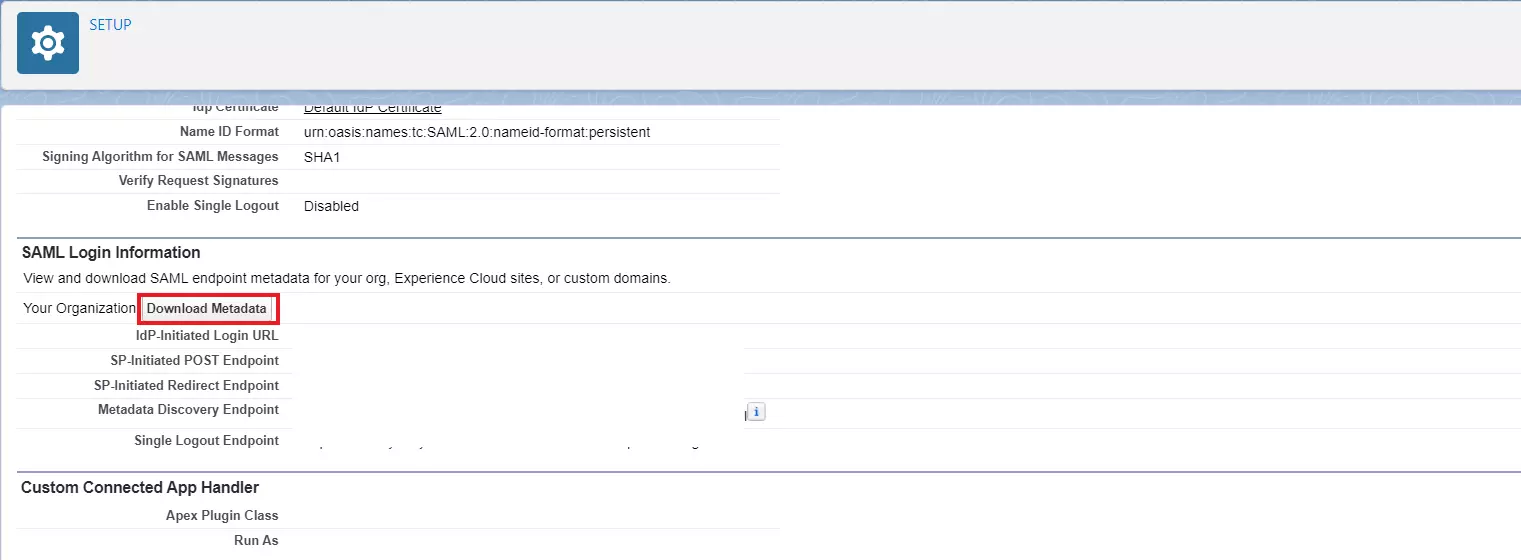
- Keep this metadata handy for configuring the Service Provider.
A] Using SAML metadata URL or metadata file
- In the Plugin Settings menu, look for Service Provider Settings. Under that, you can find the metadata URL as well as the option to download the SAML metadata.
- Copy metadata URL or download the metadata file to configure the same on your identity provider end.
- You may refer to the screenshot below:

B] Uploading metadata manually
- From the Service Provider Settings section, you can manually copy the service provider metadata like SP Entity ID, ACS URL, Single Logout URL, and share it with your Identity Provider for configuration.
- ou can also download the SP Certificate by clicking on Download SP Cert and provide it to your Identity Provider if required.
- Under the Encryption Certificate section, select the appropriate certificate type as per your requirement.
- After completing the above steps, click on Save to apply the configuration.
- You may refer to the screenshot below:

- Log into your Salesforce account as admin.
- Switch to Salesforce Lightning mode from profile menu and then go to the Setup page by clicking on setup button.
- From the left pane, select Settings Tab and click on Identity Provider.
- Click on Enable Identity Provider.
- In the Service Provider section, click on the link to create the Service Provider using Connected Apps.
- Enter Connected App Name, API Name and Contact Email.
| Connected App Name | Provide a name for Connected App |
| API Name | Provide a API name |
| Contact Email | Provide a Contact Email |
- Under the Web App Settings, check the Enable SAML checkbox and enter the following values:
| Enable SAML | Checked |
| Entity ID | SP-EntityID / Issuer from Service Provider Metadata tab of the Plugin |
| ACS URL | ACS (AssertionConsumerService) URL from Service Provider Metadata tab of the Plugin |
| Subject Type | Username |
| Name ID Format | urn:oasis:names:tc:SAML:2.0:nameid-format:unspecified |
- Click on Save to save the configuration.
- Now from the left pane, under Platform Tools section select Connected Apps.
- Then select Manage Connected Apps and click on the app you just created.
- In the Profiles section click Manage Profiles button.
- Assign the Profiles you want to give access to log in through this app.
- Under SAML Login Information, click on Download Metadata.
- Keep this metadata handy for configuring the Service Provider.
3. Configure Salesforce Identity Provider Metadata in .NET Application
- Click on the Add new IDP button to configure a new Identity Provider.

- Under the Plugin Settings tab, select Salesforce as your identity provider from the list shown.
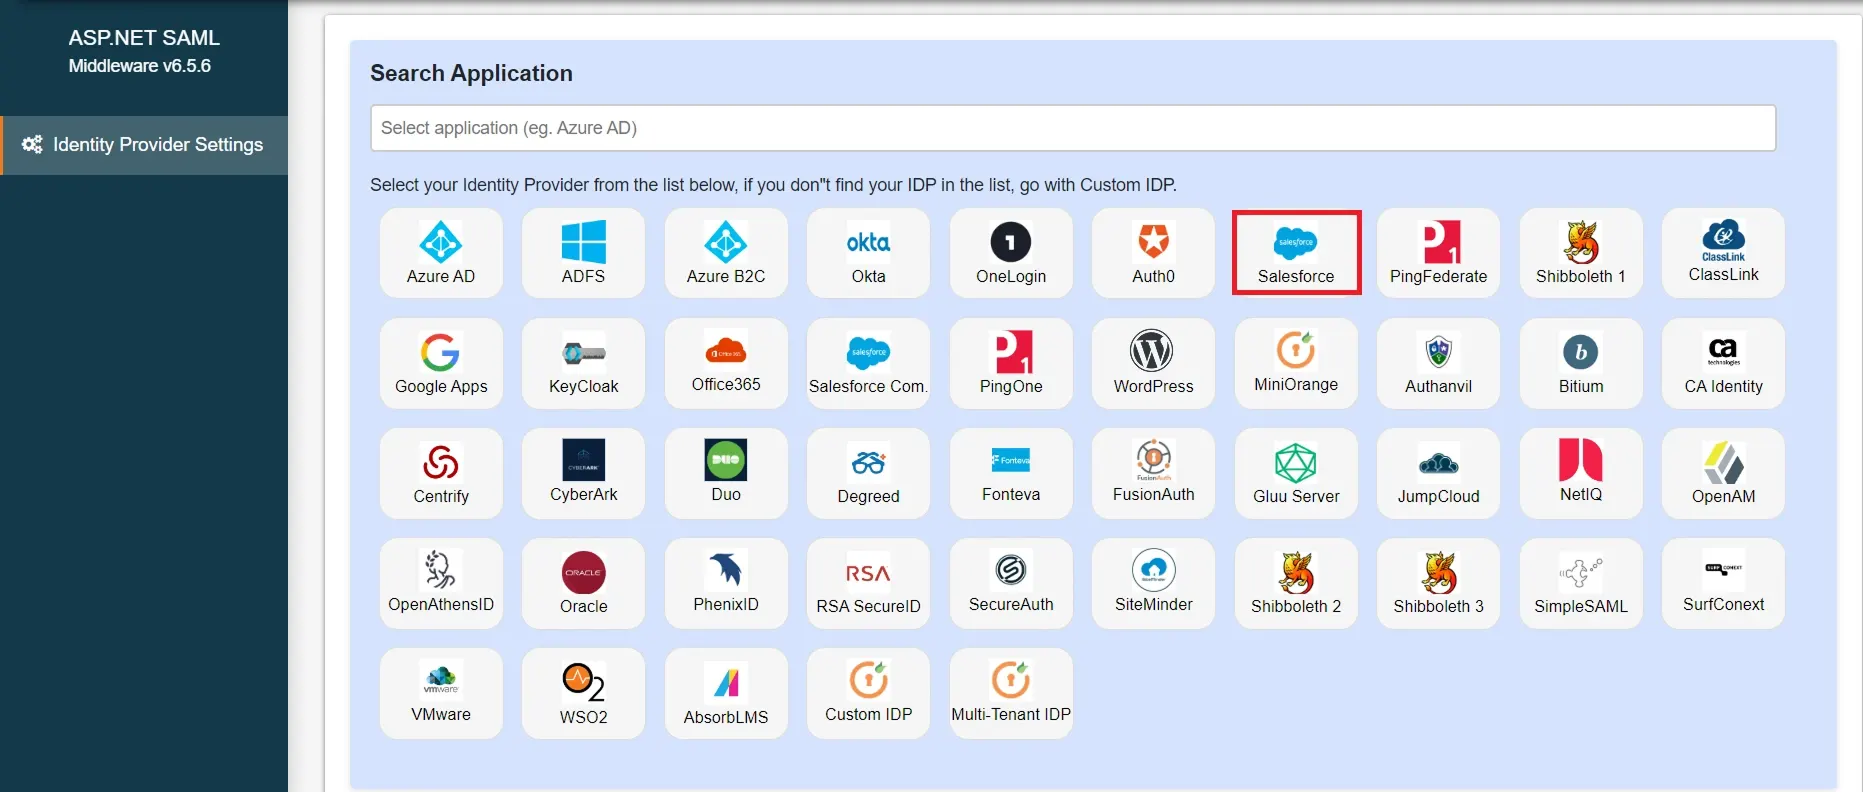
There are two ways detailed below with which you can configure your SAML Identity Provider metadata in the middleware.
A] Upload metadata using the Upload IDP Metadata button:
- If your identity provider has provided you with the metadata URL or metadata file (.xml format only), then you can simply configure the identity provider metadata in the middleware using the Upload IDP Metadata option.
- Copy metadata URL or download the metadata file to configure the same on your identity provider end.
- You may refer to the screenshot below:
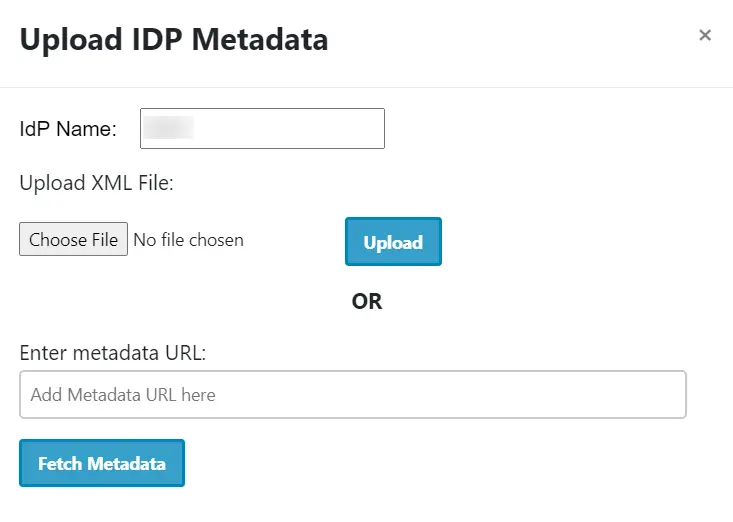
- You can choose any one of the options according to the metadata format you have available.
B] Configure the identity provider metadata manually:
- After configuring your Identity Provider, it will provide you with IDP Entity ID, IDP Single Sign On URL and SAML X509 Certificate fields respectively.
- Click Save to save your IDP details.
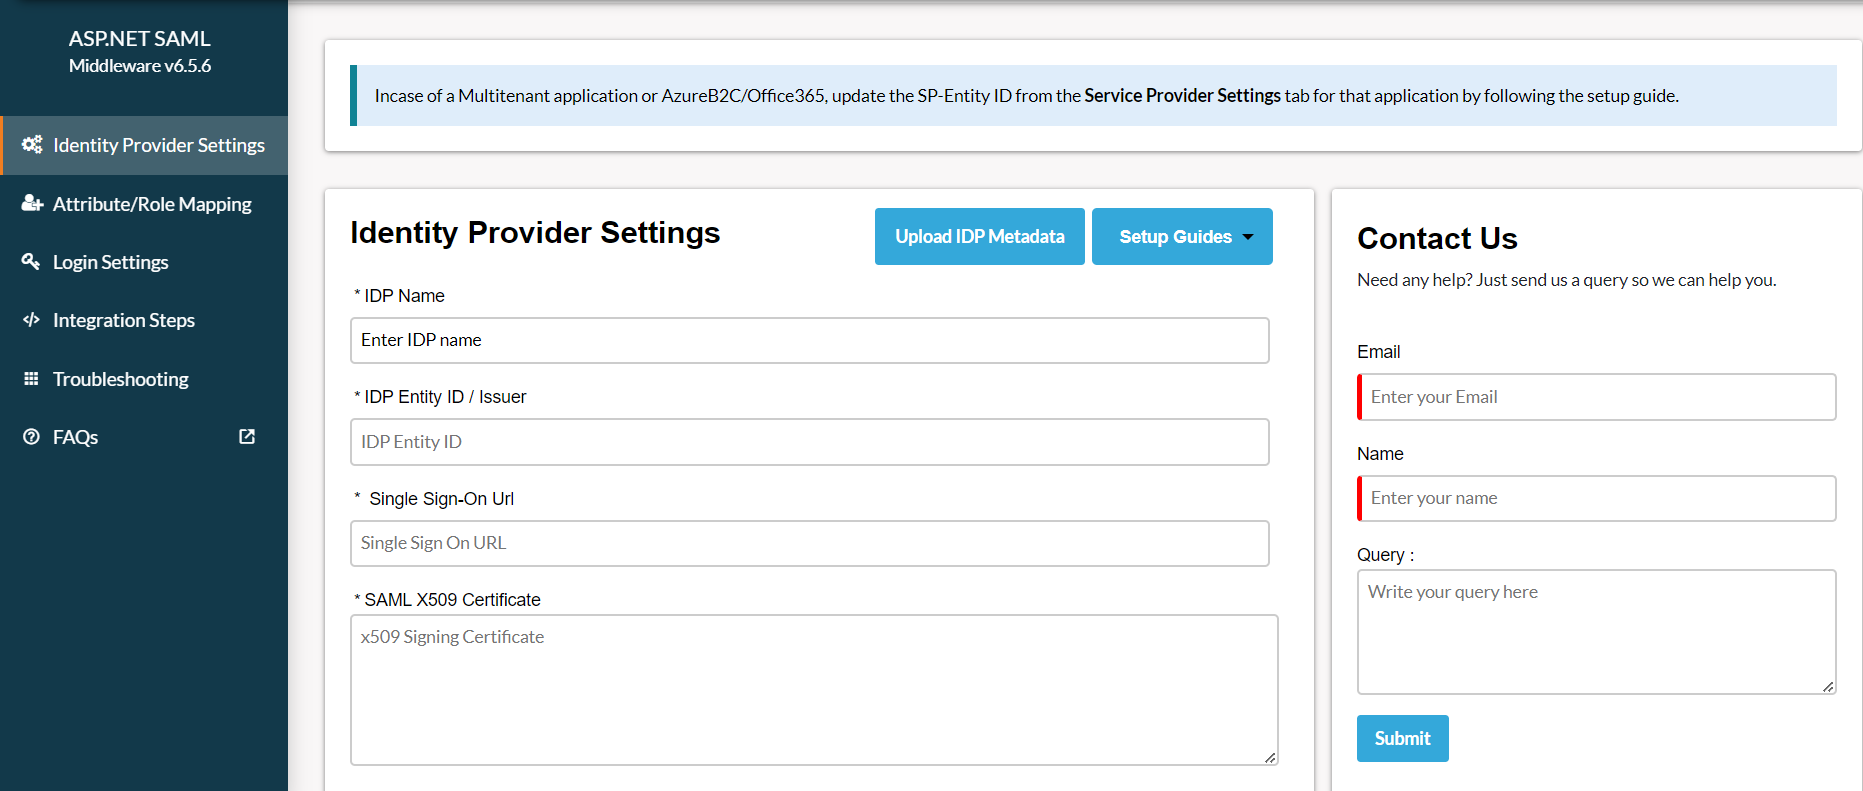
- Click on the Add new IDP button to configure a new Identity Provider.

- Under the Plugin Settings tab, select Salesforce as your identity provider from the list shown.
There are two ways detailed below with which you can configure your SAML Identity Provider metadata in the middleware.
A] Upload metadata using the Upload IDP Metadata button:
- If your identity provider has provided you with the metadata URL or metadata file (.xml format only), then you can simply configure the identity provider metadata in the middleware using the Upload IDP Metadata option.
- Copy metadata URL or download the metadata file to configure the same on your identity provider end.
- You may refer to the screenshot below:

- You can choose any one of the options according to the metadata format you have available.
B] Configure the identity provider metadata manually:
- After configuring your Identity Provider, it will provide you with IDP Entity ID, IDP Single Sign On URL and SAML X509 Certificate fields respectively.
- Click Save to save your IDP details.

4. Testing SAML SSO
- After uploading the metadata details, navigate to the Identity Provider Settings section. Hover over the Select Actions dropdown and click on Test Configuration.

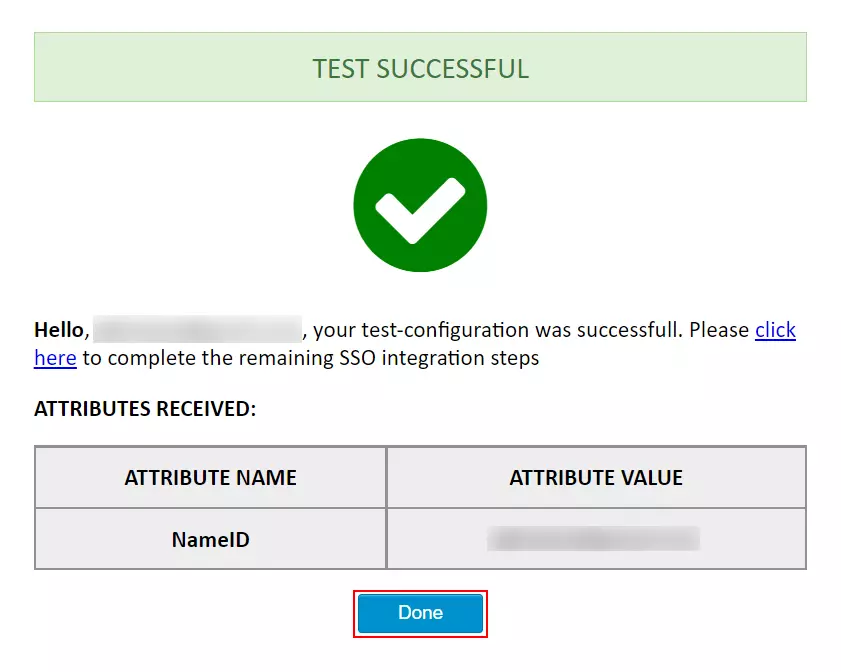
- The screenshot below shows a successful result. Click on SSO Integration to further continue with the SSO Integration.
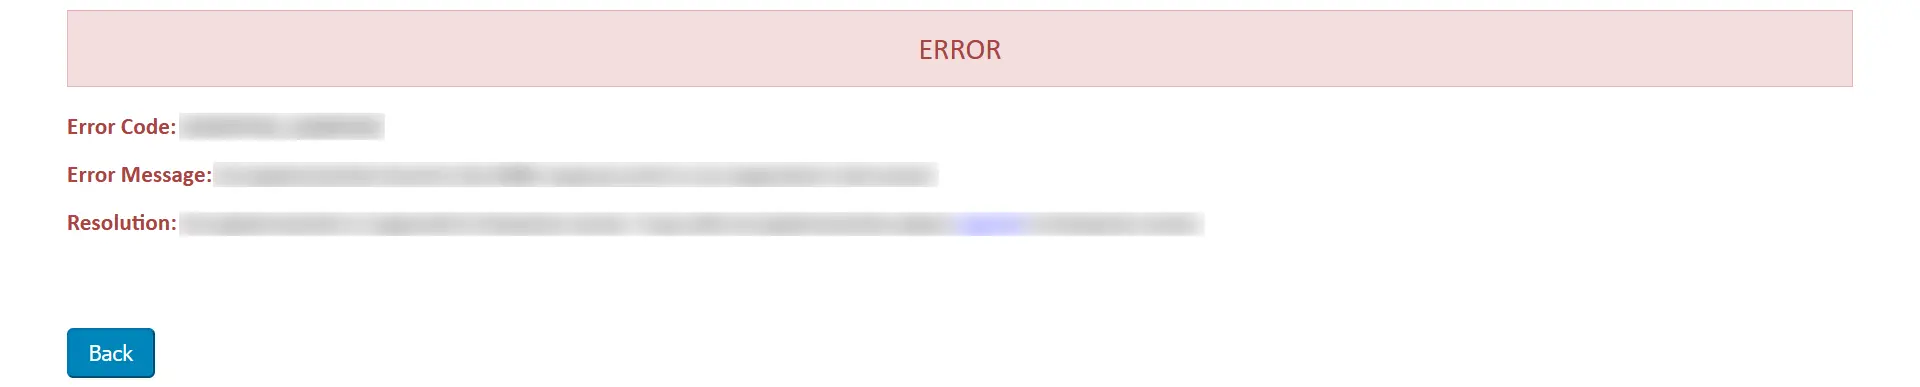
- If you are experiencing any error on the middleware end you’ll be shown with the window similar to below.
- To troubleshoot the error you can follow the below steps:
- Under Troubleshoot tab, enable the toggle to receive the plugin logs.
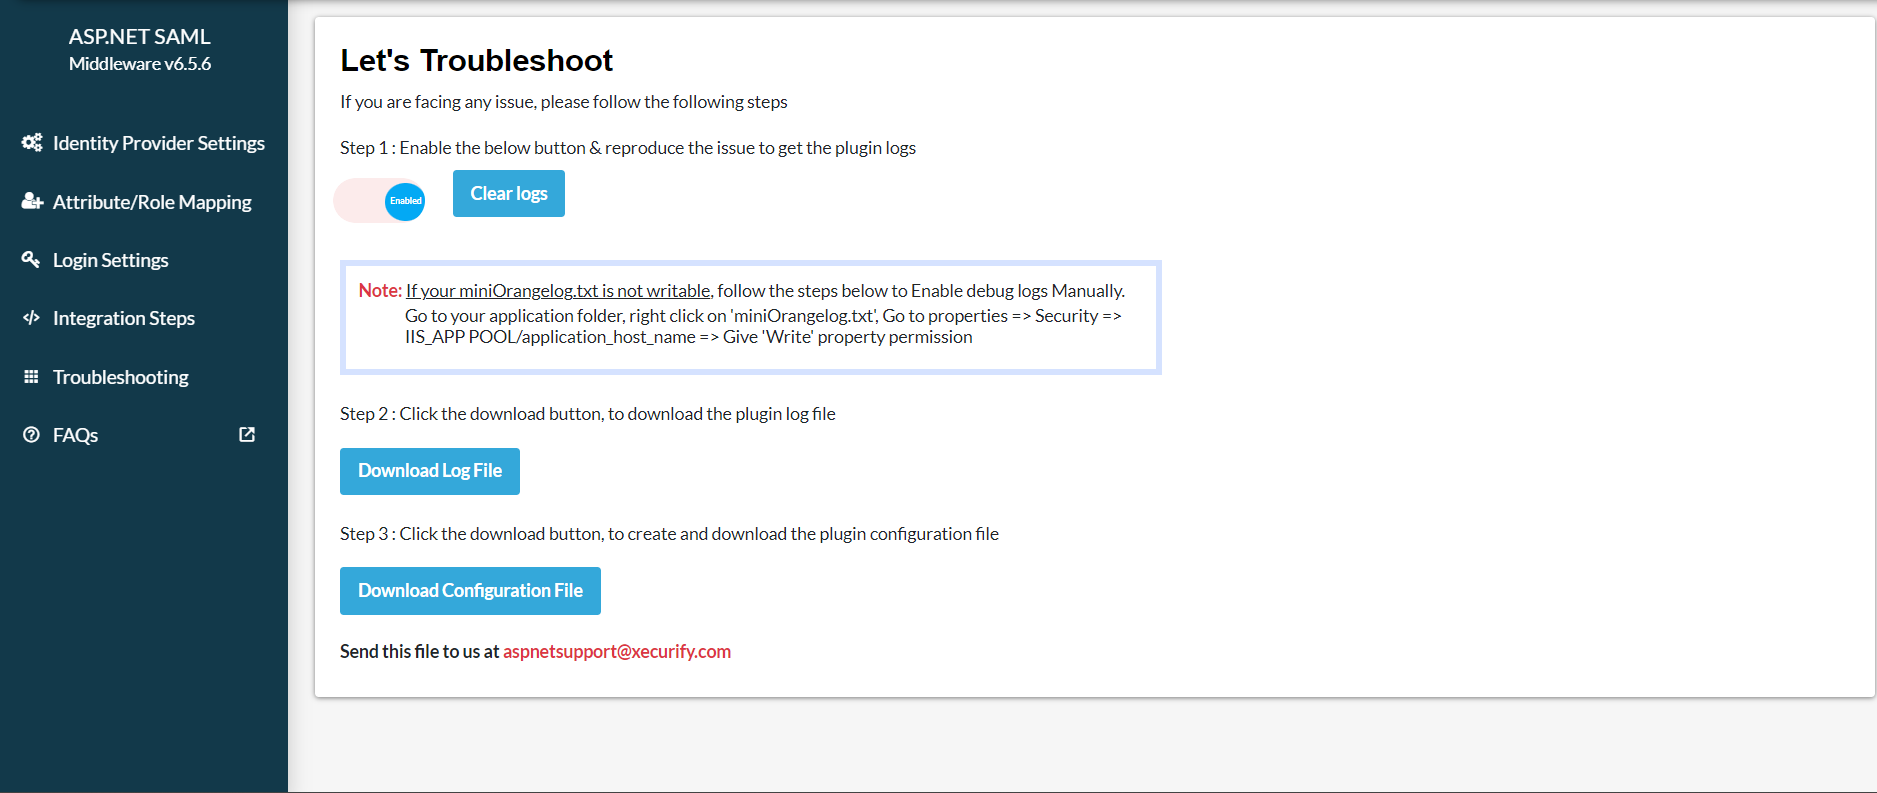
- Once enabled, you will be able to retrieve plugin logs by navigating to Plugin Settings tab and clicking on Test Configuration.
- Download the log file from the Troubleshoot tab to see what went wrong.
- You can share the log file with us at aspnetsupport@xecurify.com and our team will reach out to you to resolve your issue.
- After uploading the metadata details, navigate to the Identity Provider Settings section. Hover over the Select Actions dropdown and click on Test Configuration.

- The screenshot below shows a successful test result. Please click on click here to complete the remaining SSO integration steps.

- If you are experiencing any error on the middleware end, click on the Troubleshooting button.

- To troubleshoot the error, you can follow the below steps:
- Under the Troubleshoot tab, enable the toggle to receive the plugin logs and reproduce the issue.
- Download the log file by clicking on the Download Log File button to see what went wrong.

- You can share the log file with us at aspnetsupport@xecurify.com and our team will reach out to you to resolve your issue.
5. Attribute Mapping
- After testing the configuration, Map your application attributes with the Identity Provider (IdP) attributes.
- From the left-hand menu of the miniOrange ASP.NET SAML SSO Middleware, click on Attribute/Role Mapping tab as shown in the image.

- If you want to pass additional attributes from your IdP, enter the Attribute Name and corresponding Attribute Value under Custom Attribute Mapping.
- Note: All the mapped attributes will be stored in the session so that you can access them in your application.
- Once the attributes are mapped, click Save Attribute Mapping to apply changes.

- After testing the configuration, Map your application attributes with the Identity Provider (IdP) attributes.
- From the left-hand menu of the miniOrange ASP.NET SAML SSO Middleware, click on Attribute/Role Mapping tab as shown in the image.
- Map the required IdP attributes (such as Username, Email, Firstname, and Lastname) received in the SAML Response to their corresponding fields.

- Note: All the mapped attributes will be stored in the session so that you can access them in your application.
- Once the attributes are mapped, click Save Attribute Mapping to apply changes.
Custom Attribute Mapping
- If you want to pass additional attributes from your IdP, enter the Attribute Name and corresponding Attribute Value under Custom Attribute Mapping.
- From the Attribute Value (Claim) dropdown, select one of the claims you received in the Test Configuration results. For example: NameID.
- These claims correspond to the attributes sent by your Identity Provider (IdP).

- These claims correspond to the attributes sent by your Identity Provider (IdP).

- In the Attribute Name field, enter the name of the attribute as you want it to appear or be used in your .NET application.
- You can add multiple mappings if your application requires multiple attributes by clicking on the + button.
- After defining all the required mappings, click on Save Attribute Mapping to store the configuration.

- The plugin will now translate the incoming SSO claims from your Identity Provider (IdP) into the custom attribute names defined here.
Role Mapping
- In the Role Mapping section , enter the Group Attribute Name exactly as configured in your Identity Provider to fetch the user group information.
- Enter the Role Name received from the Identity Provider and map it to the appropriate Role Vaue field. In the Role Value field, enter the roles defined in your .NET application.
- For example: Map the IdP group Group1 or Group10 received under the UserGroups attribute to the corresponding role configured in your .NET application.
- After adding the required mappings, click on Save Role Mapping to save the configuration successfully.

Domain Restriction
- This feature can be used to restrict user access to the site based on the domain of their mapped “Email“ Attribute.
- In the Email Attribute field, enter the attribute name that contains the user's email address as received from your Identity Provider (IdP).

- In the Domain Name field, enter the domain(s) you want to allow or restrict, separated by commas if adding multiple domains.
- Enable the Restrict toggle based on your requirement to configure blacklist or whitelist access.
- After completing the configuration, click on Save Domains to save the settings successfully.

6. Integration Code
- This steps allow you to retrieve the SSO user information in your application in the form of user claims.
- You can also look the setup tour to understand how the SSO integration would work in your asp.net middleware application.
- Just copy-paste that code snippet wherever you want to access the user attributes.
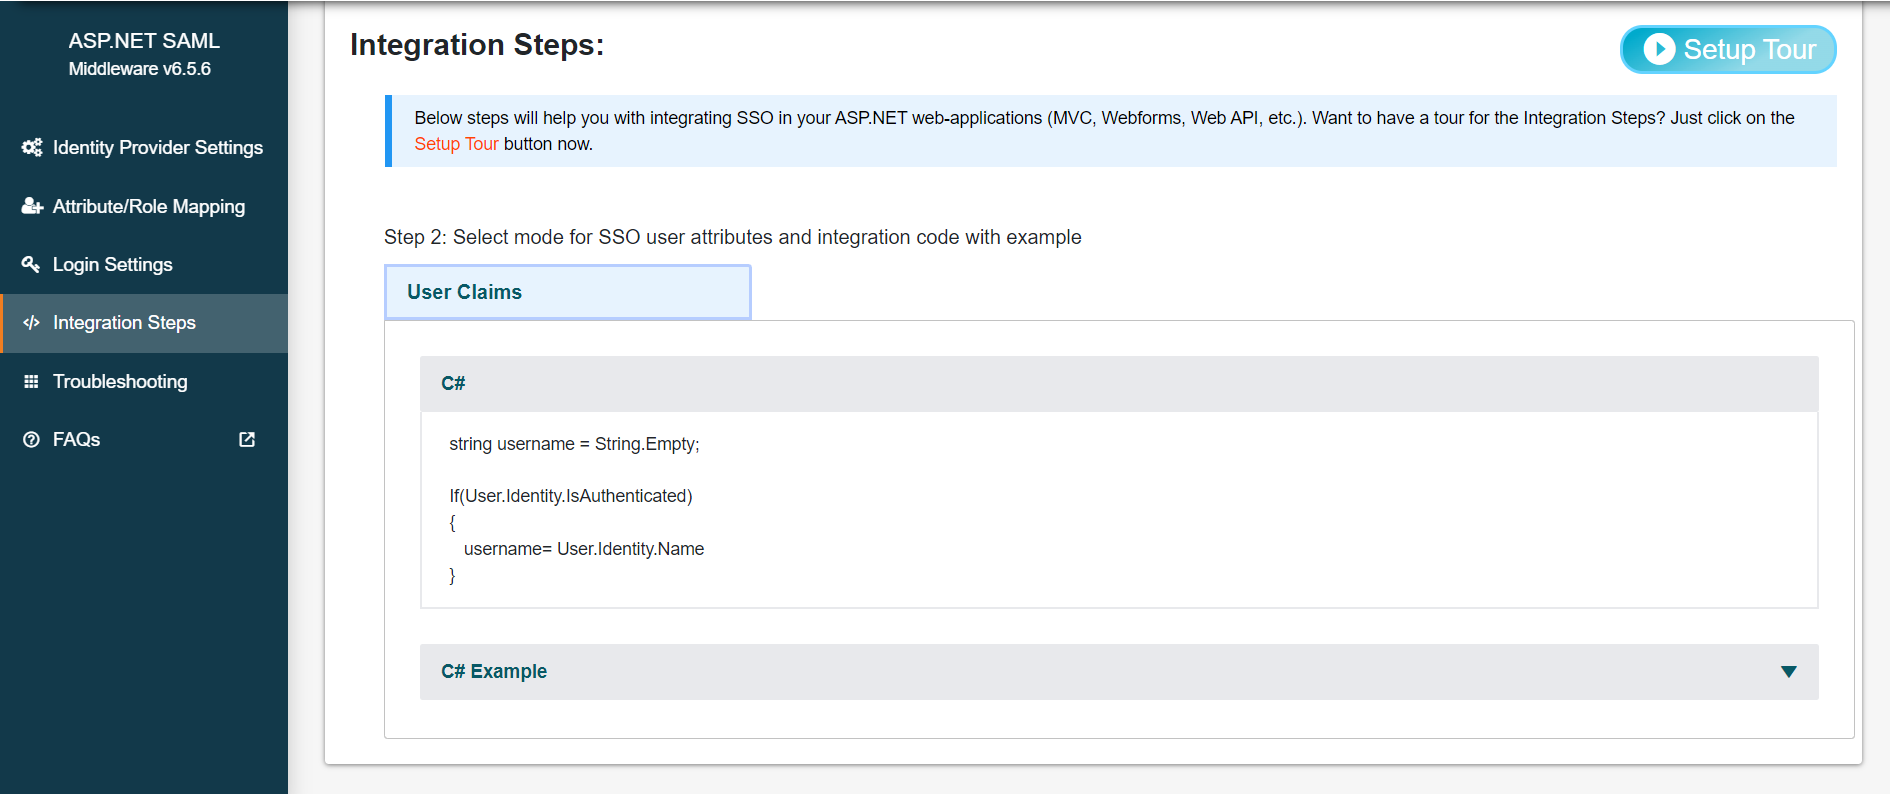
- Note: With the trial middleware the authenticated user details are stored in user claims using the default .NET Cookie Authentication. Support of setting user claims using Header-based, Session-based, JWT-based authentication is available in our premium plugin.
- You can also copy the integration code from below:
          string name="";

          string claimtype="";

          string claimvalue="";


          if(User.Identity.IsAuthenticated)


          {


            foreach(var claim in User.claims)


           {


             claimtype = claim.Type;


             claimvalue = claim.Value;


           }


           //retrive custom attributes(for eg. Retrieve Mapped 'mobileNumber' attribute of your IDP)


           var identity = (ClaimsIdentity)User.Identity;


           IEnumerable claims = identity.claims;


           string mobileNumber = identity.FindFirst("mobileNumber")?.Value;


         }
- These steps allow you to retrieve the SSO user information in your application in the form of user claims.
- Simply copy and paste the code snippet wherever you want to access the user attributes.

- You can also copy the integration code from below:
          string name="";

          string claimtype="";

          string claimvalue="";


          if(User.Identity.IsAuthenticated)


          {


            foreach(var claim in User.claims)


           {


             claimtype = claim.Type;


             claimvalue = claim.Value;


           }


           //retrive custom attributes(for eg. Retrieve Mapped 'mobileNumber' attribute of your IDP)


           var identity = (ClaimsIdentity)User.Identity;


           IEnumerable claims = identity.claims;


           string mobileNumber = identity.FindFirst("mobileNumber")?.Value;


         }
7. Login Settings
- Hover on Select Actions and click on Copy SSO Link.

- Use the following URL as a link in the application from where you want to perform SSO:
https://<asp.net-middleware-base-url>/?ssoaction=login
- For example, you can use it as:
                      <a href="https://<asp.net-middleware-base-url>/?ssoaction=login">Log
                    in</a>
8. Logout Settings
- Use the following URL as a link to your application from where you want to perform SLO:
https://<asp.net-middleware-base-url>/?ssoaction=logout
- For example, you can use it as:
                      <a href="https://<asp.net-middleware-base-url>/?ssoaction=logout">Log
                    out</a>
- Use the following URL as a link to your application from where you want to perform SLO:
https://<asp.net-middleware-base-url>/?ssoaction=logout
- For example, you can use it as:
                      <a href="https://<asp.net-middleware-base-url>/?ssoaction=logout">Log
                    out</a>
Advanced Settings
If you want to apply Advanced Settings, navigate to the Advanced Settings tab.
Auto Redirect to IdP
- Enable the Auto Redirect to IdP toggle button to automatically redirect users to the configured Identity Provider during login.
- Select the IDP where you want to redirect the users from the specific Url in the Default IDP dropdown.
- Choose the Type of Redirection as Restricted or Public based on your requirement.
- If required, enter the URLs that should be excluded from redirection in the Exclude URLs field, separated by commas.
- Click on Save to store the configuration successfully.

Disable Admin Dashboard
- Enable the Disable Admin Dashboard toggle to hide the miniOrange Admin Dashboard, and click on Save to apply the changes.

Certificate Information
- Navigate to the Certificate Information section and select the required Certificate Type (Signing Certificate or Encryption Certificate).
- Click on Regenerate Certificate if you want to generate a new certificate.

- Then click on Apply New Certificate to apply the updated certificate.
Upload Custom Certificate
- Navigate to the Upload Custom Certificate section and select the required Certificate Type (Signing Certificate or Encryption Certificate).
- Click on Choose File to upload the Public Key (.crt) and Private Key (.pfx) files, and enter the Private Key Password in the provided field.
- After providing the required details, click on Save to upload and apply the custom certificate successfully.

Related Articles
Thank you for your response. We will get back to you soon.
Something went wrong. Please submit your query again


