Guide to Configure Umbraco SAML SSO using WordPress as IDP
Overview
Umbraco SAML Single Sign-On (SSO) plugin gives the ability to enable SAML Single Sign-On for your Umbraco applications. Using Single Sign-On you can use only one password to access your Umbraco application and services. Our plugin is compatible with all the SAML compliant Identity providers. Here we will go through a step-by-step guide to configure Single Sign-On (SSO) between Umbraco and WordPress considering WordPress as IdP.
Select your umbraco version to configure SSO with:
Pre-requisites : Download And Installation
- Install from NuGet store
- Manual Installation
- Install from NuGet store
- Manual Installation
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 9.2.3
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 9.2.3
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your startup.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the startup.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;


          namespace Application

          {

            public class Startup

            {


              // Add services to the container.

              public void ConfigureServices(IServiceCollection services)

              {

                services.AddUmbraco(_env, _config)

                  .AddBackOffice()

                  .AddWebsite()

                  .AddComposers()

                  .Build();


                services.AddminiOrangeServices(Assembly.GetExecutingAssembly());

              }


              public void Configure(IApplicationBuilder app, IWebHostEnvironment env)

              {

                if (env.IsDevelopment())

                {

                  app.UseDeveloperExceptionPage();

                }

                app.UseUmbraco()

                  .WithMiddleware(u =>

                  {

                    u.UseBackOffice();

                    u.UseWebsite();

                    u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

                  })

                  .WithEndpoints(u =>

                  {

                    u.UseInstallerEndpoints();

                    u.UseBackOfficeEndpoints();

                    u.UseWebsiteEndpoints();

                  });

              }

            }

          }
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 10.2.3
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 10.2.3
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your startup.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the startup.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;


          namespace Application

          {

            public class Startup

            {


              // Add services to the container.

              public void ConfigureServices(IServiceCollection services)

              {

                services.AddUmbraco(_env, _config)

                  .AddBackOffice()

                  .AddWebsite()

                  .AddComposers()

                  .Build();


                services.AddminiOrangeServices(Assembly.GetExecutingAssembly());

              }


              public void Configure(IApplicationBuilder app, IWebHostEnvironment env)

              {

                if (env.IsDevelopment())

                {

                  app.UseDeveloperExceptionPage();

                }

                app.UseUmbraco()

                  .WithMiddleware(u =>

                  {

                    u.UseBackOffice();

                    u.UseWebsite();

                    u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

                  })

                  .WithEndpoints(u =>

                  {

                    u.UseInstallerEndpoints();

                    u.UseBackOfficeEndpoints();

                    u.UseWebsiteEndpoints();

                  });

              }

            }

          }
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 11.2.3
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 11.2.3
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your program.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the program.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;

          WebApplicationBuilder builder = WebApplication.CreateBuilder(args);


          builder.CreateUmbracoBuilder()

            .AddBackOffice()

            .AddWebsite()

            .AddDeliveryApi()

            .AddComposers()

            .Build();


          // Add services to the container.

          builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


          WebApplication app = builder.Build();


          await app.BootUmbracoAsync();


          app.UseUmbraco()

            .WithMiddleware(u =>

            {

              u.UseBackOffice();

              u.UseWebsite();

              u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

            })

            .WithEndpoints(u =>

            {

              u.UseBackOfficeEndpoints();

              u.UseWebsiteEndpoints();

            });

          await app.RunAsync();
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 12.2.3
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 12.2.3
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your program.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the program.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;

          WebApplicationBuilder builder = WebApplication.CreateBuilder(args);


          builder.CreateUmbracoBuilder()

            .AddBackOffice()

            .AddWebsite()

            .AddDeliveryApi()

            .AddComposers()

            .Build();


          // Add services to the container.

          builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


          WebApplication app = builder.Build();


          await app.BootUmbracoAsync();


          app.UseUmbraco()

            .WithMiddleware(u =>

            {

              u.UseBackOffice();

              u.UseWebsite();

              u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

            })

            .WithEndpoints(u =>

            {

              u.UseBackOfficeEndpoints();

              u.UseWebsiteEndpoints();

            });

          await app.RunAsync();
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 13.2.3
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 13.2.3
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your program.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the program.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;

          WebApplicationBuilder builder = WebApplication.CreateBuilder(args);


          builder.CreateUmbracoBuilder()

            .AddBackOffice()

            .AddWebsite()

            .AddDeliveryApi()

            .AddComposers()

            .Build();


          // Add services to the container.

          builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


          WebApplication app = builder.Build();


          await app.BootUmbracoAsync();


          app.UseUmbraco()

            .WithMiddleware(u =>

            {

              u.UseBackOffice();

              u.UseWebsite();

              u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

            })

            .WithEndpoints(u =>

            {

              u.UseBackOfficeEndpoints();

              u.UseWebsiteEndpoints();

            });

          await app.RunAsync();
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 14.2.3
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 14.2.3
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your program.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the program.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;

          WebApplicationBuilder builder = WebApplication.CreateBuilder(args);


          builder.CreateUmbracoBuilder()

            .AddBackOffice()

            .AddWebsite()

            .AddDeliveryApi()

            .AddComposers()

            .Build();


          // Add services to the container.

          builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


          WebApplication app = builder.Build();


          await app.BootUmbracoAsync();


          app.UseUmbraco()

            .WithMiddleware(u =>

            {

              u.UseBackOffice();

              u.UseWebsite();

              u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

            })

            .WithEndpoints(u =>

            {

              u.UseBackOfficeEndpoints();

              u.UseWebsiteEndpoints();

            });

          await app.RunAsync();
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 15.2.4
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 15.2.4
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your program.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the program.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;

          WebApplicationBuilder builder = WebApplication.CreateBuilder(args);


          builder.CreateUmbracoBuilder()

            .AddBackOffice()

            .AddWebsite()

            .AddDeliveryApi()

            .AddComposers()

            .Build();


          // Add services to the container.

          builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


          WebApplication app = builder.Build();


          await app.BootUmbracoAsync();


          app.UseUmbraco()

            .WithMiddleware(u =>

            {

              u.UseBackOffice();

              u.UseWebsite();

              u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

            })

            .WithEndpoints(u =>

            {

              u.UseBackOfficeEndpoints();

              u.UseWebsiteEndpoints();

            });

          await app.RunAsync();
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 16.2.4
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 16.2.4
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your program.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the program.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;

          WebApplicationBuilder builder = WebApplication.CreateBuilder(args);


          builder.CreateUmbracoBuilder()

            .AddBackOffice()

            .AddWebsite()

            .AddDeliveryApi()

            .AddComposers()

            .Build();


          // Add services to the container.

          builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


          WebApplication app = builder.Build();


          await app.BootUmbracoAsync();


          app.UseUmbraco()

            .WithMiddleware(u =>

            {

              u.UseBackOffice();

              u.UseWebsite();

              u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

            })

            .WithEndpoints(u =>

            {

              u.UseBackOfficeEndpoints();

              u.UseWebsiteEndpoints();

            });

          await app.RunAsync();
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 17.2.4
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 17.2.4
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your program.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the program.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;

          WebApplicationBuilder builder = WebApplication.CreateBuilder(args);


          builder.CreateUmbracoBuilder()

            .AddBackOffice()

            .AddWebsite()

            .AddDeliveryApi()

            .AddComposers()

            .Build();


          // Add services to the container.

          builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


          WebApplication app = builder.Build();


          await app.BootUmbracoAsync();


          app.UseUmbraco()

            .WithMiddleware(u =>

            {

              u.UseBackOffice();

              u.UseWebsite();

              u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

            })

            .WithEndpoints(u =>

            {

              u.UseBackOfficeEndpoints();

              u.UseWebsiteEndpoints();

            });

          await app.RunAsync();
- Run the application when the configuration is done.
PM> NuGet\Install-Package miniOrange.Umbraco.SAML.SSO.Login -Version 18.0.0
> dotnet add package miniOrange.Umbraco.SAML.SSO.Login --version 18.0.0
- Download Umbraco SAML Single Sign-On (SSO) middleware.
- For Setting up the middleware, you will be required to add the below namespaces, services and middleware in your program.cs file (marked in green), below here is a sample example.
Include only the highlighted section below in the program.cs file of your application.
          using miniOrange.saml;

          using System.Reflection;

          WebApplicationBuilder builder = WebApplication.CreateBuilder(args);


          builder.CreateUmbracoBuilder()

            .AddBackOffice()

            .AddWebsite()

            .AddDeliveryApi()

            .AddComposers()

            .Build();


          // Add services to the container.

          builder.Services.AddminiOrangeServices(Assembly.GetExecutingAssembly());


          WebApplication app = builder.Build();


          await app.BootUmbracoAsync();


          app.UseUmbraco()

            .WithMiddleware(u =>

            {

              u.UseBackOffice();

              u.UseWebsite();

              u.AppBuilder.UseminiOrangeSAMLSSOMiddleware();

            })

            .WithEndpoints(u =>

            {

              u.UseBackOfficeEndpoints();

              u.UseWebsiteEndpoints();

            });

          await app.RunAsync();
- Run the application when the configuration is done.
Configuration Steps
Step by Step guide for Umbraco SAML SSO using WordPress as Identity Provider.
1. Access the Umbraco SAML Plugin Dashboard
- After integration, open your browser and browse the connector dashboard with the URL below:
https://<umbraco-base-url>/?ssoaction=config
- If the registration page or login page pops up, you have successfully added the miniOrange SAML SSO middleware in your application.

- Register or log in with your account by clicking the Register button to configure the middleware.
- After successful registration, you will receive a trial license key on your registered email address.
- To activate the middleware, you can either:
- Enter the license key received via email in the provided input field.
- Upload the license file that you downloaded by clicking on the Click Here button.
OR

- Then, check the box "I have read the above conditions and I want to activate the middleware", and click the Activate License button.

2. Provide Umbraco Application Metadata to WordPress Identity Provider
There are two ways detailed below with which you can get the SAML SP metadata to configure onto your Identity Provider end.
A] Using SAML metadata URL or metadata file
- In the Plugin Settings menu, look for Service Provider Settings. Under that, you can find the metadata URL as well as the option to download the SAML metadata.
- Copy metadata URL or download the metadata file to configure the same on your identity provider end.
- You may refer to the screenshot below:

B] Uploading metadata manually
- From the Service Provider Settings section, you can manually copy the service provider metadata like SP Entity ID, ACS URL, Single Logout URL and share it with your identity provider for configuration.
- You may refer to the screenshot below:

- Go to the WordPress IDP plugin, navigate to the Service Provider tab.
- Enter the values corresponding to the information from the Service Provider. Refer to the table below.
| Service Provider Name | Name of your Service Provider. |
| SP Entity ID or Issuer | Copy and paste the SP-EntityID from the Service Provider |
| ACS URL | Copy and paste the ACS URL from the Service Provider. |
| NameID Format | urn:oasis:names:tc:SAML:1.1:nameid-format:emailAddress |
| Assertion Signed | Checked |
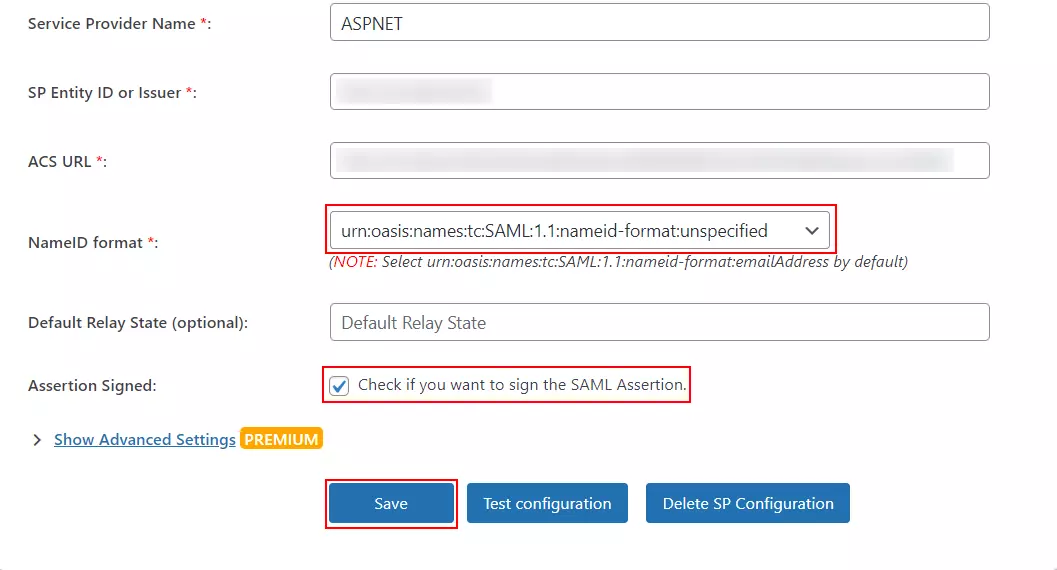
- Click on the Save button to save your configurations.
- Go to the IDP Metadata tab. Here you can find information for configuring the Service Provider.
- You can also download the metadata XML file, by clicking on the download link.
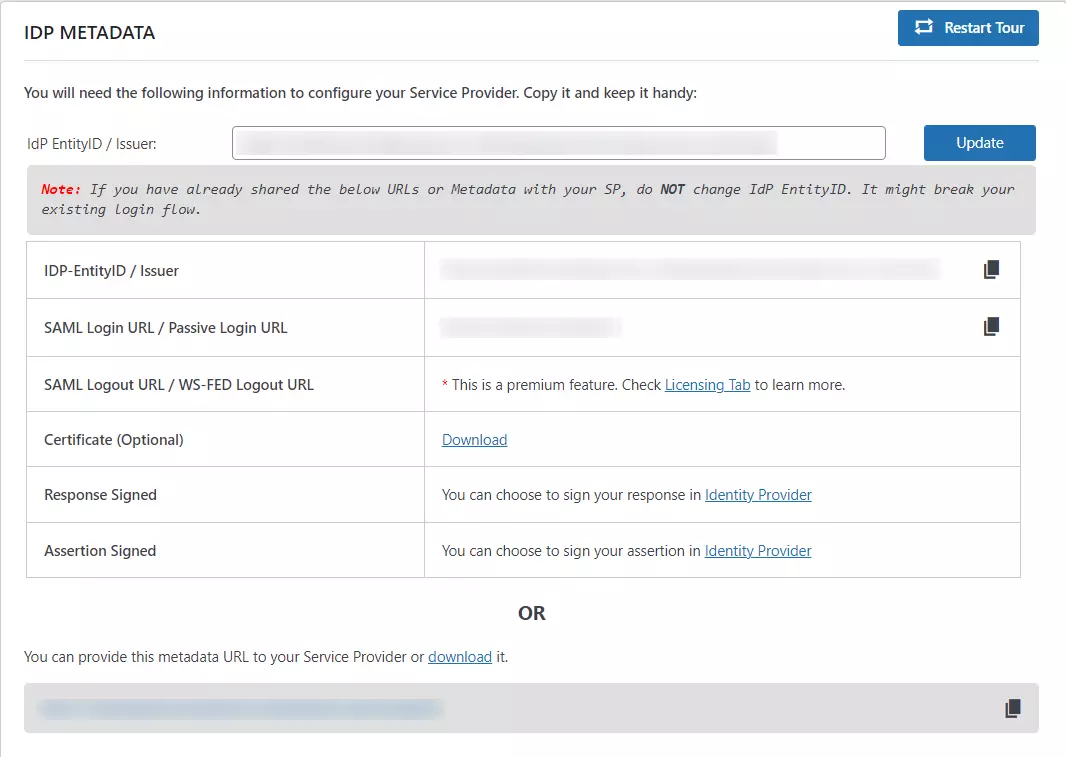
You have successfully configured WordPress as SAML IDP (Identity Provider) for achieving Umbraco Single Sign-On (SSO).
3. Configure WordPress Identity Provider Metadata in Umbraco Application
- Click on the Add new IDP button to configure a new Identity Provider.

- Under the Plugin Settings tab, select WordPress as your identity provider from the list shown.
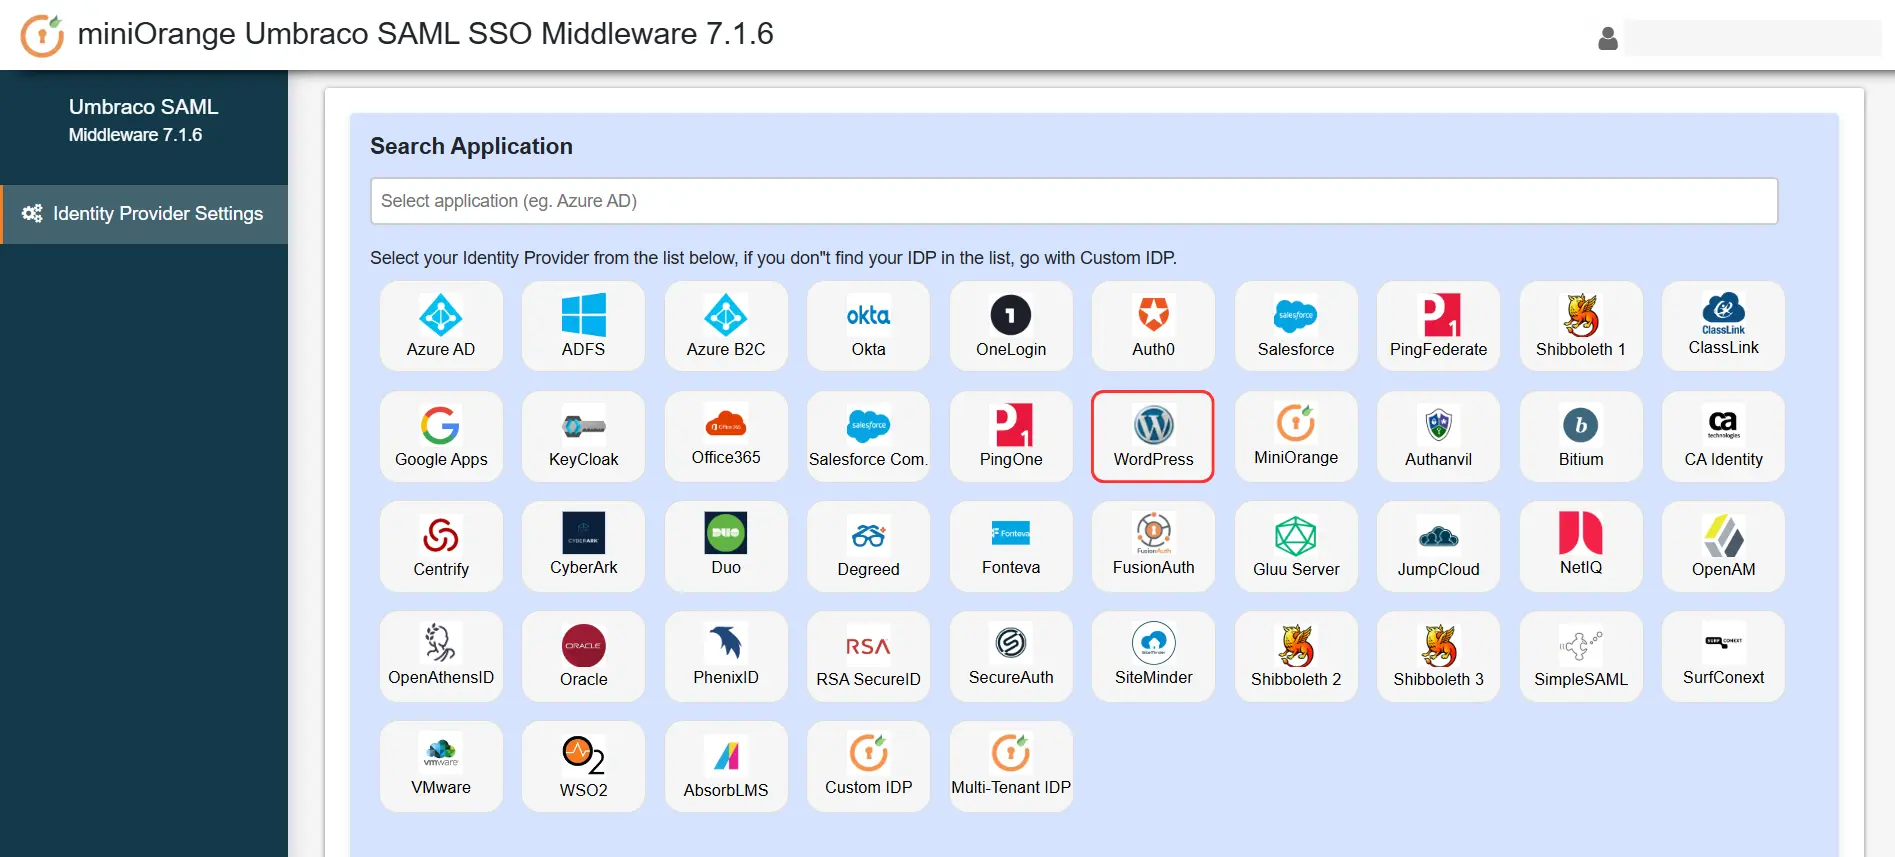
There are two ways detailed below with which you can configure your SAML Identity Provider metadata in the middleware.
A] Upload metadata using the Upload IDP Metadata button:
- If your identity provider has provided you with the metadata URL or metadata file (.xml format only), then you can simply configure the identity provider metadata in the middleware using the Upload IDP Metadata option.
- Copy metadata URL or download the metadata file to configure the same on your identity provider end.
- You may refer to the screenshot below:

- You can choose any one of the options according to the metadata format you have available.
B] Configure the identity provider metadata manually:
- After configuring your Identity Provider, it will provide you with IDP Entity ID, IDP Single Sign On URL and SAML X509 Certificate fields respectively.
- Click Save to save your IDP details.

4. Testing SAML SSO
- After uploading the metadata details, navigate to the Identity Provider Settings section. Hover over the Select Actions dropdown and click on Test Configuration.

- The screenshot below shows a successful result. Click on SSO Integration to further continue with the SSO Integration.

- If you are experiencing any error on the middleware end you’ll be shown with the window similar to below.
- To troubleshoot the error you can follow the below steps:
- Under Troubleshoot tab, enable the toggle to receive the plugin logs.

- Once enabled, you will be able to retrieve plugin logs by navigating to Plugin Settings tab and clicking on Test Configuration.
- Download the log file from the Troubleshoot tab to see what went wrong.
- You can share the log file with us at umbracosupport@xecurify.com and our team will reach out to you to resolve your issue.
Umbraco Login Type
- After this, select the Login Type from the dropdown on the right side of the Identity Provider Settings page.
- You can choose from BackOffice, Member, or Custom Attribute based.
- Note: The Custom Attribute based login type is available in the Premium and Enterprise versions.

5. Attribute Mapping
- Attribute Mapping, Role Mapping and Domain Restriction are available in the Premium and Enterprise versions of the middleware.

6. Login Settings
- Hover on Select Actions and click on Copy SSO Link.

- Use the following URL as a link in the application from where you want to perform SSO:
https://<umbraco-base-url>/?ssoaction=login
- For example, you can use it as:
<a href="https://<umbraco-base-url>/?ssoaction=login">Log in</a>
7. Logout Settings
- Use the following URL as a link to your application from where you want to perform SLO:
https://<umbraco-base-url>/?ssoaction=logout
- For example, you can use it as:
<a href="https://<umbraco-base-url>/?ssoaction=logout">Log out</a>
Related Articles
Thank you for your response. We will get back to you soon.
Something went wrong. Please submit your query again


